Stay SOC 2 compliant all year
SOC 2 examines service-company controls against AICPA criteria in an independent CPA firm's audit.
SOC 2 compliance means controls keep working
ZeroTB keeps your compliance controls working after the audit. Our software and team support the commitments in your SOC 2, ISO 27001 and HIPAA programs as your company changes.
We serve US software, AI, fintech and healthtech companies with 25 to 250 people.
Set the scope. Trust Services Criteria require security. Commitments determine availability, processing integrity, confidentiality and privacy coverage
Understand the period. Type 1 covers design on one date. Type 2 tests operation, usually over a 3 to 12 month observation period. Customers generally consider reports current for about 12 months
Support customer reviews. Customers ask for SOC 2 reports in security reviews, although SOC 2 is voluntary
SOC 2 requirements fall into nine control areas
CC1
Control environment (5 criteria)
Leaders assign control responsibilities, set expected conduct and oversee the people doing the work.
CC2
Information and communication (3 criteria)
People need reliable information to run controls and explain their responsibilities to others.
CC3
Risk assessment (4 criteria)
Risk assessments examine fraud, business changes and other threats to company objectives.
CC4
Monitoring activities (2 criteria)
Evaluations establish whether controls work and give owners the gaps they need to address.
CC5
Control activities (3 criteria)
Policies and procedures put selected controls into practice to address risks.
CC6
Access controls (8 criteria)
Controls protect logical and physical access as accounts, permissions, equipment and data change.
CC7
System operations (5 criteria)
Teams investigate unusual activity and vulnerabilities, respond to incidents and restore affected systems.
CC8
Change management (1 criterion)
System and code changes pass through approval and testing before deployment.
CC9
Risk mitigation (2 criteria)
Continuity plans address business interruptions, while vendor reviews address risks from business partners.
Broken controls cost clean SOC 2 reports
Retained access breaks CC6 commitments. A missing review rule breaks CC8 commitments while the report still describes working controls.
A Type 2 test finds an exception, an enterprise deal stalls in security review, and the team repeats its investigation and evidence gathering.
A contractor leaves
Offboarding misses an account
Former contractor retains access
ZeroTB checks SOC 2 controls daily between audits
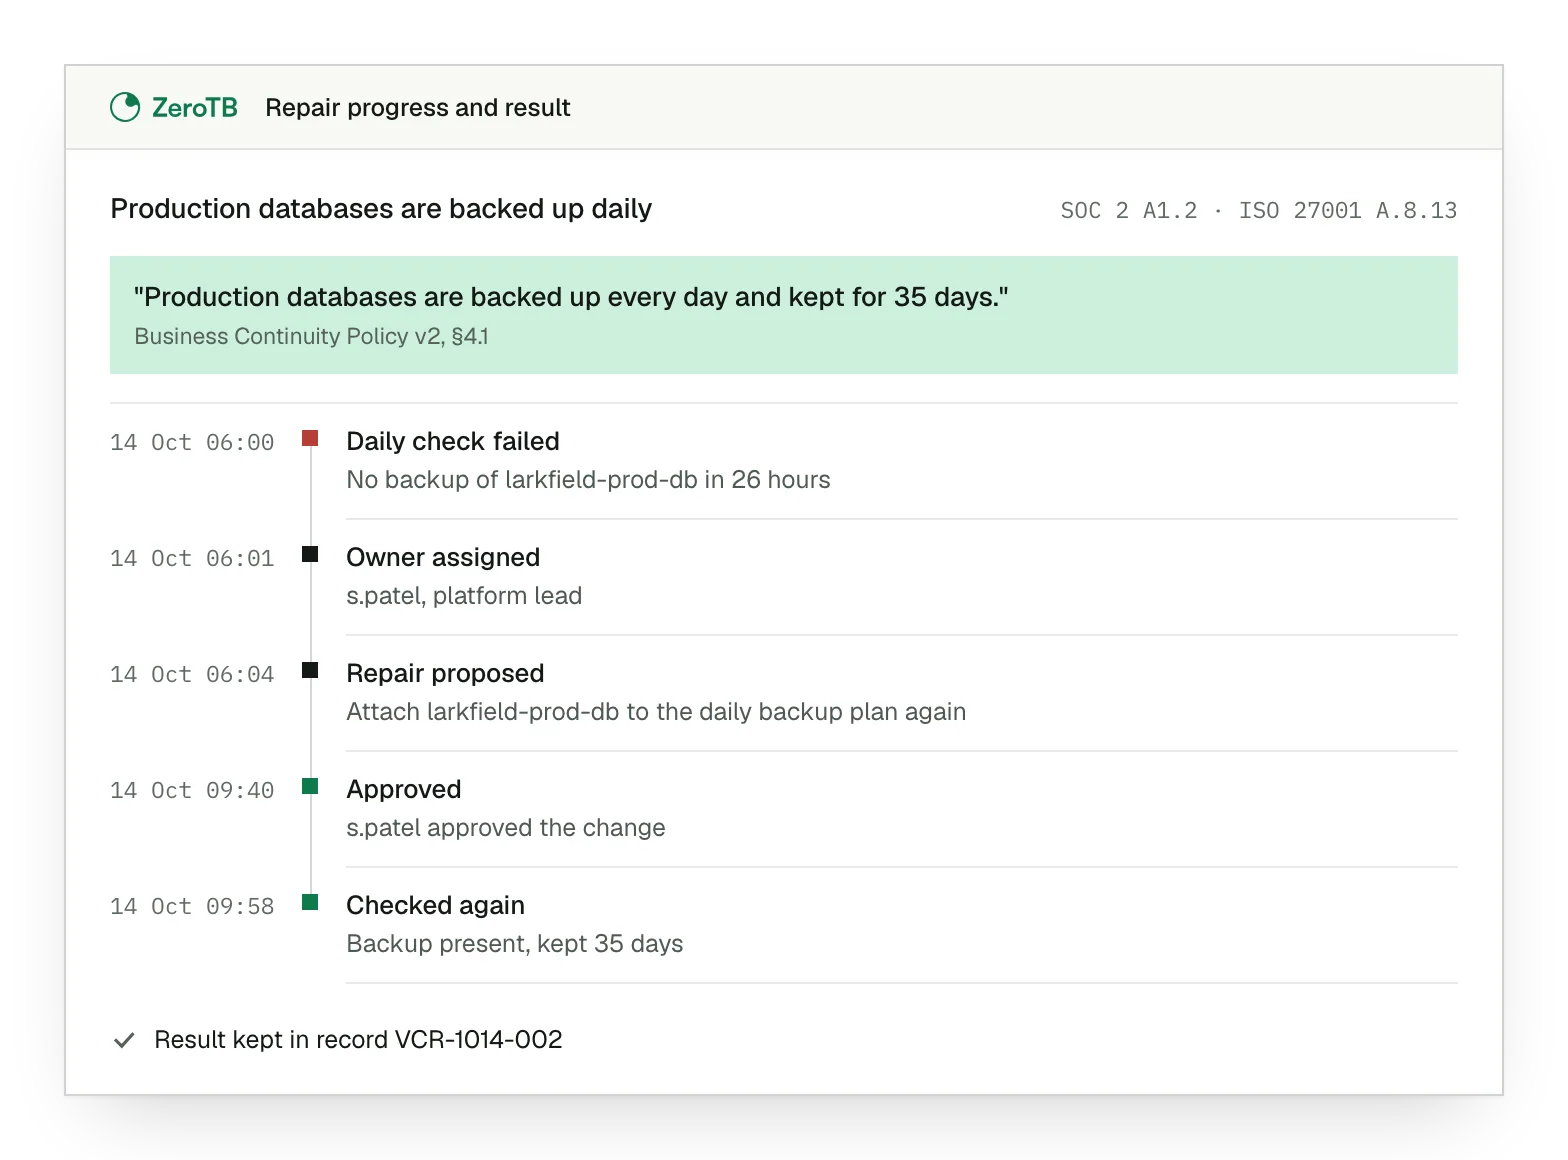
ZeroTB reads your SOC 2 report and policies into commitments your team approves line by line, then checks systems daily, starting read-only.
Prepare the repair. Our team drafts runbooks, pull requests, API actions or guardrails for each gap
Approve material changes. Your team authorizes repairs before ZeroTB rechecks the control and signs its evidence
Reuse completed work. A Verified Control Record can support several frameworks when the control meets their requirements
Only an independent CPA firm audits SOC 2
An independent CPA firm provides SOC 2 audit services and issues the SOC 2 report. ZeroTB neither audits nor promises audit success.
Auditors read the Verified Control Record in ZeroTB. They decide whether continuous records are sufficient and appropriate, agreeing source, reliability and period.
ZeroTB fixes SOC 2 gaps beside your consultant
A SOC 2 compliance consultant can advise your program while ZeroTB handles daily control work. You can continue working with your consultant.
| Task | Your GRC platform | A consultant | ZeroTB |
|---|---|---|---|
| Program scope | Records agreed scope | Helps define scope and controls | Works from your report's commitments |
| Evidence | Collects and organizes evidence | Reviews evidence in engagement | Signed records of completed repairs |
| Recurring checks | Tracks control status | Scheduled reviews | Daily checks against commitments |
| Control gaps | Tracks findings and tasks | Investigates or fixes when engaged | Carries gaps to verified restoration |
Talk to our team
Talk with us about the SOC 2 controls your team keeps chasing and the work it takes to keep them running.
FAQ
Is SOC 2 legally required?
SOC 2 is voluntary. Customers often ask for a report before they buy, as part of their security review.
Which Trust Services categories should we include?
Security belongs in every SOC 2 report. Add availability, processing integrity, confidentiality or privacy where your service commitments require them, and agree scope with your auditor.
Which SOC 2 controls break first when engineers use coding agents?
Access, system operations and change management under CC6, CC7 and CC8 need review where coding agents reach. Start with the agent's permissions and affected systems.
Can one control support both SOC 2 and ISO 27001?
One control can support SOC 2 and ISO 27001 when it meets both requirements. Approved work accounts are one example. ISO A.5.15 maps to CC6.1.
Who takes part in ongoing SOC 2 control work?
Requirement and system owners participate in SOC 2 control work. Compliance confirms commitments, IT or engineering reviews changes, and your team retains material decisions and exceptions.
What system access does ZeroTB need?
ZeroTB starts read-only. Write access is scoped per approved action class and revocable. Pull requests are the default. Direct API actions are opt-in and reversible.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments, verifies repairs to two real control gaps, and provides portable evidence records.
Keeping your commitments working every day
ZeroTB checks your commitments against your systems each day and carries detected gaps through to verified restoration. The same responsibility continues as the company changes.
Confirm requirements
AI identifies commitments in your report and policies for your team to confirm, including scope and required evidence.
Check daily
ZeroTB compares requirements with system state daily, showing the source clause, observation and reason for each finding.
Prepare repairs
Each gap gets an owner and response window before ZeroTB prepares a runbook, pull request, API action or guardrail.
Authorize changes
Your team authorizes material changes before the responsible person or ZeroTB executes the repair within agreed permissions.
Verify and record
You receive verified restoration and a signed record of the commitment, before-and-after states, action, approval and verification.