Pass ISO 27001 surveillance audits without findings
The ISO 27001 standard defines requirements for an information security management system (ISMS).
ISO 27001 standard requires a managed security program
ISO 27001 requires companies to assess risks, choose controls and examine whether they work. ZeroTB combines software and hands-on support to maintain those controls for US software companies with 25 to 250 people.
Manage the program. Clauses 4 to 10 cover scope, leadership, risk treatment, resources, evaluation and improvement
Examine the system. Internal audits and management reviews examine how the ISMS works
Maintain certification. An accredited certification body certifies the ISMS, then checks it through surveillance audits
Annex A groups 93 controls into four themes
Organizational controls
A.5 has 37 controls covering security responsibilities, suppliers and incident preparation.
People controls
Eight controls cover employment responsibilities, security awareness, reporting concerns and duties after leaving.
Physical controls
A.7 has 14 controls protecting premises and equipment, including entry and environmental safeguards.
Technological controls
A.8.1 to A.8.34 cover 34 controls over access, configuration and software security.
Risk treatment decides which Annex A controls apply
Your risk treatment decisions determine which Annex A controls you need. The Statement of Applicability (SoA) records those choices and whether each control is implemented.
Compare against Annex A for omissions. Explain inclusions and justify exclusions in the SoA. ISO 27002 guides implementation.
Drifted controls become findings at surveillance audits
A new repository lacks the review rule that passed the last audit. Unreviewed changes reach production before the next ISO 27001 surveillance audit finds them.
Compliance has to reconstruct the repair history from screenshots and messages to show what happened.
A repository is created
Required review is omitted
Unreviewed changes reach production
ZeroTB checks controls daily and verifies each repair
ZeroTB starts ISO 27001 monitoring read-only. We confirm policy and Statement of Applicability commitments with your team, then check systems against them daily.
Prepare approved repairs. We draft runbooks, pull requests, API actions or guardrails. People approve material changes
Carry recurring work. We schedule training, vendor reviews and policy reviews, escalating overdue tasks
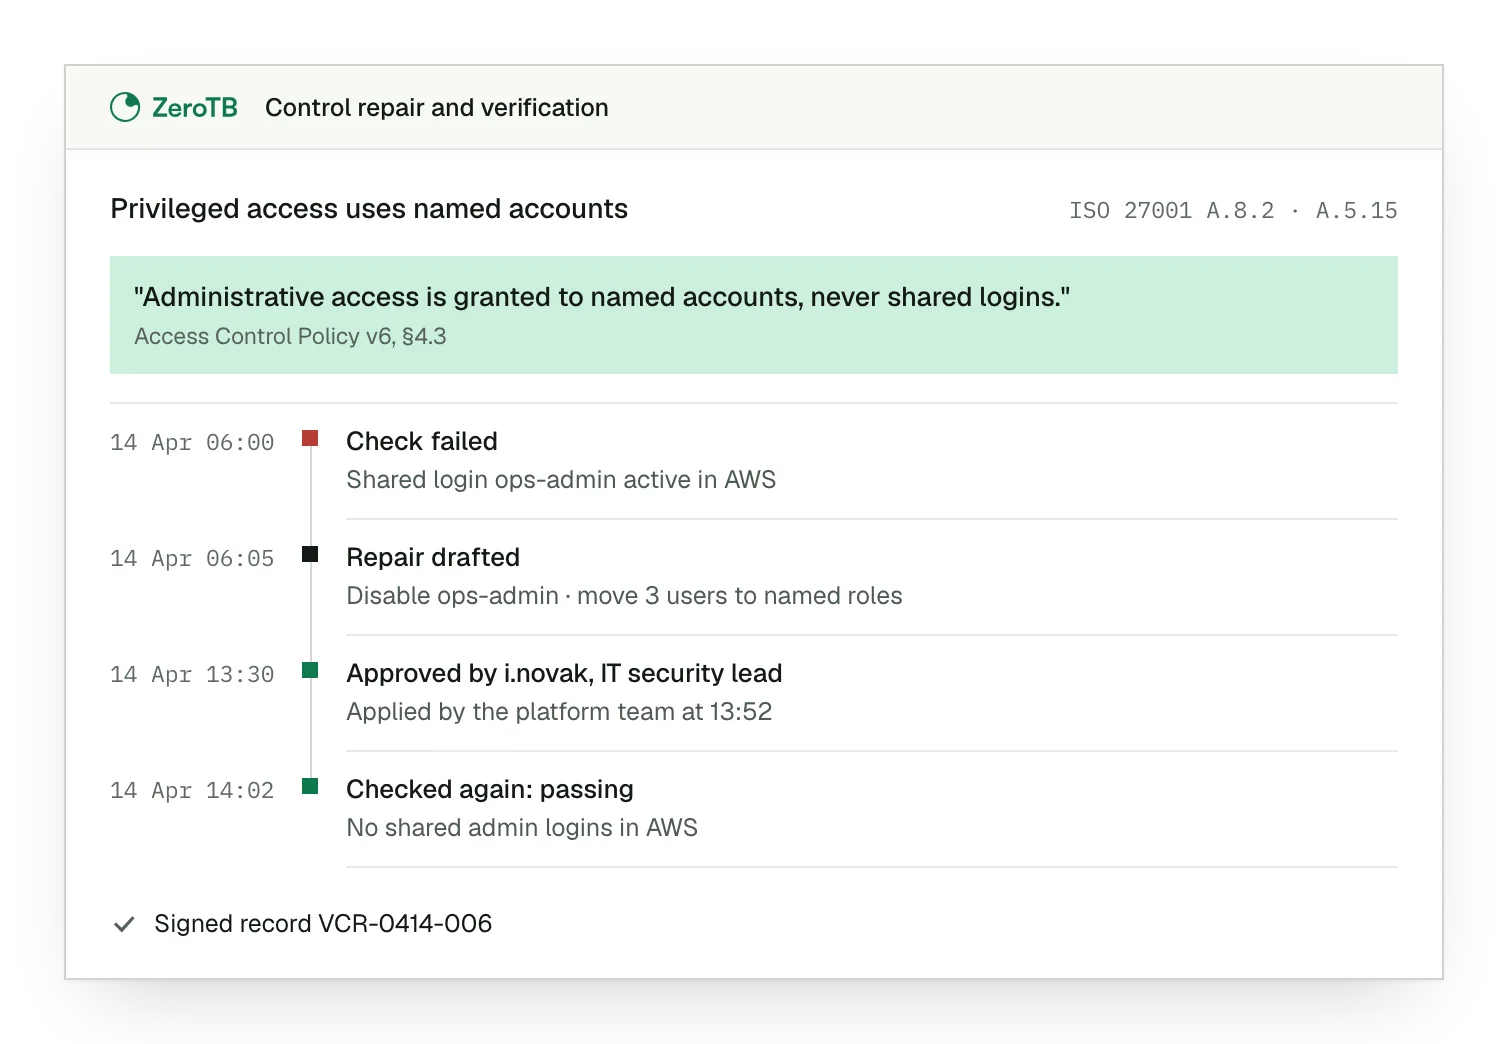
Verify each repair. We recheck the control and sign a Verified Control Record your auditor can inspect
Shared controls cover SOC 2 and ISO 27001
Existing SOC 2 controls support ISO 27001 where both programs' requirements match. ZeroTB operates shared controls, so one restoration can support both audits.
| Control | ISO 27001 Annex A | SOC 2 criterion |
|---|---|---|
| Access control | Control A.5.15 | Criterion CC6.1 |
| Access rights | Control A.5.18 | Criterion CC6.3 |
| Configuration management | Control A.8.9 | Criterion CC7.1 |
| Logging controls | Control A.8.15 | Criterion CC7.2 |
| Change management | Control A.8.32 | Criterion CC8.1 |
Talk to our team
Discuss where ISO 27001 control gaps keep returning and the repair work your team needs between audits.
FAQ
Is ISO 27001 a certification?
ISO 27001 is a standard for ISMS certification. An accredited certification body audits conformity, issues certification and conducts surveillance audits. We do not perform audits.
Can daily monitoring replace an ISO 27001 internal audit?
Daily monitoring cannot replace an ISO 27001 internal audit. The audit evaluates the whole management system. Observations of selected controls can inform that assessment.
When should our Statement of Applicability change?
Review the Statement of Applicability when scope, risks or control decisions change. Observations from systems help the program owner check whether the recorded decisions still apply.
What evidence can ZeroTB provide for a surveillance audit?
Your surveillance auditor can inspect each repair's Verified Control Record: commitment, before-and-after state, action, approval and verification. The auditor decides how that evidence serves the audit.
What access does ZeroTB need to make repairs?
Repairs start with read-only access. Write permissions cover approved action classes. Pull requests are the default for material changes. Direct API actions are opt-in, reversible and limited.
Does ZeroTB cover training and policy reviews?
Training, vendor reviews, incident exercises and policy reviews are scheduled from commitments, assigned to owners, escalated when late and verified when complete.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments and takes two gaps through verified restoration, with signed records of repairs and checks.