Continuous monitoring compares current systems and processes with the controls a company has agreed to maintain between audits. It gives the team a way to find failures while there is work to do about them. Each failure needs an owner, an approved correction and a check that establishes whether the repair succeeded.
After an audit, accounts change, new repositories appear and devices need attention. The evidence collected for the audit describes an earlier state. The ongoing question is whether those systems still meet the company's commitments, and who will act when they do not.
Checks that lead to action
A monitoring result becomes useful when someone can act on it. The check compares an observation with a defined requirement, such as the requirement to review changes before release. A failure tells the responsible team which condition needs investigation and where it occurred.
NIST's continuous monitoring guidance describes information about control effectiveness as a basis for responding to risk. An independent audit has a separate role: examining controls and evidence within its scope. The monitoring program continues to check conditions and inform responses between those examinations.
Control scope
The scope of a check must match the promise the company made. An access policy may apply to every company application. Checking the central identity system alone leaves a question about other access routes, including accounts maintained within individual applications.
A passing result needs that context. It should identify the systems covered, so the reviewer can recognize an application that was added later or remains outside the check. An approved exception also needs defined conditions; otherwise, the check cannot distinguish permitted access from a gap.
Repeatable checks across systems and processes
Automated compliance monitoring can identify changes across several parts of the working environment. Privileged accounts, device baselines, cloud settings and repository review requirements are candidates for repeatable checks. Each needs a connection to the commitment that makes the observed condition acceptable or unacceptable.
Some commitments concern work performed by people. Software can identify a late vendor review or a missing training record, but the evidence still needs to describe what happened. A reviewer must be able to decide whether the completed activity satisfies the requirement it supports.
Check frequency
The check interval determines how long a changed condition may remain unseen. For a setting affected by deployments, checking after a deployment may be appropriate. For a policy review, the relevant timing comes from when the company has committed to complete that review.
Continuous monitoring keeps these checks operating on their respective schedules between audits. Increasing frequency can give an owner earlier notice of a failure. The owner still needs an agreed response window and a way to act; otherwise, the earlier notice leaves the same gap unresolved.
Missing observations
Missing data needs a visible status of its own. When a connection stops working, the team loses its current view of the system. An earlier passing observation remains useful as history, but it cannot account for changes made after the connection failed.
Unknown, stale and disconnected tell the reviewer why a current conclusion is unavailable. The immediate work is to restore a reliable observation. A new check may then reveal a control failure, or confirm that the condition still holds. Until then, the current state remains unresolved.
The limits of a test result
Automated control testing answers the question its test was designed to answer. Checking a repository setting can establish that review is required. Checking the record of a particular release can establish whether that change received review. Both may matter to the same commitment.
This distinction affects how a team interprets compliance control testing results. The owner approves the meaning of the test and any exceptions to it. Evidence should identify the condition tested, so a reviewer can judge whether it supports the conclusion being drawn about the control.
Response ownership
Ownership has to continue beyond the person who receives the alert. The control may need a change from an application owner or an engineer before it can operate again. Someone must carry that request through to a result, with the requirement and observed gap available.
For a software company maintaining SOC 2 Type 2 controls, this work persists between audits. A continuous compliance service can handle investigation and prepare repairs across teams. Its scope needs to make the approval decision clear and identify who handles stalled work and unsuccessful corrections.
Approved changes
A repair proposal gives the owner a decision to make about the affected system. It should describe the correction and the legitimate activity that must continue afterward. In an access case, the owner needs to understand which permissions will remain and which will change.
Material changes can go through a reviewed pull request. Direct actions need agreed permissions and boundaries as well. Keeping the approval with the action allows a later reviewer to understand the decision, including why the owner retained an exception or authorized a particular correction.
Verification evidence
Closing a gap requires evidence from after the repair. The change record shows what action was taken; a new observation shows whether the intended condition now holds. If the check fails, the work continues. If data is unavailable, success has yet to be established.
The Verified Control Record connects those observations with the commitment, action and approval. This gives the reviewer the basis for accepting the repair. The same evidence from control operations lets someone examining the work later follow how the team reached its conclusion about the control.
Software evaluation through failed controls
The useful test of continuous control monitoring software is what happens to a failed control. A demonstration should make its scope and observation time visible. It should also show who owns the gap and what happens when a proposed repair fails its verification check.
The work around the software matters when assessing CCM software vendors. ZeroTB combines software and service to take commitments through verified restoration and keep the commitments, checks, repairs and evidence together. The monitoring tools guide develops the questions about coverage and continuing responsibility.
Operating measures
Coverage and freshness explain how much confidence to place in the monitoring view. Coverage identifies commitments with useful checks. Freshness shows whether their observations are current enough to support a decision. A gap in either measure points to conditions the team cannot yet judge.
Ownership and time to verified restoration concern the response. They show who is handling open gaps and how long repairs take to confirm. Repeated failures need investigation too: the recurring findings guide considers why the same condition may keep failing after an apparently successful repair.
Example of restoring repository review
In this example, a check finds that a production repository no longer requires review before release. The record gives its owner the information needed to approve a correction. After the change, another check establishes whether the required review setting has been restored.
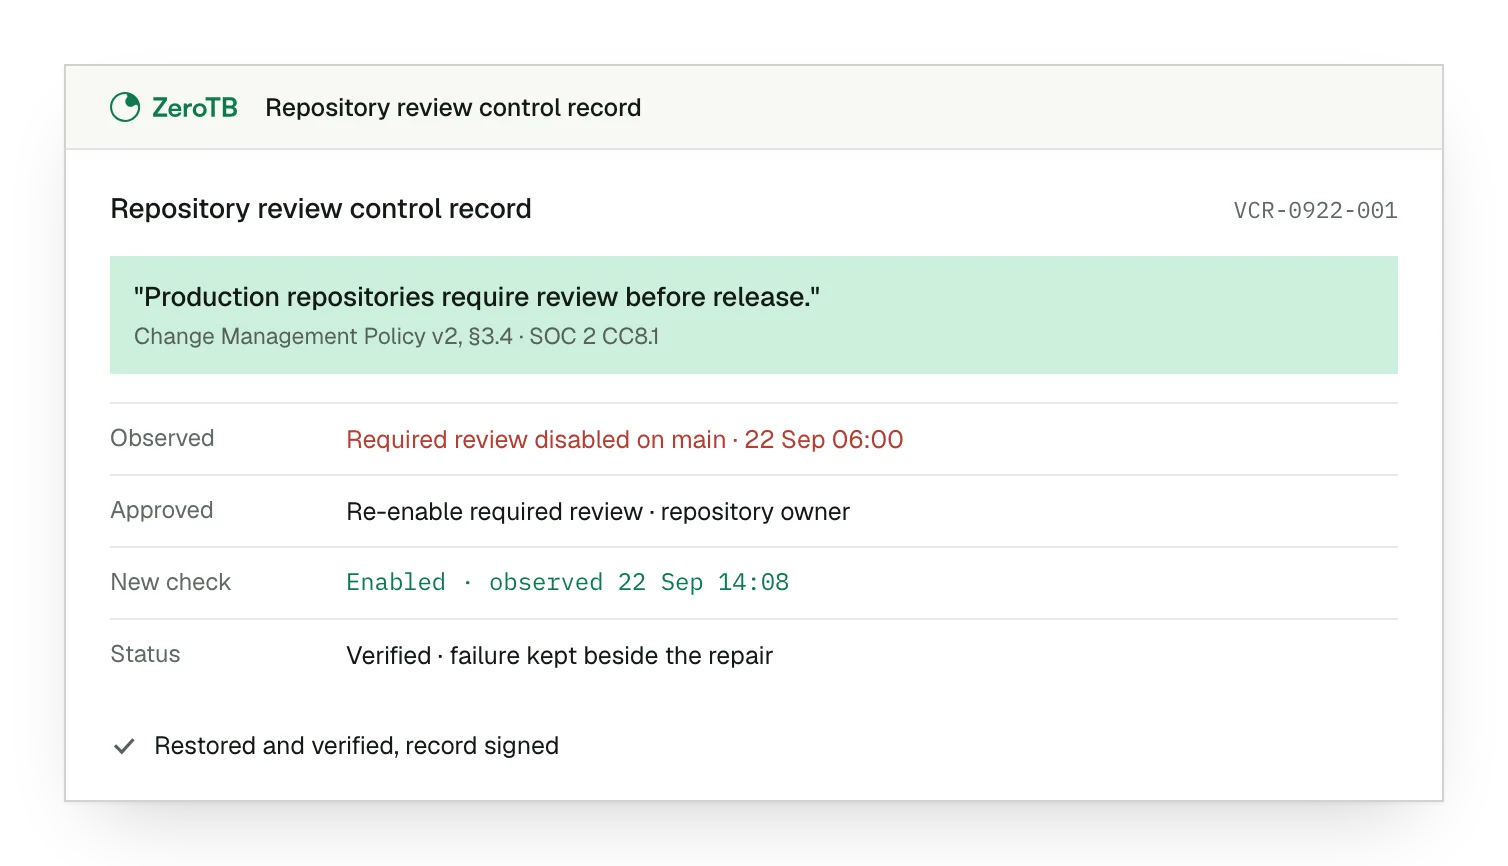
Failed review check. The observed setting permits release without review, contrary to the requirement for this production repository.
Approved setting change. The proposed correction restores required review, and the repository owner approves its effect on releases.
Verified review requirement. The dated observation after the change confirms that the repository again requires review before release.
Recorded repair evidence. The original failure remains alongside the correction, approval and successful check that support closing the gap.
Monitoring review checklist
Agree which requirement matters, where it applies and what a passing observation must establish about the affected systems.
Check whether the evidence covers the requirement and whether its age supports a decision about the current state.
Decide who can authorize the correction and who carries the work through delays, exceptions and failed checks.
Agree which resulting-state check will establish success and which evidence the reviewer needs to accept the repair.
Related pages
Coding-agent compliance
Read about keeping engineering controls working as coding agents change code and infrastructure.
Healthtech
Read about control operations for healthtech companies managing requirements across devices and work accounts.
Control operations
See what the continuing service covers between audits, from failed checks to verified repairs.
Start with the Pilot
Talk with our team about keeping controls working between audits. The eight-week Pilot maps up to 25 commitments and takes two real control gaps through approved repairs and verified restoration. The completed work includes evidence of the changes and their results.