Keeping GitHub controls working between audits
ZeroTB checks GitHub compliance commitments against branch protection, required reviews and CI gates, then prepares repairs.
Works with the stack you already run


ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA.
GitHub compliance depends on your repository settings
GitHub reports on its platform. Your team keeps repository settings compliant. ZeroTB's software and team keep those controls working after audits for US software, AI, fintech and healthtech companies.
GitHub covers GitHub. GitHub reports cover its platform's controls. Your team remains responsible for repository settings
Auditors sample merges. Auditors examine pull request approvals and the branch protection rules behind them
The period counts. Required reviews and CI gates must hold across the whole audit period
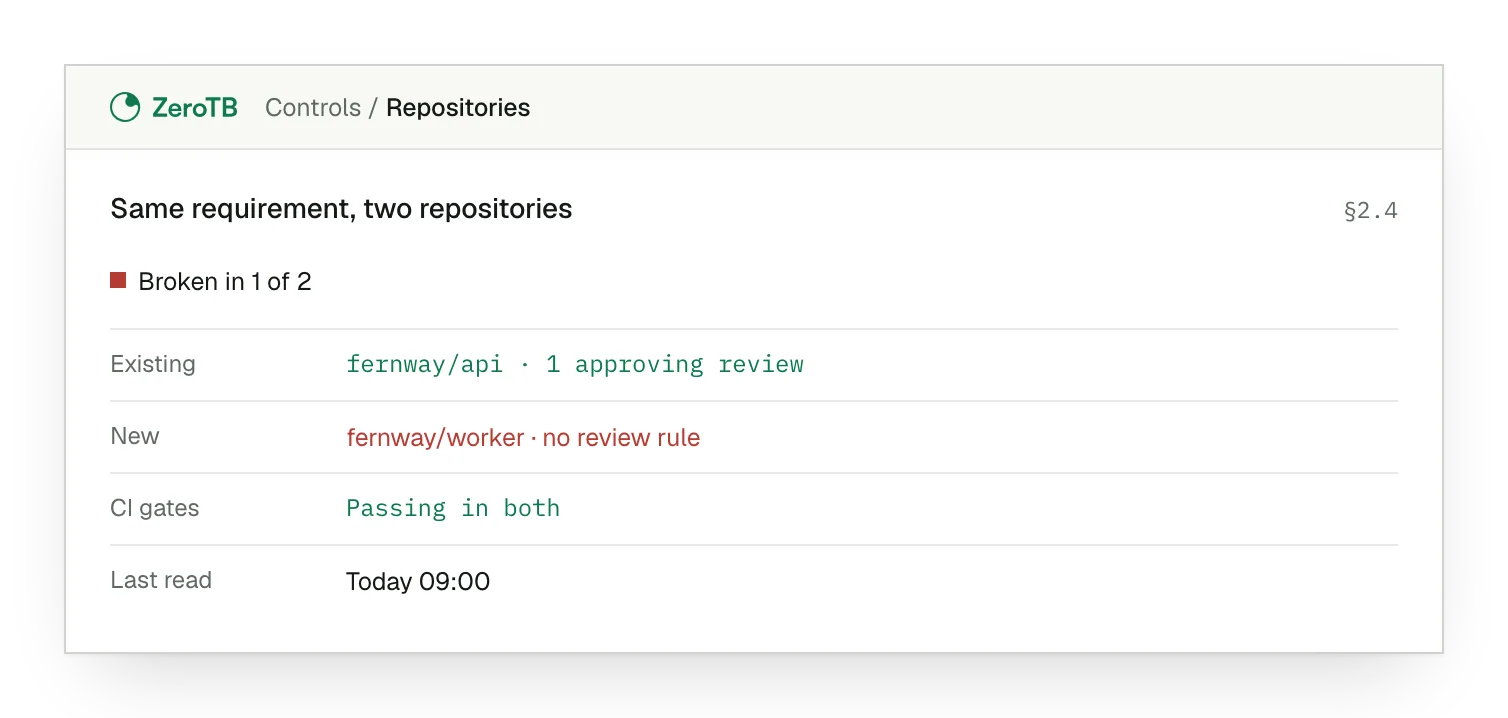
New repositories skip reviews and cost audit findings
Missing branch protection rules let new repositories ship without required reviews or tests. The unmet policy can return as an audit finding.
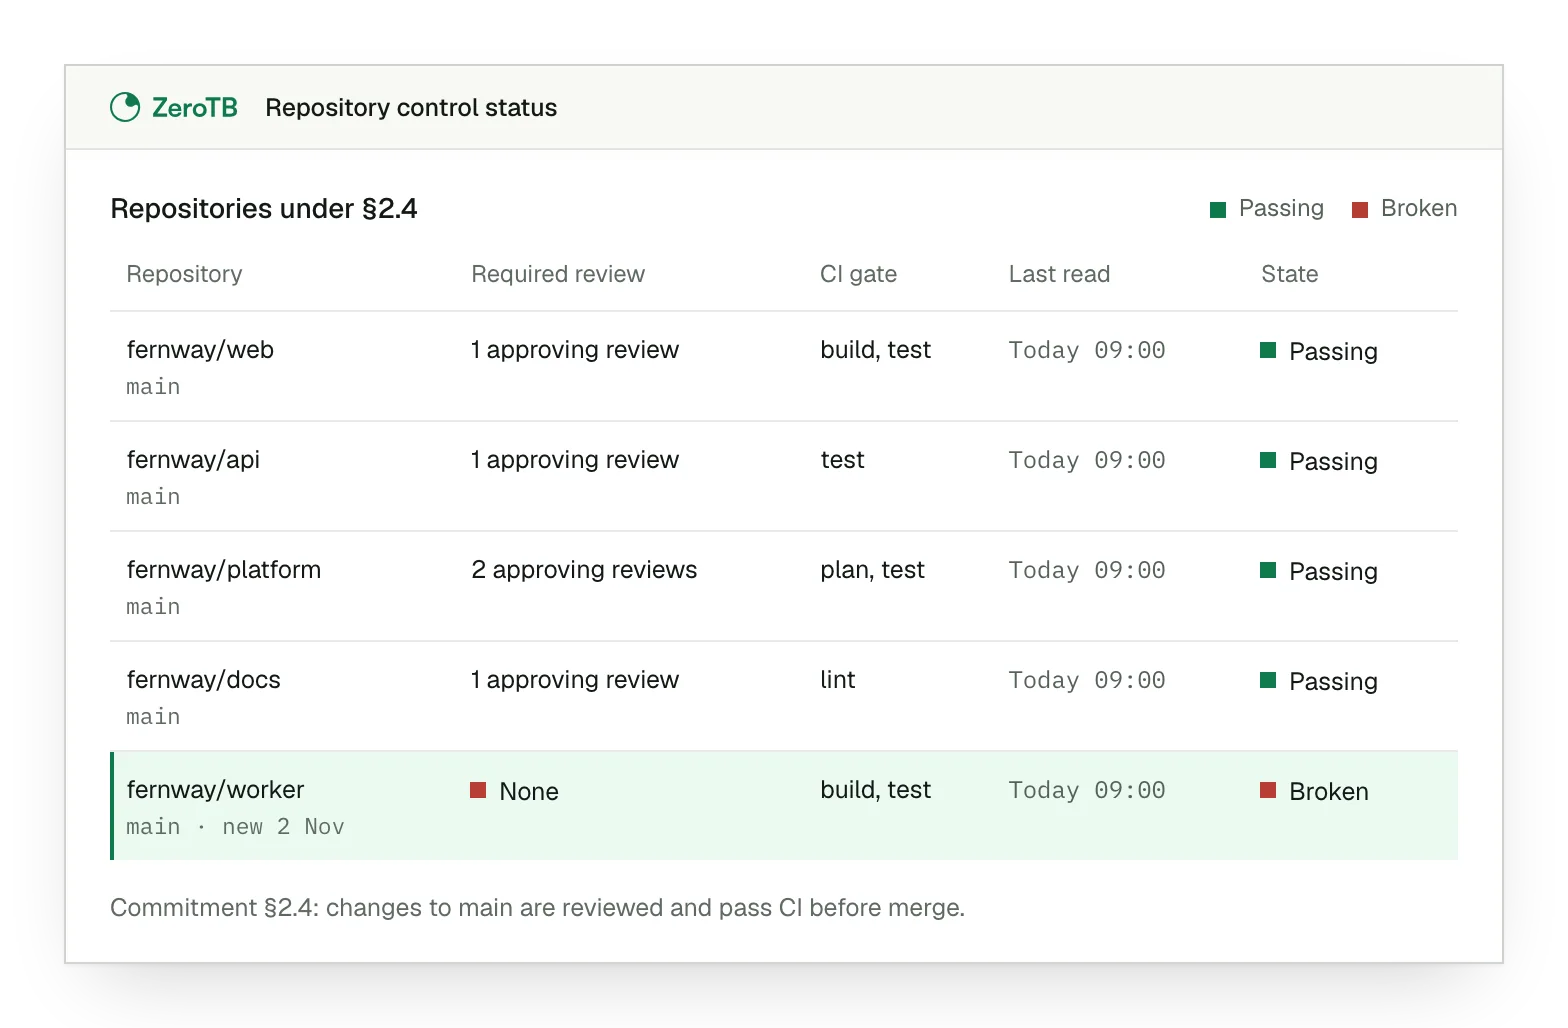
A new repository is created
Branch protection is never applied
Unreviewed code reaches production
ZeroTB restores missing GitHub protections and rechecks them
ZeroTB repairs gaps in GitHub protections and checks them again. Daily checks show whether the agreed conditions still hold as repositories change.
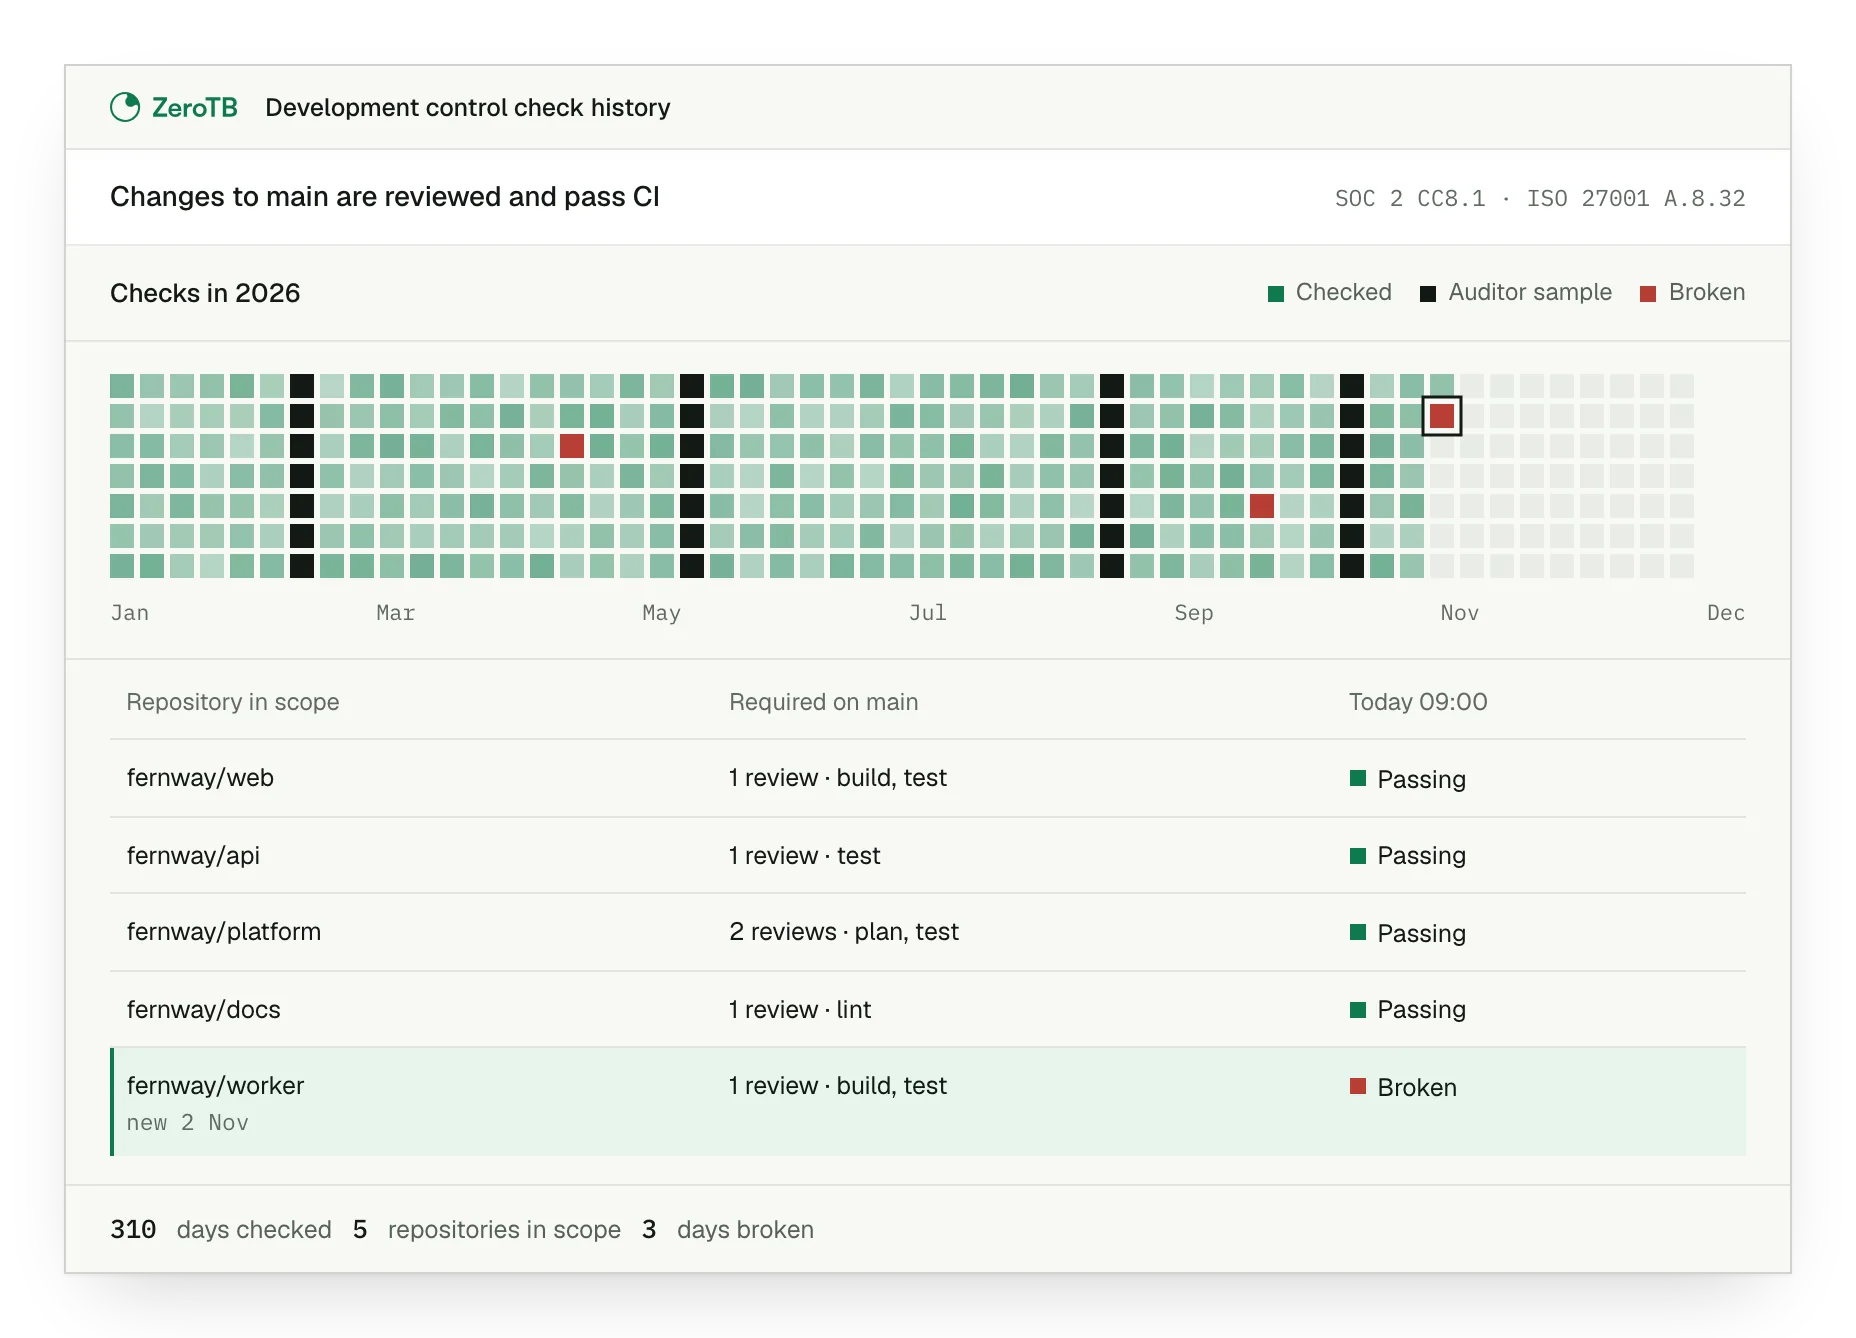
Daily commitment checks
We check approved commitments daily against repositories within the agreed scope and evidence requirements.
Fix with an owner
We assign the failed condition to an owner with its clause and proposed fix.
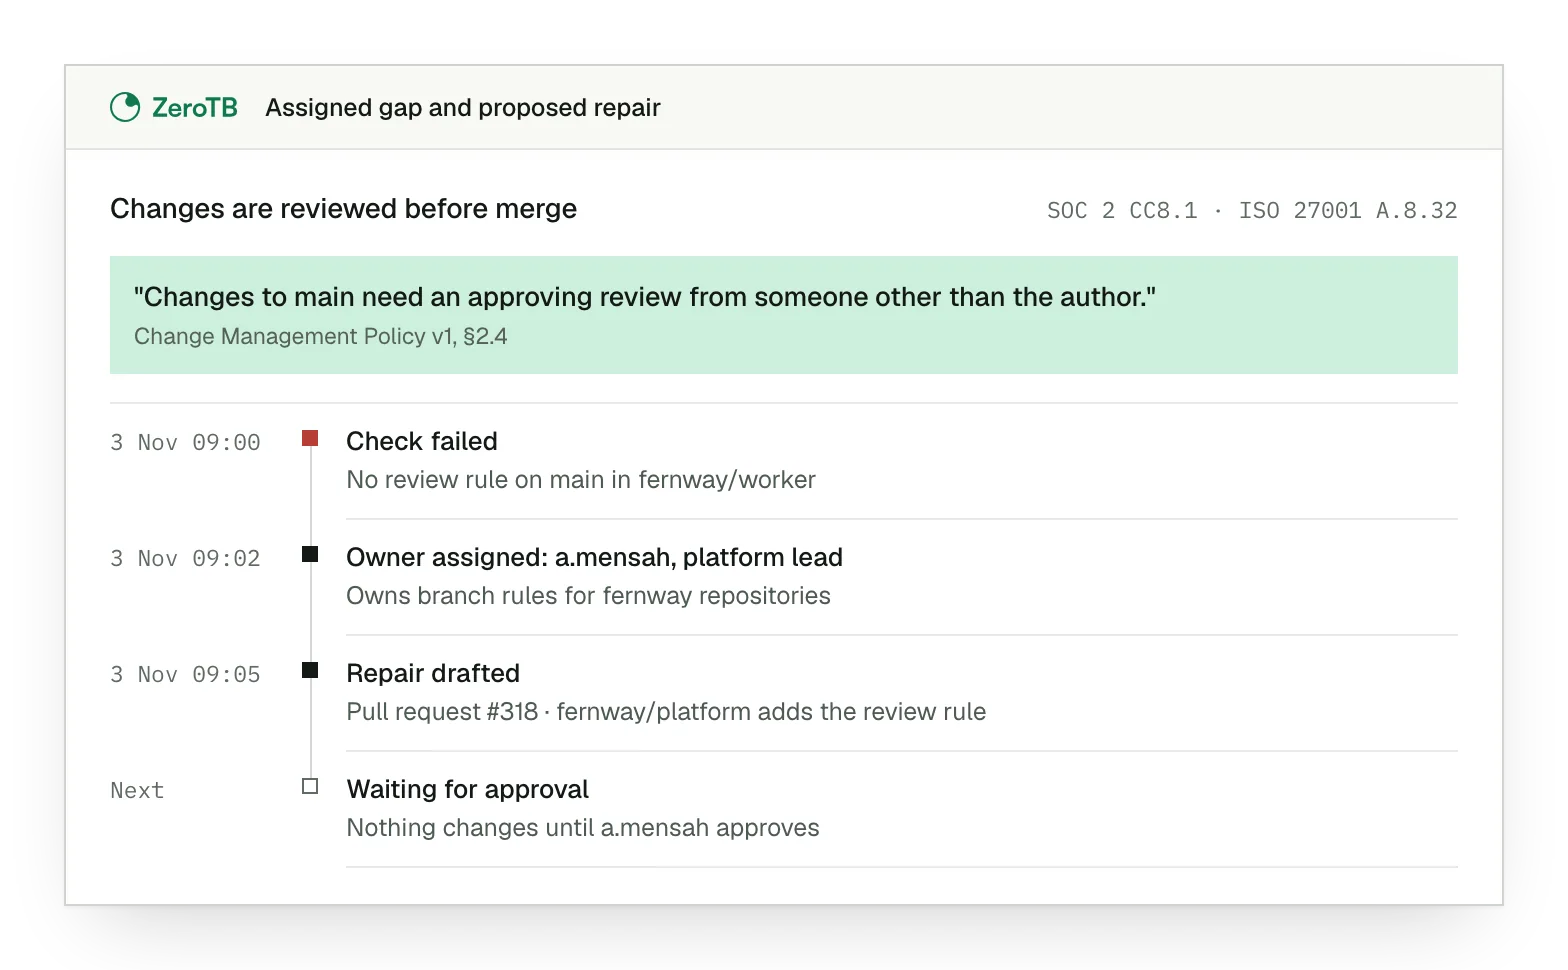
Engineers merge fixes
Each fix arrives as a pull request for engineers to review and merge.
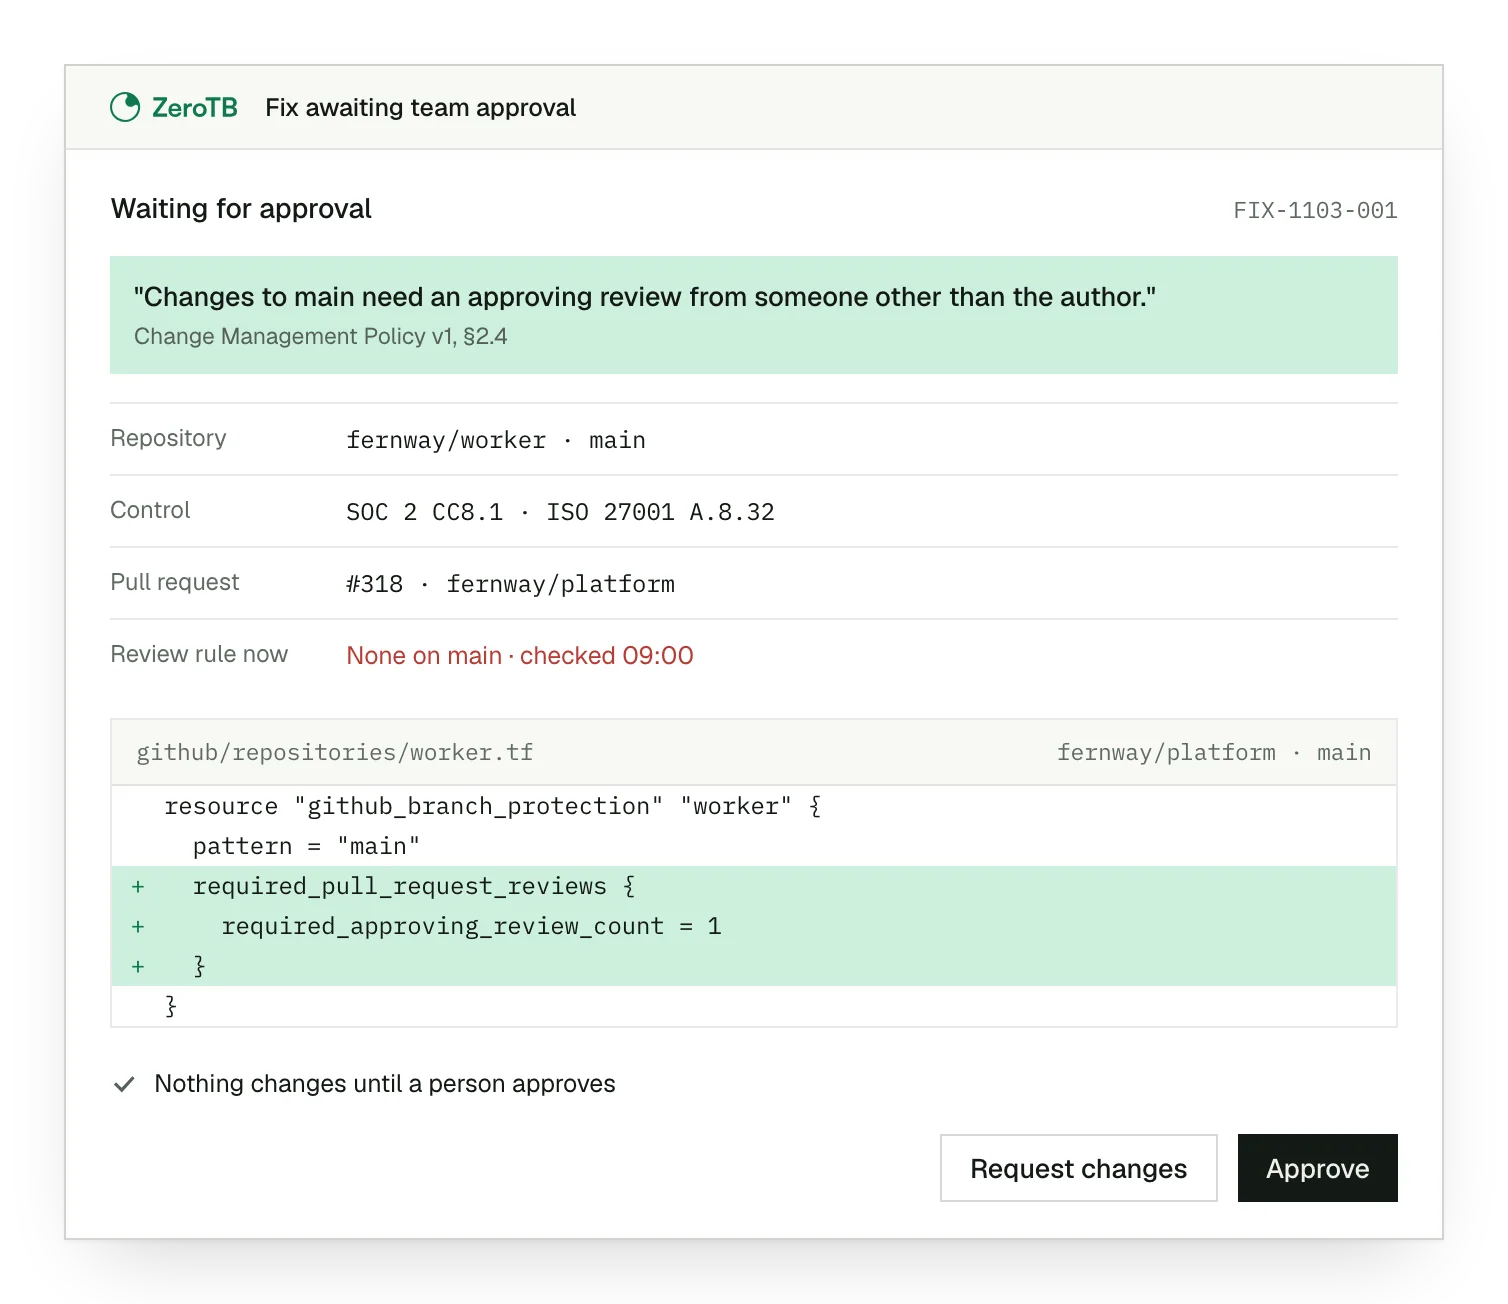
Closed after recheck
ZeroTB rechecks the repaired rule before closure. AI cannot close the gap independently.
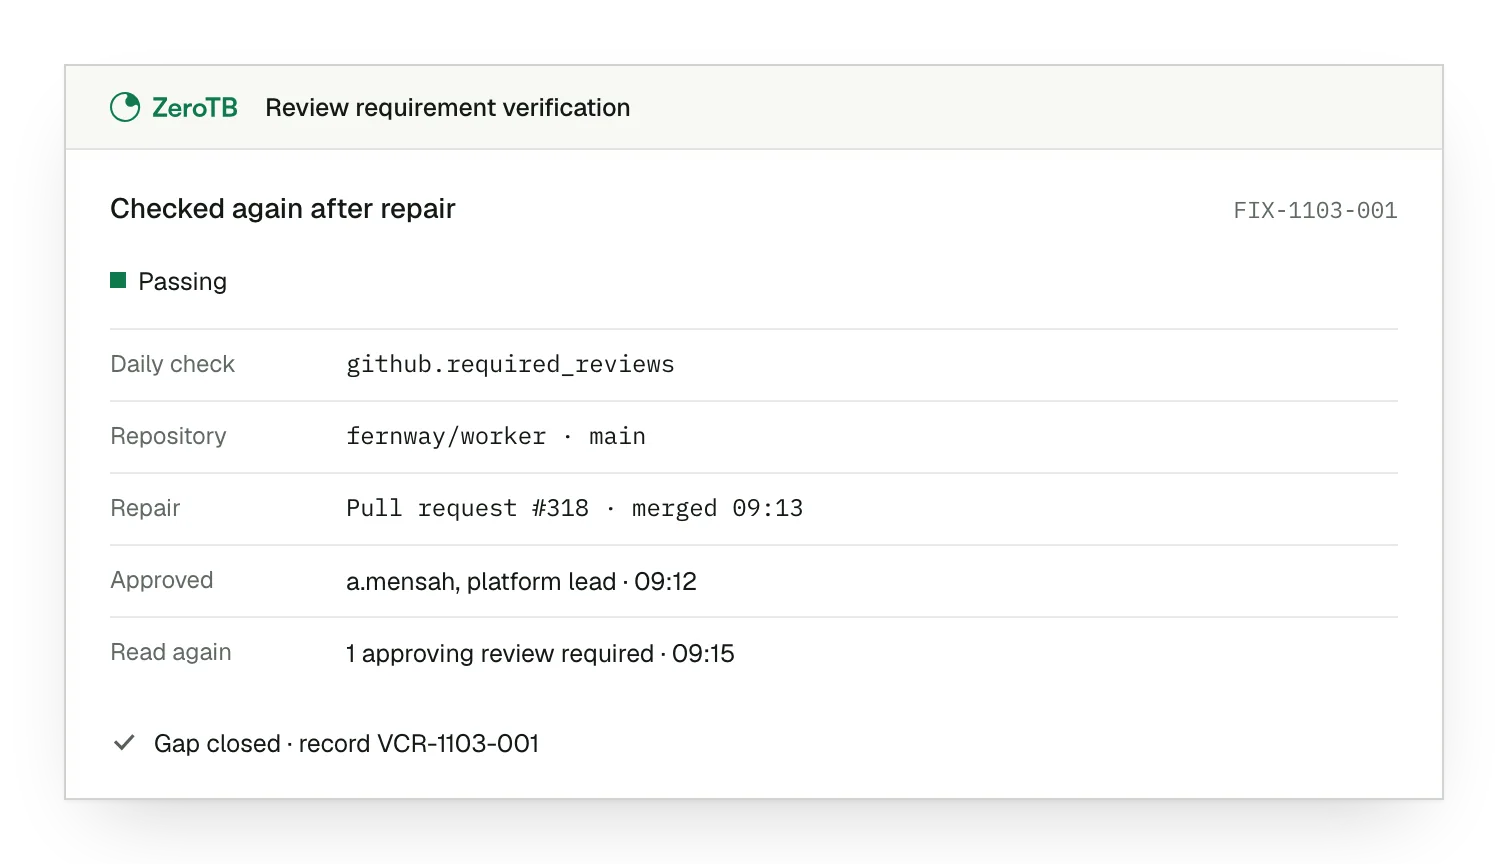
Signed repair record
ZeroTB keeps commitment, before-and-after states, action, approval and verification in the Verified Control Record.
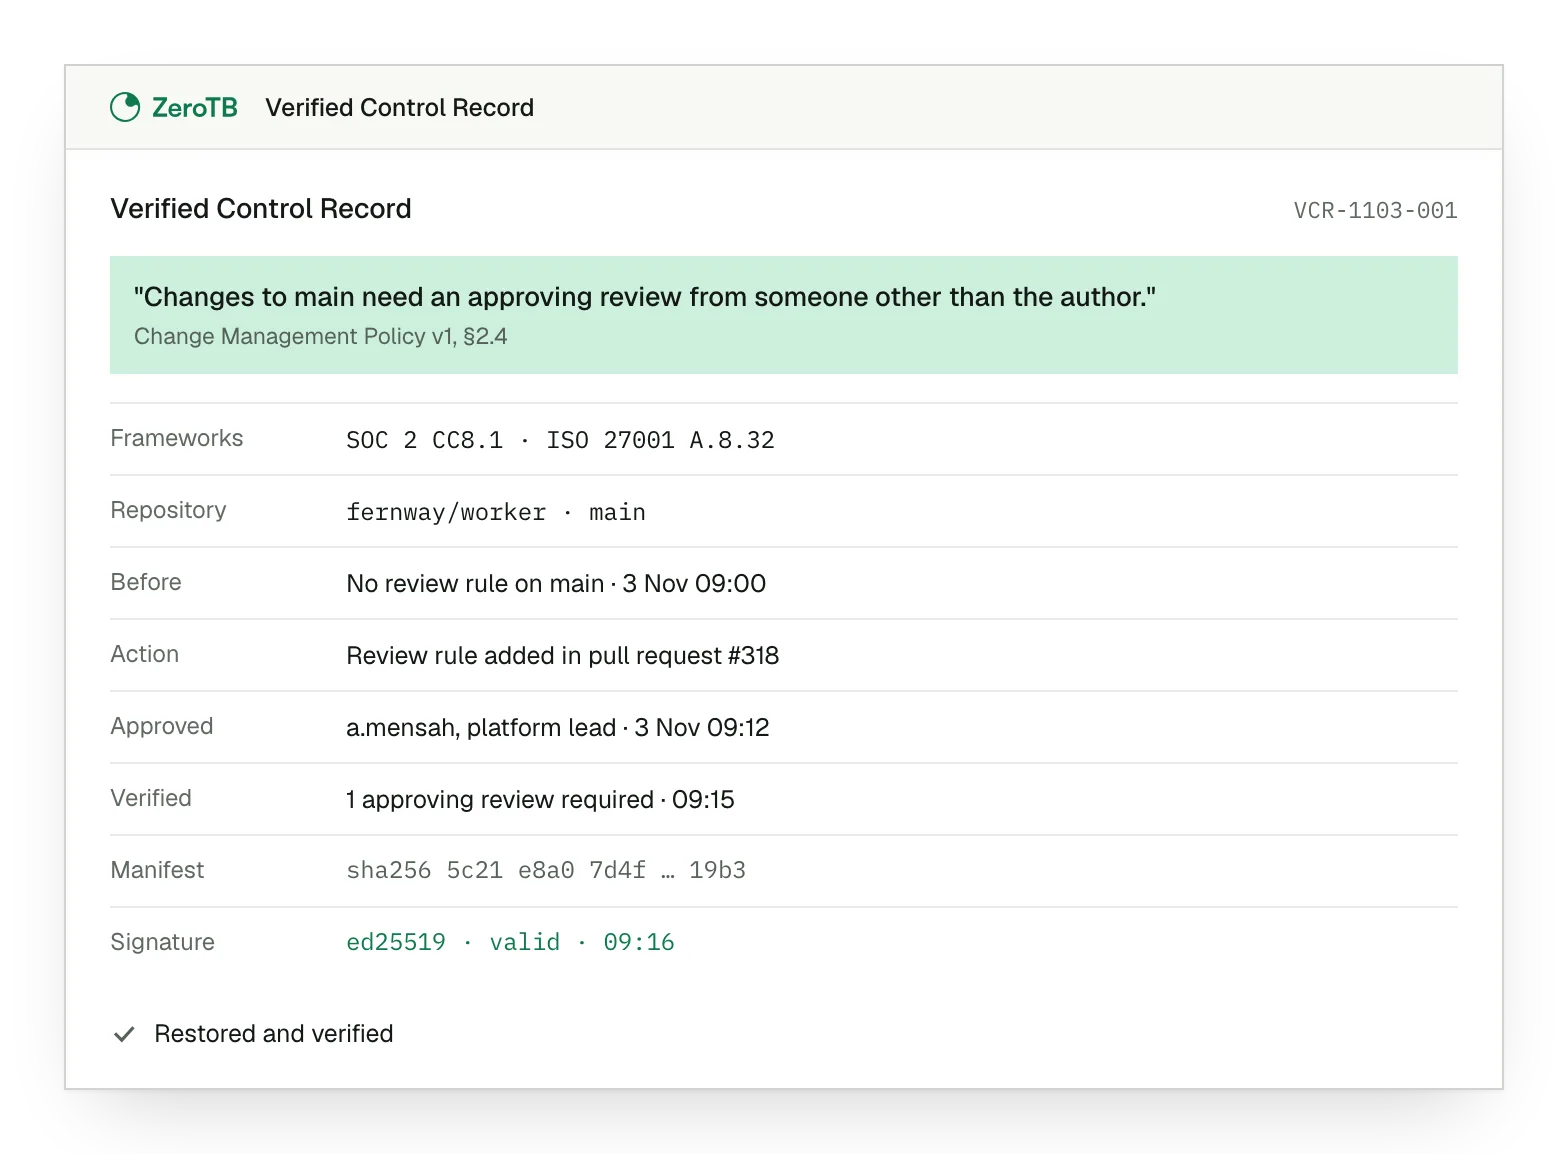
ZeroTB checks GitHub rules for SOC 2 CC8.1
ZeroTB checks GitHub branch protection rules, required reviews and CI gates against the route your company approved for code changes.
Reads
- Branch protection rules
- Required review settings
- CI gate conditions
Controls
- SOC 2 CC8.1 · Control changes to systems
- ISO 27001 A.8.4 · Control access to source code
- ISO 27001 A.8.32 · Manage system changes
A.8.4 coverage concerns only the controlled route for code changes. Wider access decisions remain part of that control. See SOC 2 change management.
We compare each repository's branch rules with the approved development commitment.
We check that required reviews are still in place across the agreed repositories.
We check that CI gates still enforce the testing requirements your team approved.
We examine whether reviews and tests support the route your commitment describes.
Your team scopes ZeroTB's GitHub write access
Read-only access lets ZeroTB observe GitHub. Your team decides which writes to allow and can revoke the permissions it grants.
The initial connection observes repositories before your team grants any write access.
Each permission grant covers specific action classes your team has authorized.
Your team can withdraw write permissions granted for a repair.
Direct API actions require an explicit choice to use that repair method.
API actions must be reversible and stay within policy limits.
Your team decides when a repository needs an exception to the commitment.
ZeroTB connects read-only to repositories you approve
Before connecting to GitHub, we establish which repositories the commitment covers and what their settings must show.
Agree the requirement
We identify the development commitment and prepare its required repository conditions for approval.
Define the scope
We identify the repositories, owners, check cadence and evidence each commitment needs.
Connect read-only
ZeroTB observes GitHub settings within the approved scope before any write action.
New repositories and agent-written code stay covered
GitHub checks follow where your team ships code, including new repositories, changed release routes and routes for agent-written contributions.
New repositories
We include new repositories where the same review and testing requirements apply.
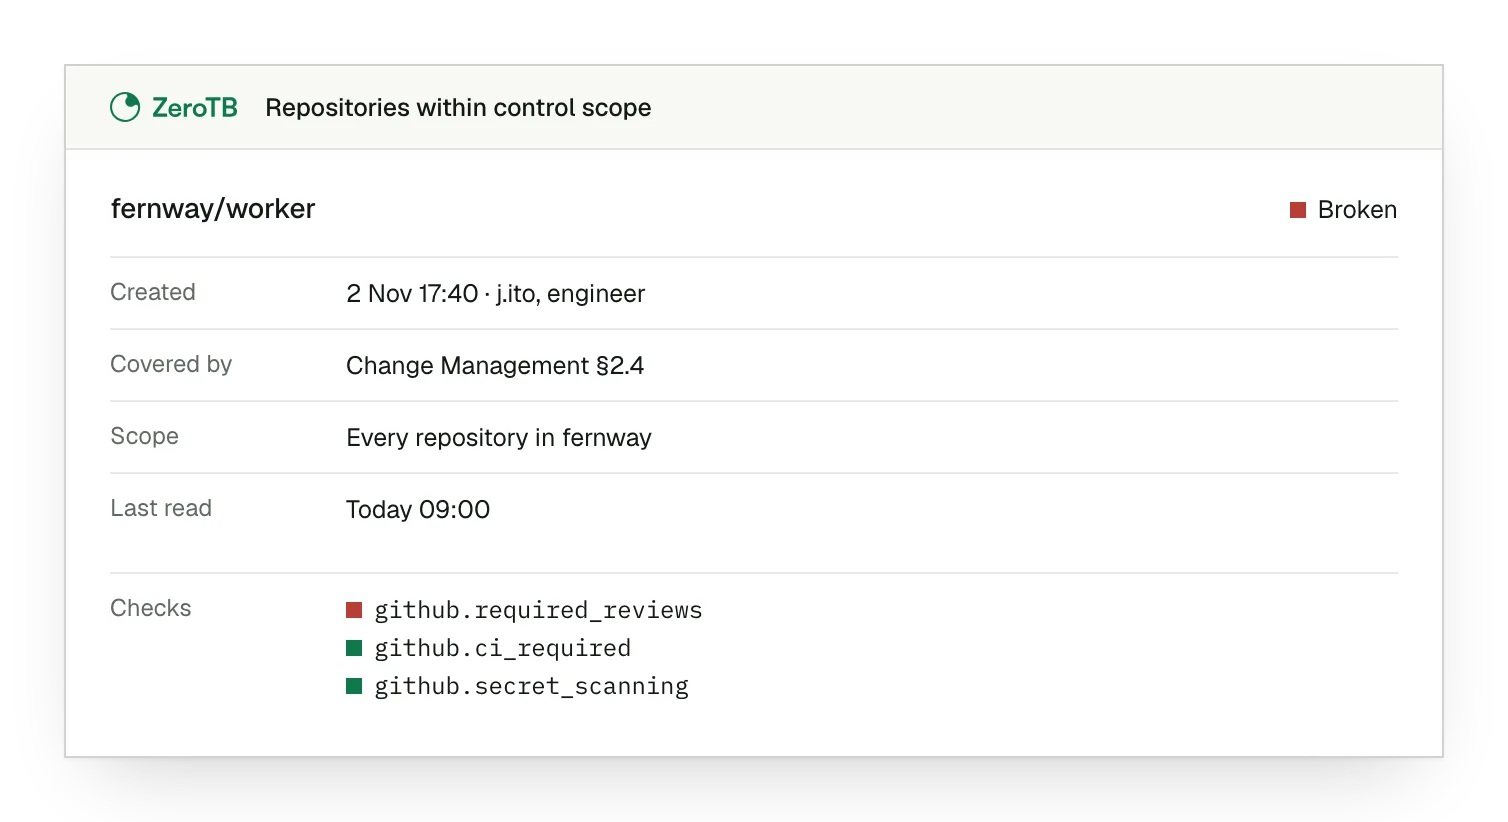
Changed release workflows
We recheck required reviews and tests when a release takes a different route.
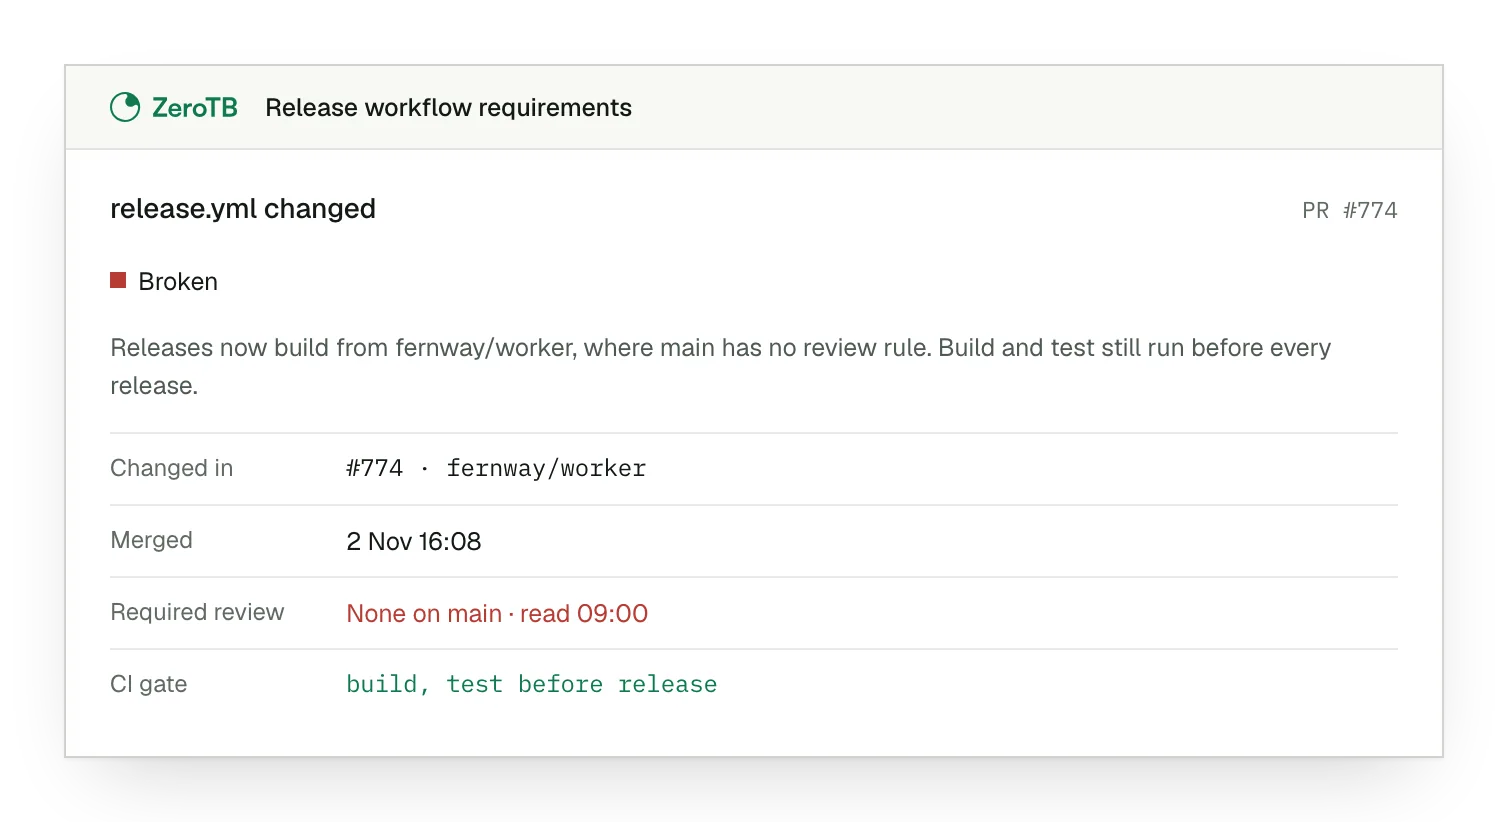
Agent-assisted development
Agent-written code follows the same change and development requirements as other contributions.
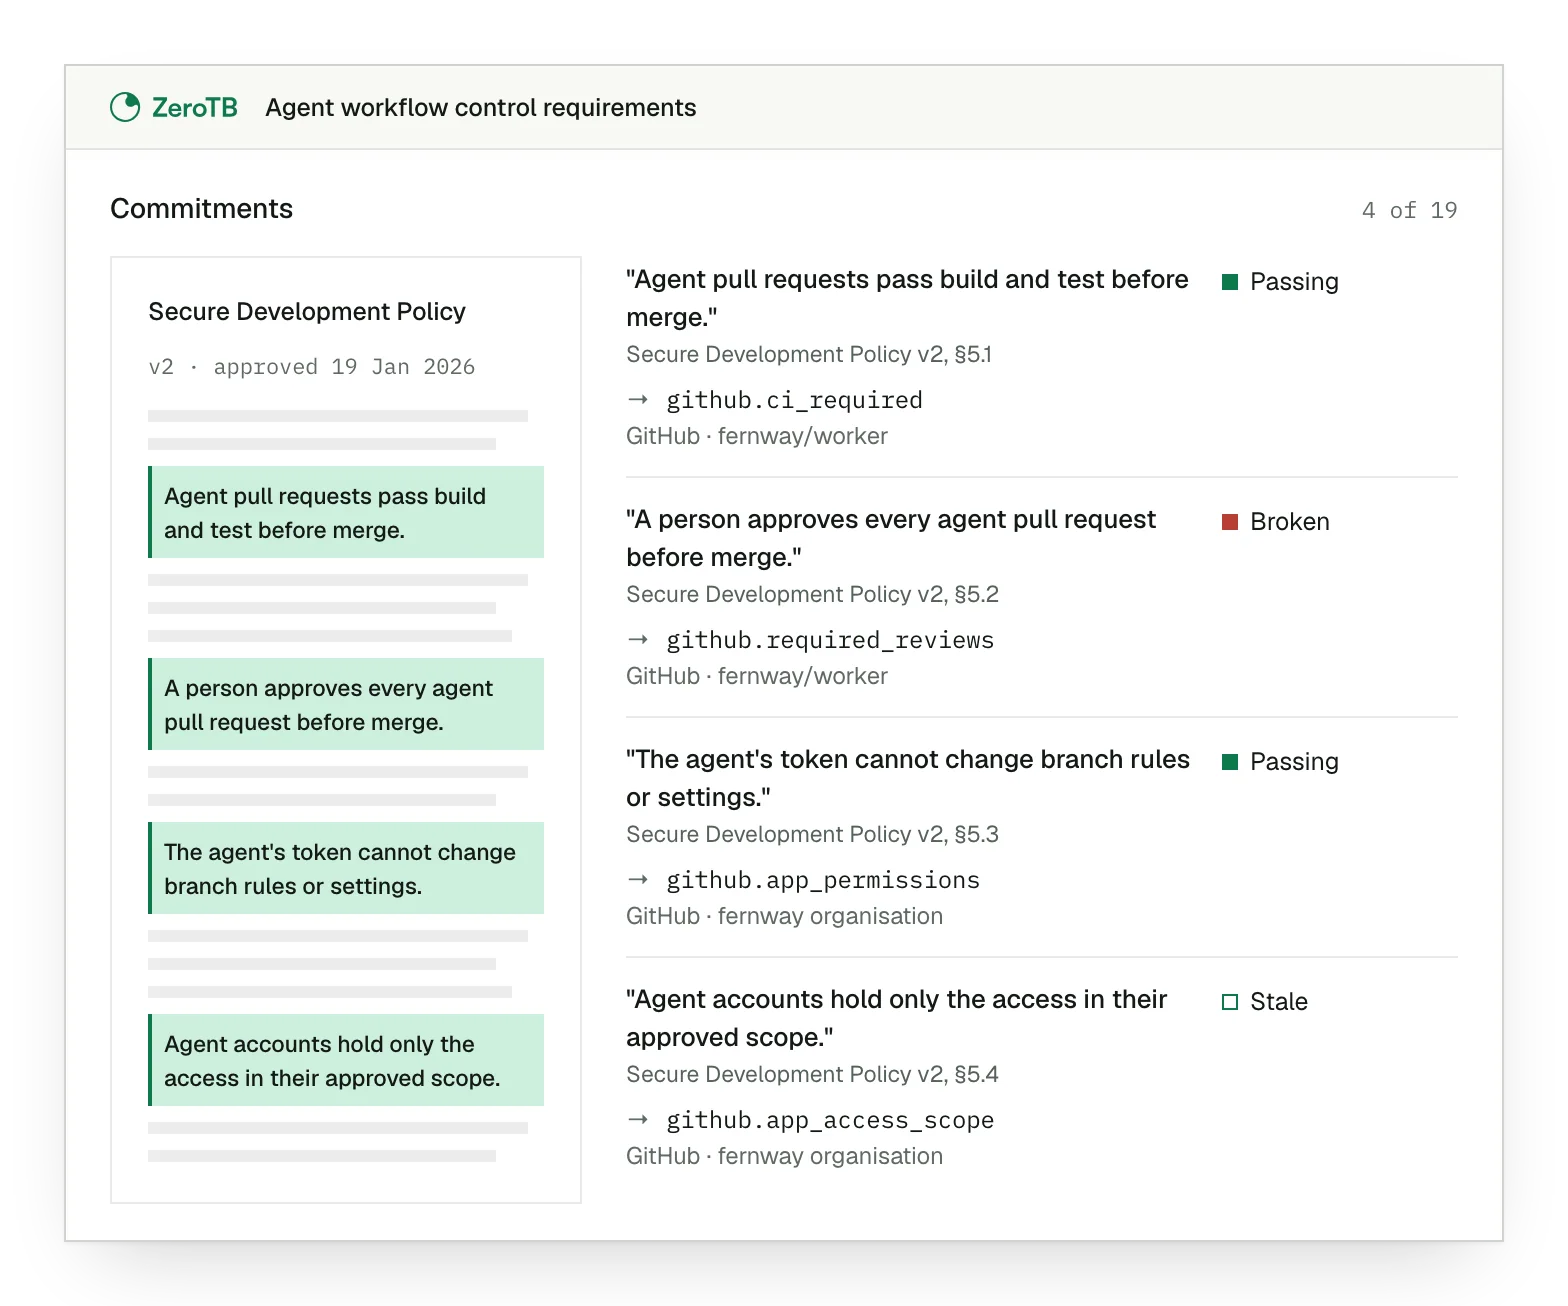
Talk to our team
Talk with our team about GitHub review and testing gaps and where your engineers need support.
FAQ
Does GitHub's SOC 2 report cover our repositories?
GitHub's SOC 2 report covers its platform. Your team must show that branch protection, required reviews and CI gates hold in your own repositories.
What evidence does an auditor want for GitHub change management?
Auditors examine pull request approvals and protection settings across the period. Each repair adds a signed, portable Verified Control Record that auditors can read directly in ZeroTB.
Does a stale observation mean a branch protection rule has failed?
A stale observation means ZeroTB lacks current evidence about the rule. Unknown, stale or disconnected states remain visible until a fresh check establishes the condition.
What if production changes through a route outside GitHub?
A route outside GitHub needs its own place in the change-control scope. A repository rule does not cover a separate deployment path.
What if a GitHub repair needs manual work?
A GitHub repair needing manual work gets a proposed runbook for the owner. ZeroTB checks the repository again after the work.
What happens if the same repository requirement fails again?
A repeated repository failure becomes a new gap for its owner. Checks continue at the agreed cadence, so a restored review rule can be checked again after removal.
Start with the Pilot
In eight weeks, the Pilot maps up to 25 commitments and takes two real control gaps through verified restoration.