Code, cloud, access and devices stay compliant
ZeroTB keeps controls working in development, cloud, identity, endpoints, and people and process.
ZeroTB checks and repairs controls in five areas
Change and development
Our deepest area includes branch rules, CI gates, required reviews and repair pull requests.
Cloud and infrastructure
We find production settings outside policy and prepare repairs as infrastructure-as-code pull requests.
Identity and access. We check departures, MFA, privileges and on-time access reviews
Endpoint. A lightweight device agent observes enrollment, encryption and patching
People and process. Control operations schedules training, vendor reviews and incident exercises, then verifies completion
Untracked system changes cost you audit findings
A repository loses a required review while the policy stays unchanged. Like access left after a departure, that gap can become an audit finding.
Systems change after the audit
Required protections stop working
Unresolved gaps become findings
Keeping your commitments working every day
ZeroTB checks your commitments against your systems each day and carries detected gaps through to verified restoration. The same responsibility continues as the company changes.
Confirm requirements
AI identifies commitments in your report and policies for your team to confirm, including scope and required evidence.
Check daily
ZeroTB compares requirements with system state daily, showing the source clause, observation and reason for each finding.
Prepare repairs
Each gap gets an owner and response window before ZeroTB prepares a runbook, pull request, API action or guardrail.
Authorize changes
Your team authorizes material changes before the responsible person or ZeroTB executes the repair within agreed permissions.
Verify and record
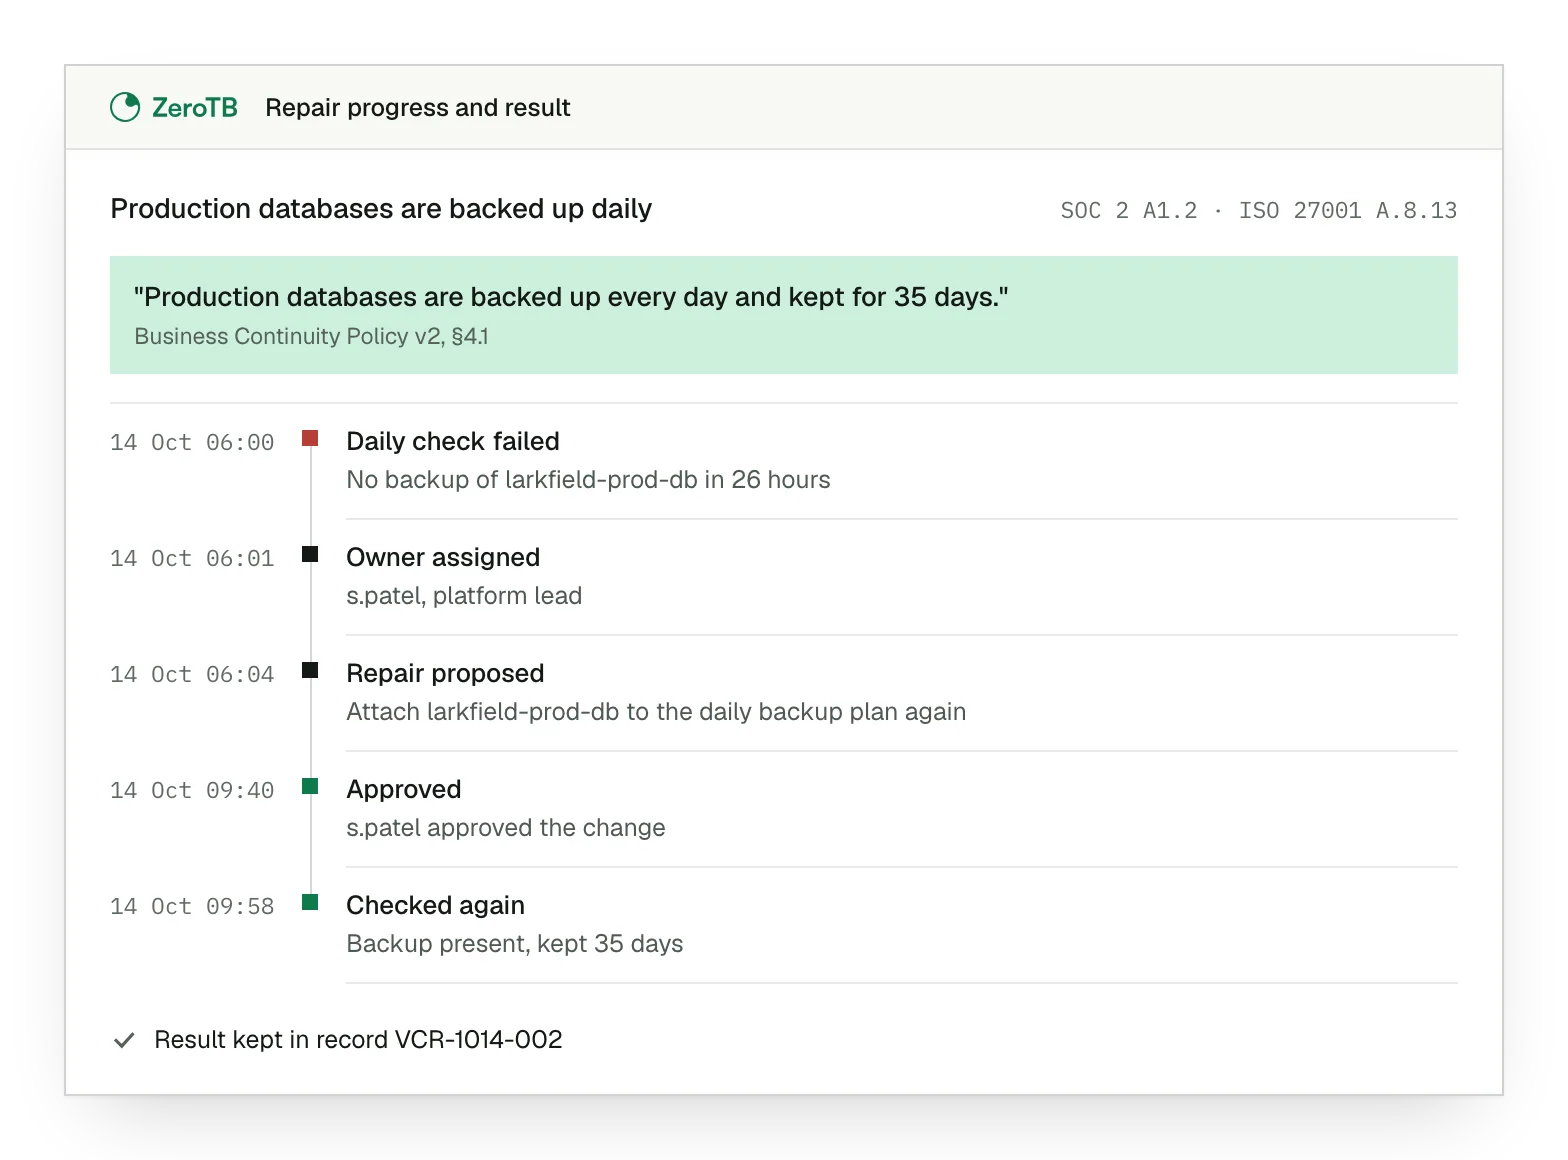
You receive verified restoration and a signed record of the commitment, before-and-after states, action, approval and verification.
ZeroTB checks work accounts and their managed devices
A policy requires approved work accounts on managed devices. ZeroTB checks the account and device separately, showing where either part fails the requirement.
Work account rule. Approved accounts on managed devices form one commitment across two areas
Both parts checked. We check the account through identity coverage and the device through endpoint coverage
Failing part named. The owner can see whether the account or the device needs attention
Talk to our team
Talk with us about the systems your team manages and the control gaps that keep returning.
FAQ
How do these areas connect to the systems we already run?
ZeroTB checks your systems through repository, cloud, work-account, identity-provider and endpoint connections. We use the connection each commitment needs, as described on the integrations page.
Do all connected systems need write access?
Connected systems start with read-only access. You grant revocable writes by action class. Material changes use pull requests by default. Direct API actions require opt-in and allow reversal.
What happens when a device or system stops sending observations?
A check with missing observations stays unknown, stale or disconnected. ZeroTB cannot count the control as healthy without evidence of its current condition.
Can a control in one area support SOC 2, ISO 27001 and HIPAA?
A restored control can meet requirements in SOC 2, ISO 27001 and HIPAA at once. Its evidence must cover the scope of each requirement.
Where does the evidence from these areas go?
Your auditor reads the signed Verified Control Record in ZeroTB. The record holds the repair evidence, and your team can keep a portable copy.
Do we need all five areas covered from the start?
Your selected commitments determine which areas need coverage. The Pilot maps up to 25 commitments, and its checks cover the areas needed to assess them.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments and takes two real control gaps through verified restoration.