Keep AWS configuration matching your commitments
ZeroTB keeps AWS security compliance current by checking settings against commitments and preparing repairs for review.
Works with the stack you already run


ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA.
AWS security compliance covers the settings you own
Under the shared responsibility model, AWS secures infrastructure and you keep settings compliant. ZeroTB's software and team keep post-audit controls working for US software, AI, fintech and healthtech companies.
AWS secures infrastructure. AWS protects the hosts, network and services it runs
You secure settings. Your team maintains accounts, access and resource configuration against its commitments
Audits test the period. Auditors sample SOC 2, ISO 27001 or HIPAA evidence across the audit period
Settings changed by deployments cost audit findings
AWS configuration drift after deployment leaves evidence describing old settings. An unmet requirement can return as an audit finding.
Approved configuration recorded
Deployment changes a setting
Production leaves the baseline
ZeroTB repairs what AWS Config rules flag
AWS Config evaluates resources against rules that must match your requirement. ZeroTB prepares repairs and checks the result against that requirement.
| Task | AWS Config rules | Your team | ZeroTB |
|---|---|---|---|
| What it checks | Resource settings against rules | Approves requirements and changes | Your commitments across accounts |
| Who maps requirements | The rule's author | Confirms the meaning | Drafts the check for approval |
| Who repairs drift | Runbooks you configure | Approves the fix | Prepares the repair, then rechecks |
| What auditors read | Rule evaluation results | Approvals in your process | The signed Verified Control Record |
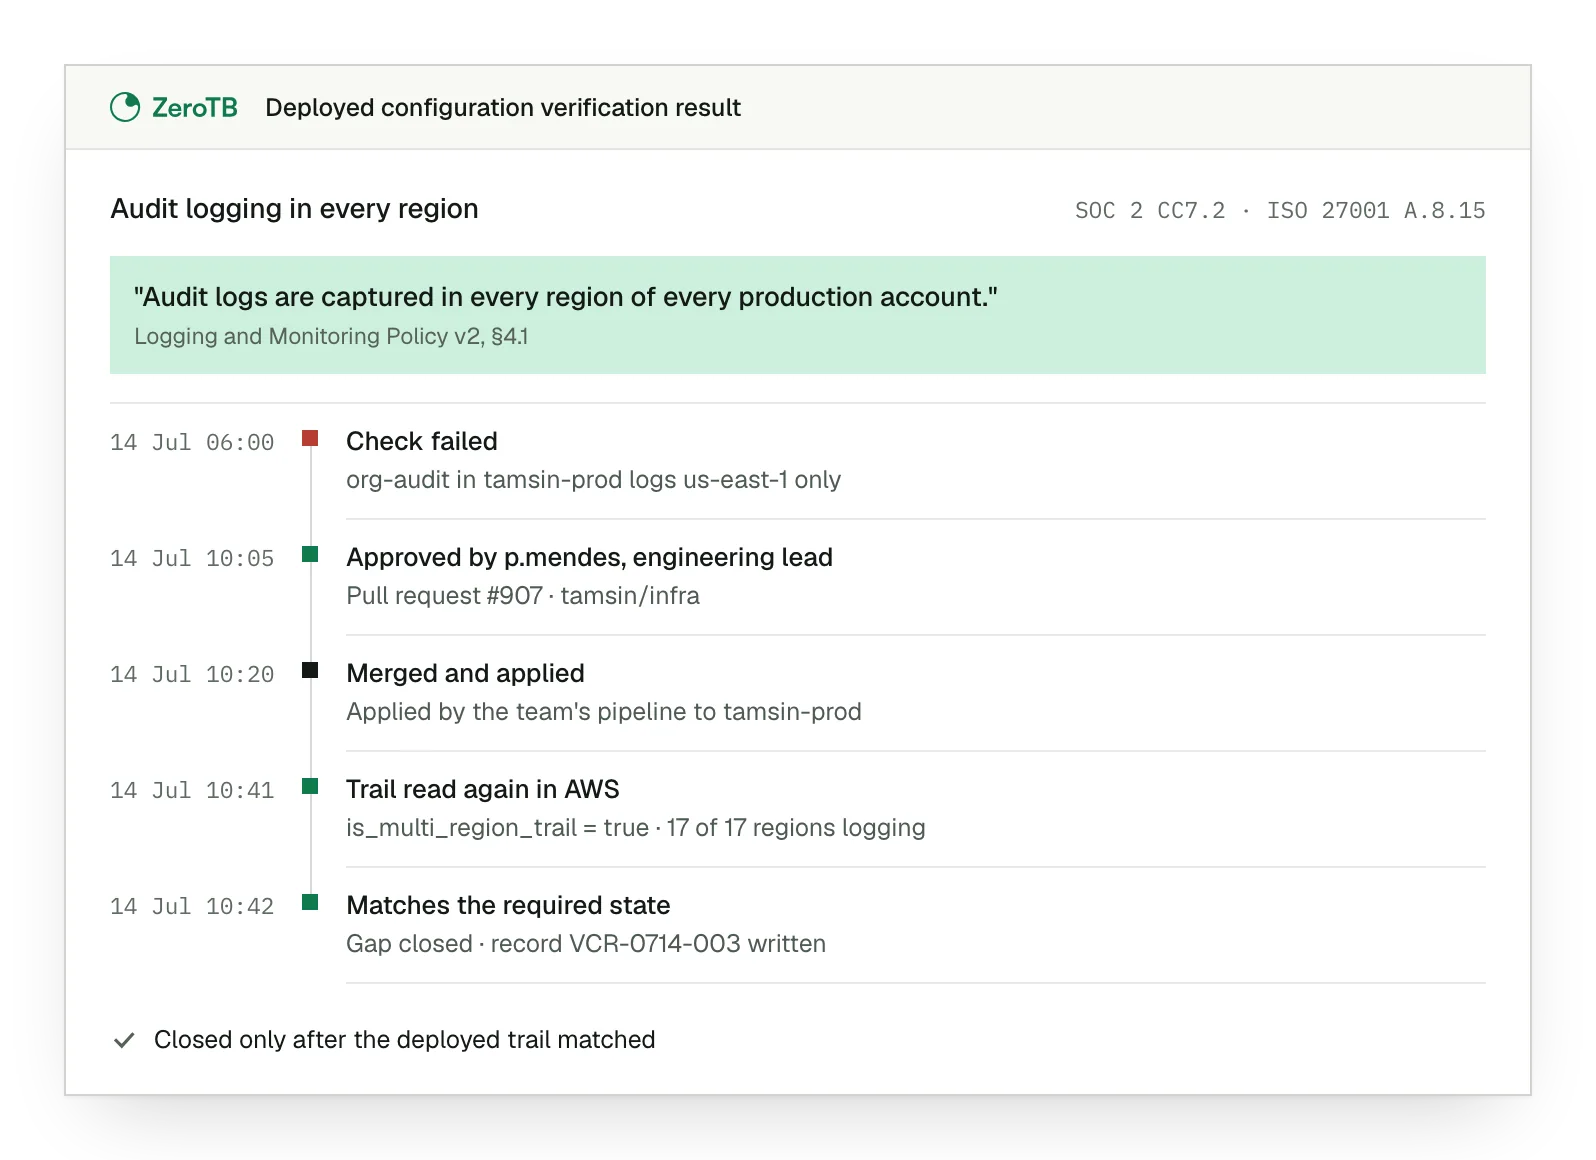
ZeroTB prepares each AWS fix and rechecks it
For an AWS gap, ZeroTB prepares a change engineers can review and merge. We check the deployed setting before closing the repair.
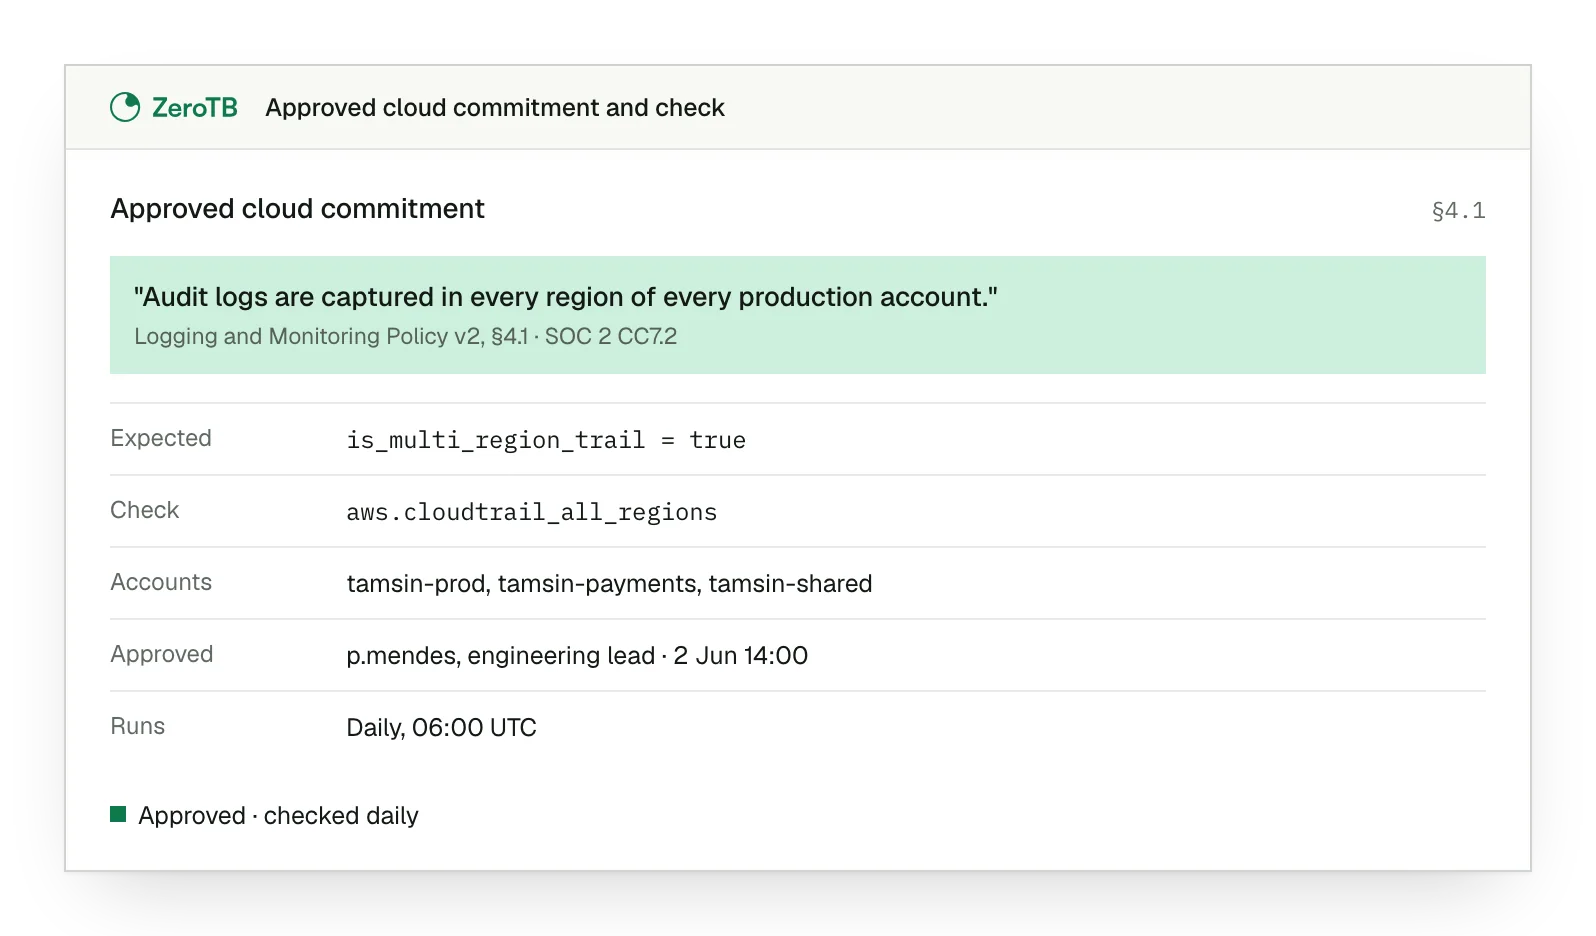
Policy into checks
We turn the report or policy clause into a configuration check for approval.
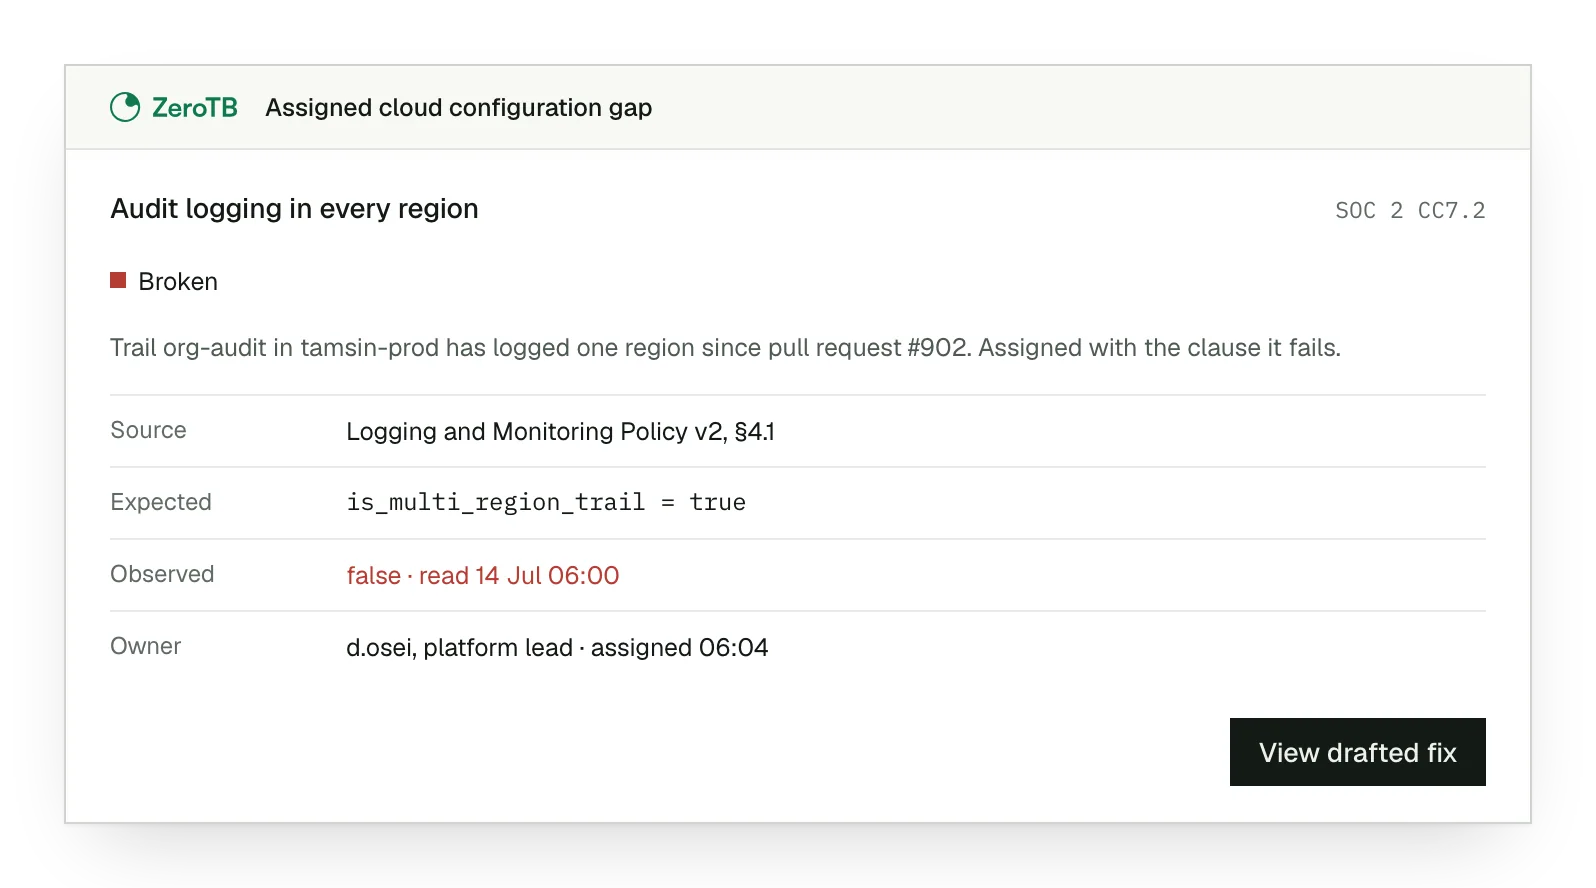
Finding with source
The owner sees which setting failed and the clause that requires it.
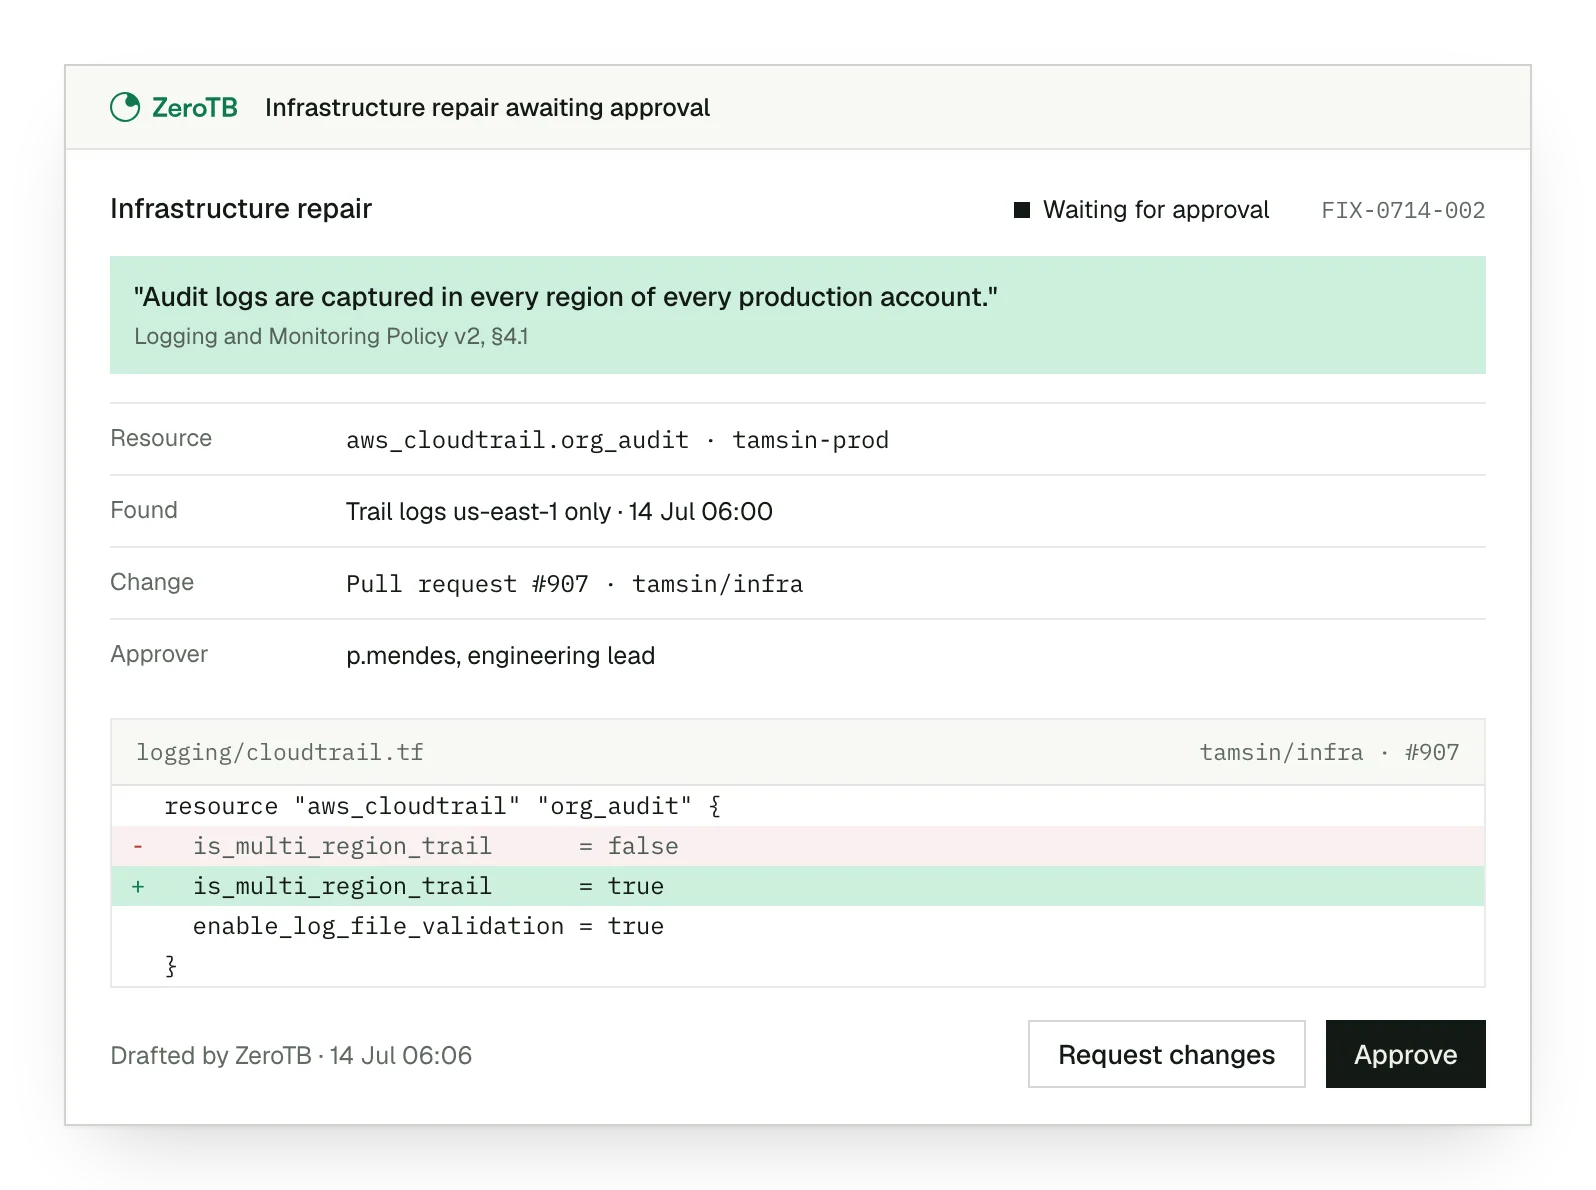
Infrastructure pull request
Engineers review and merge ZeroTB's infrastructure as code pull request through their process.
Deployed state rechecked
We check AWS after deployment and close the gap when the required setting holds.
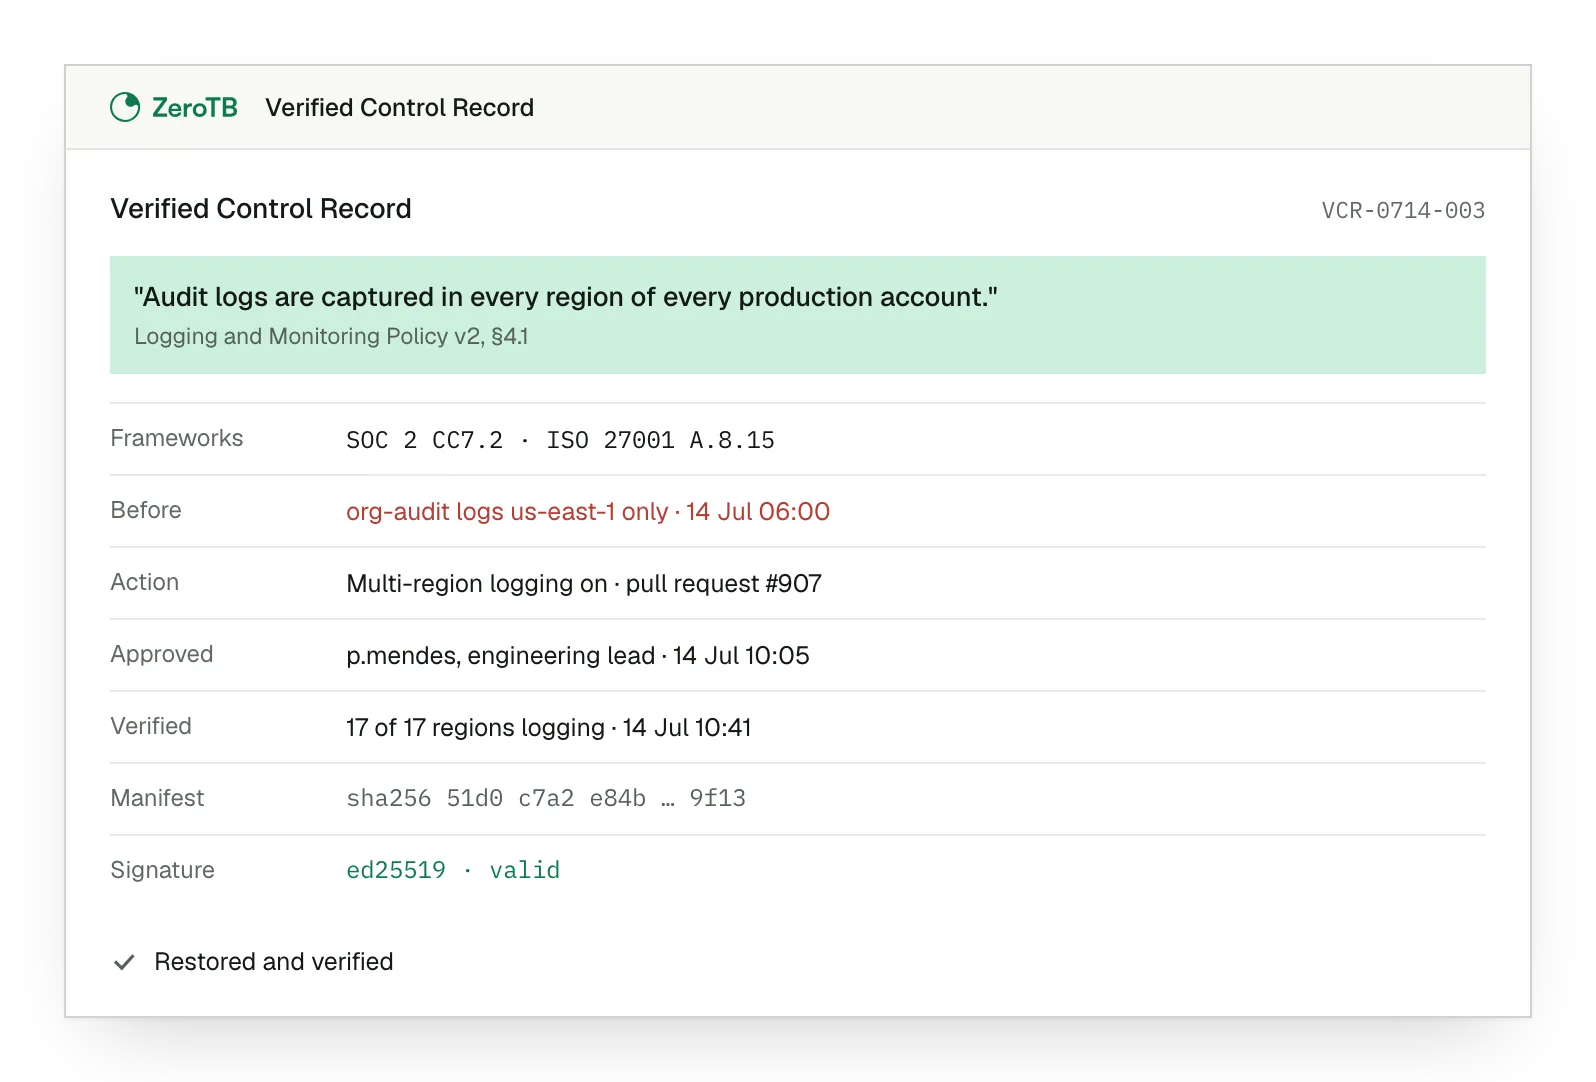
Signed repair record
The Verified Control Record keeps the requirement, before-and-after states, repair, approval and verification together.
ZeroTB checks AWS configuration for SOC 2 controls
Each AWS commitment identifies the resources to examine. ZeroTB reads their configuration and checks it against the approved requirement.
Reads
- Cloud resource configuration
- AWS account context
- Resource identifiers and context
Controls
- SOC 2 CC7.1 · Detect configuration changes
- SOC 2 CC8.1 · Control changes to systems
- ISO 27001 A.8.9 · Maintain approved configuration baselines
These checks supply control evidence. The approved commitment defines which resources and conditions the evidence covers.
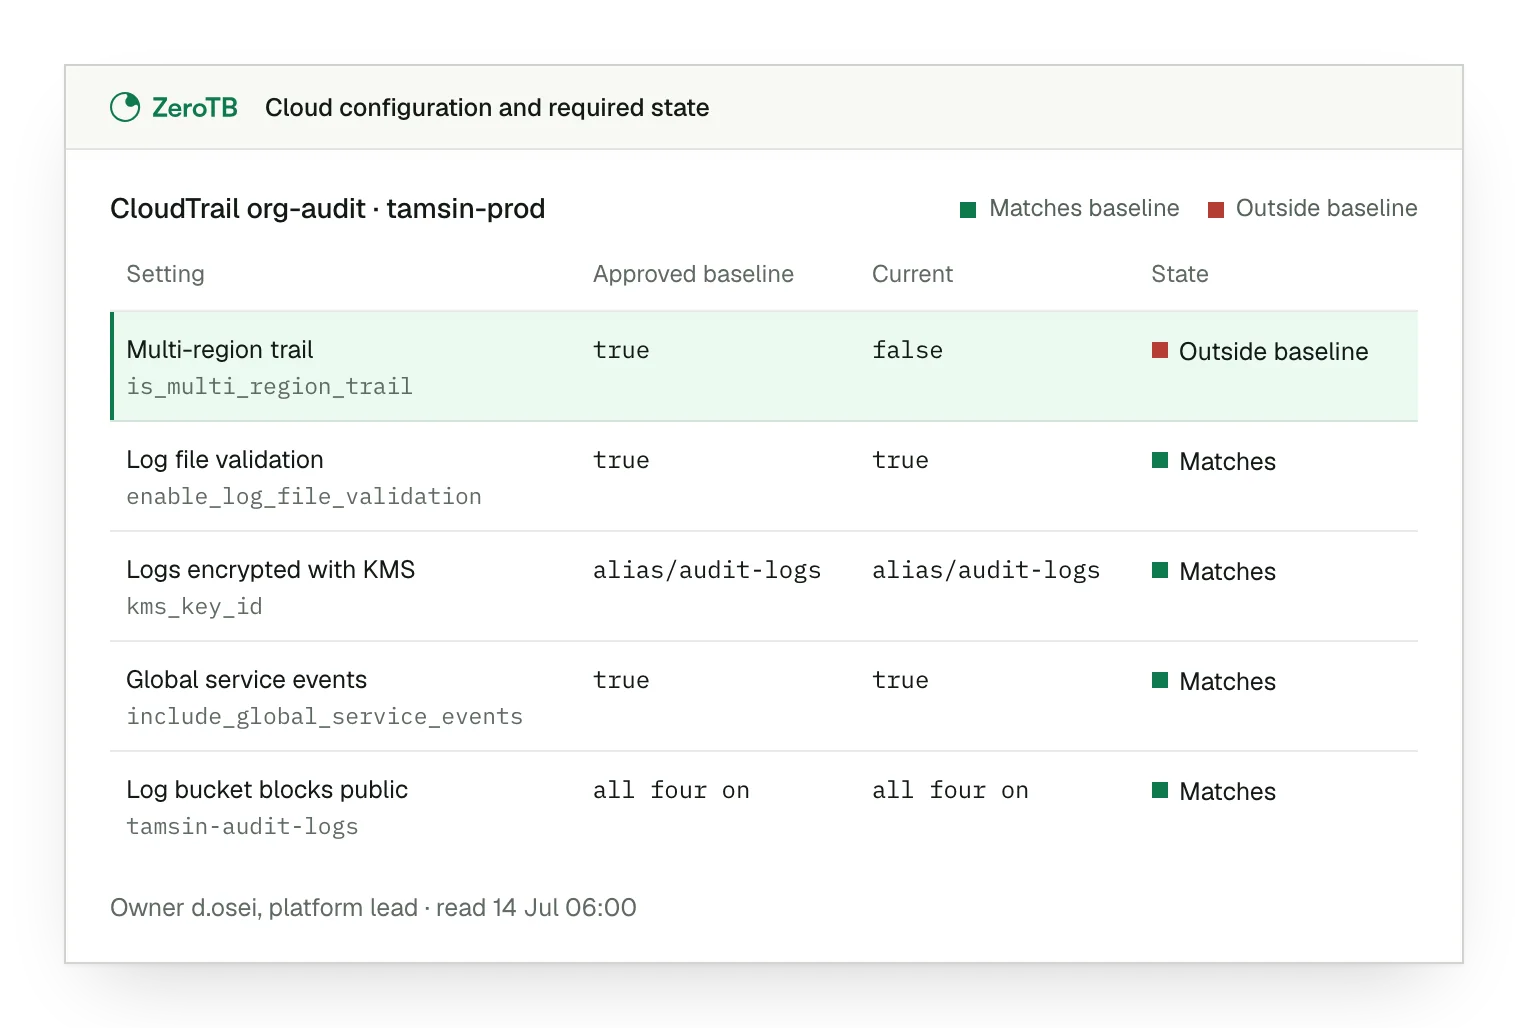
We compare the resource's settings with the baseline your company agreed to keep.
We check the settings running in production against the requirement for that environment.
We check observation sources and whether current observations cover the agreed resources.
We inspect the configuration after deployment to confirm that the required setting is back.
ZeroTB starts read-only in your AWS accounts
Read-only access lets ZeroTB observe AWS settings. Your team separately grants the permissions needed to change a resource.
The first connection observes the settings on AWS resources in scope.
A grant names the action class and limits the resources ZeroTB can change.
Your team can withdraw the write permissions it granted for a repair.
People authorize material changes and decide which exceptions are legitimate.
Your team explicitly opts into direct API actions before ZeroTB uses them.
Policy limits the resources API actions can affect, and those actions must be reversible.
Your team approves the AWS scope before connection
Before connecting to AWS, we establish what the clause requires and where that setting needs to hold.
Define the requirement
Our team prepares the clause's configuration requirement for your approval.
Establish the scope
We identify the accounts, resources, owner and evidence needed for the check.
Connect and observe
ZeroTB connects read-only to observe the configuration within the approved scope.
ZeroTB extends AWS checks as your accounts change
AWS checks follow the commitment as infrastructure changes, accounts join its scope or another framework requires the same condition.
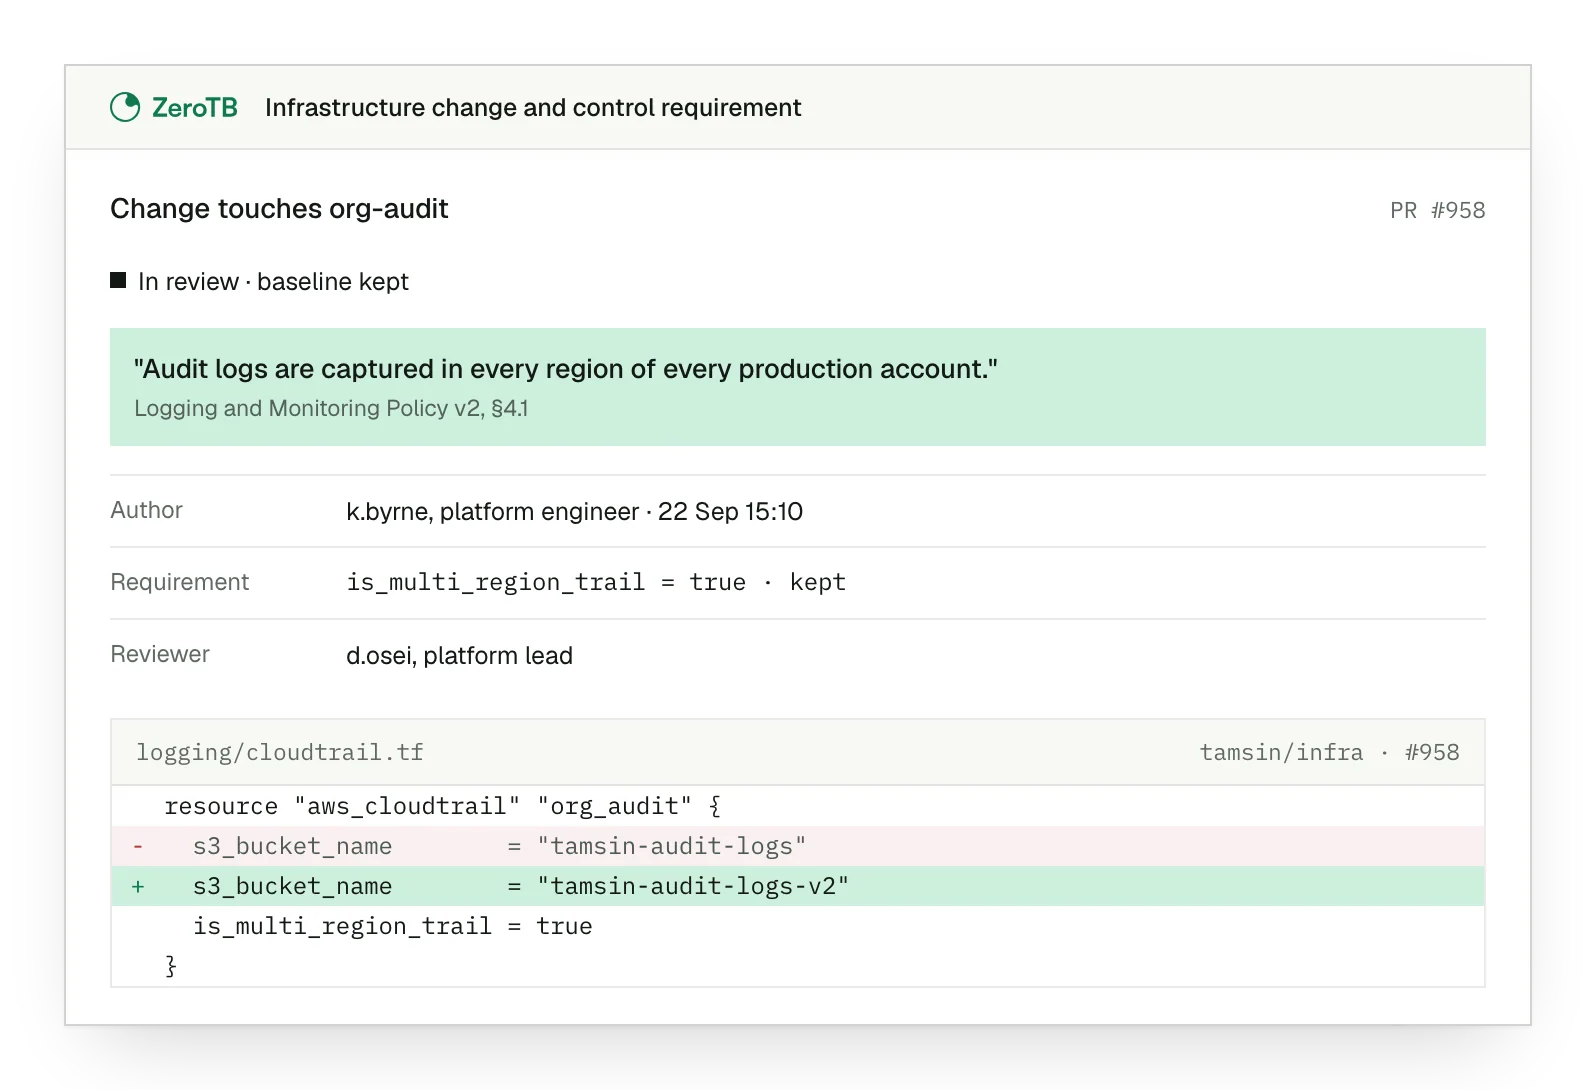
Infrastructure edits
Engineers assess infrastructure changes against the required setting before they reach production.
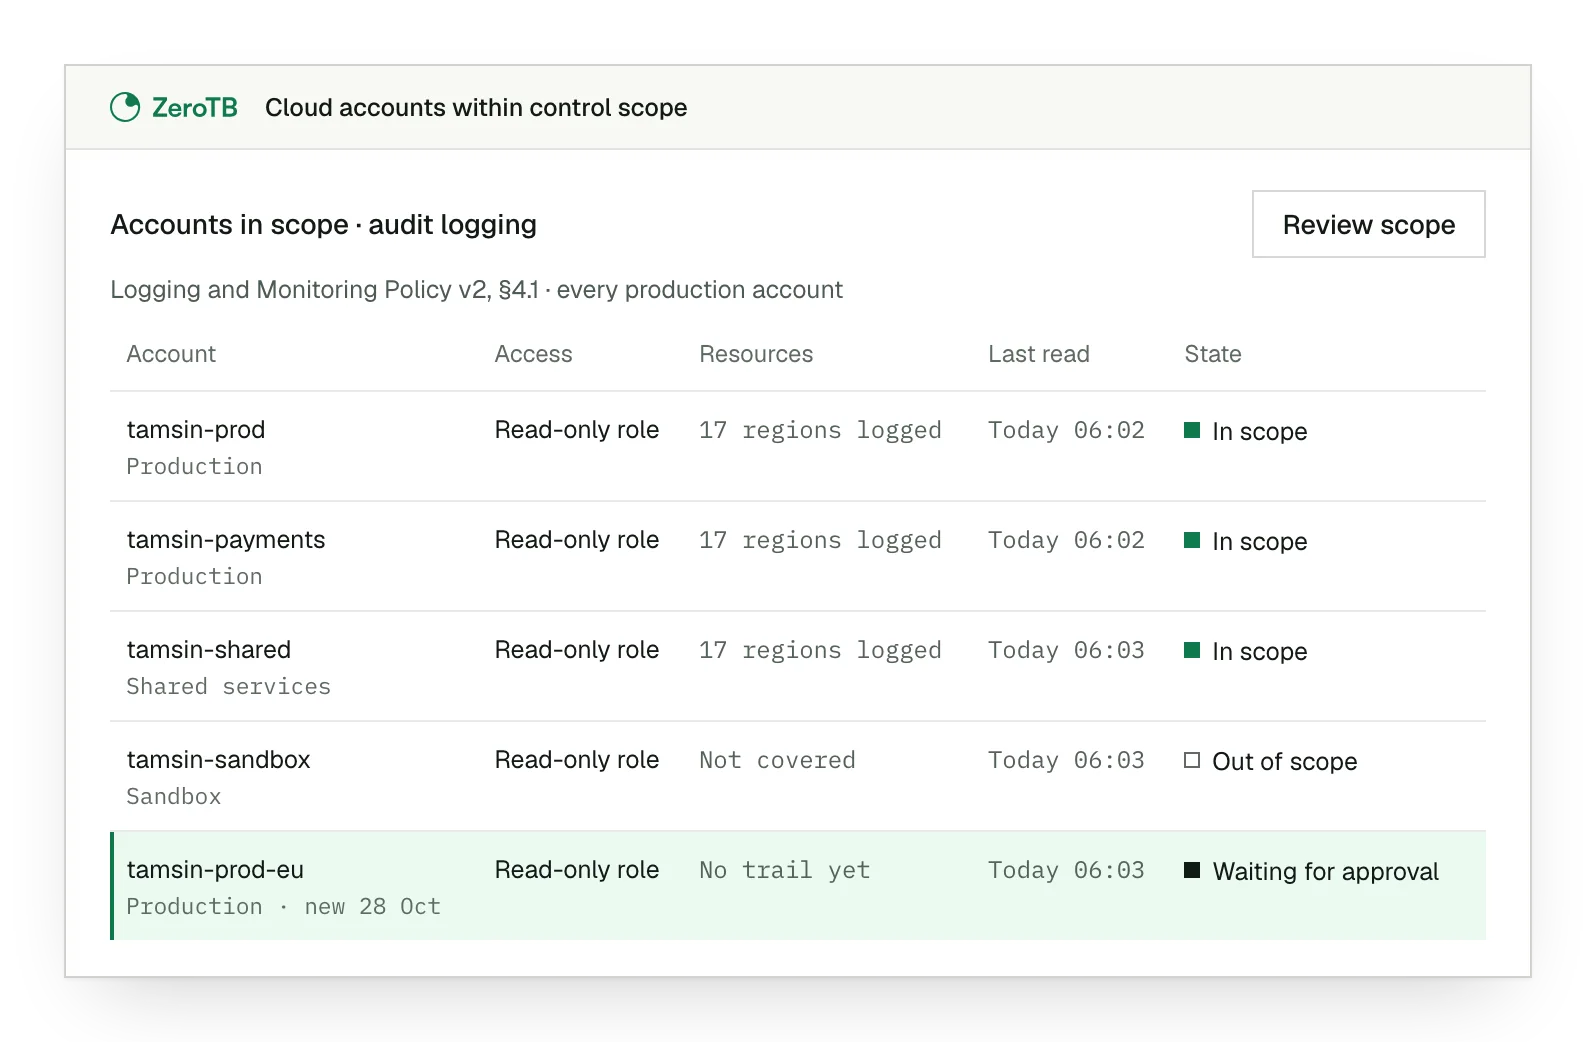
Account changes
We extend the scope to new accounts where the same setting must hold.
Shared framework requirements
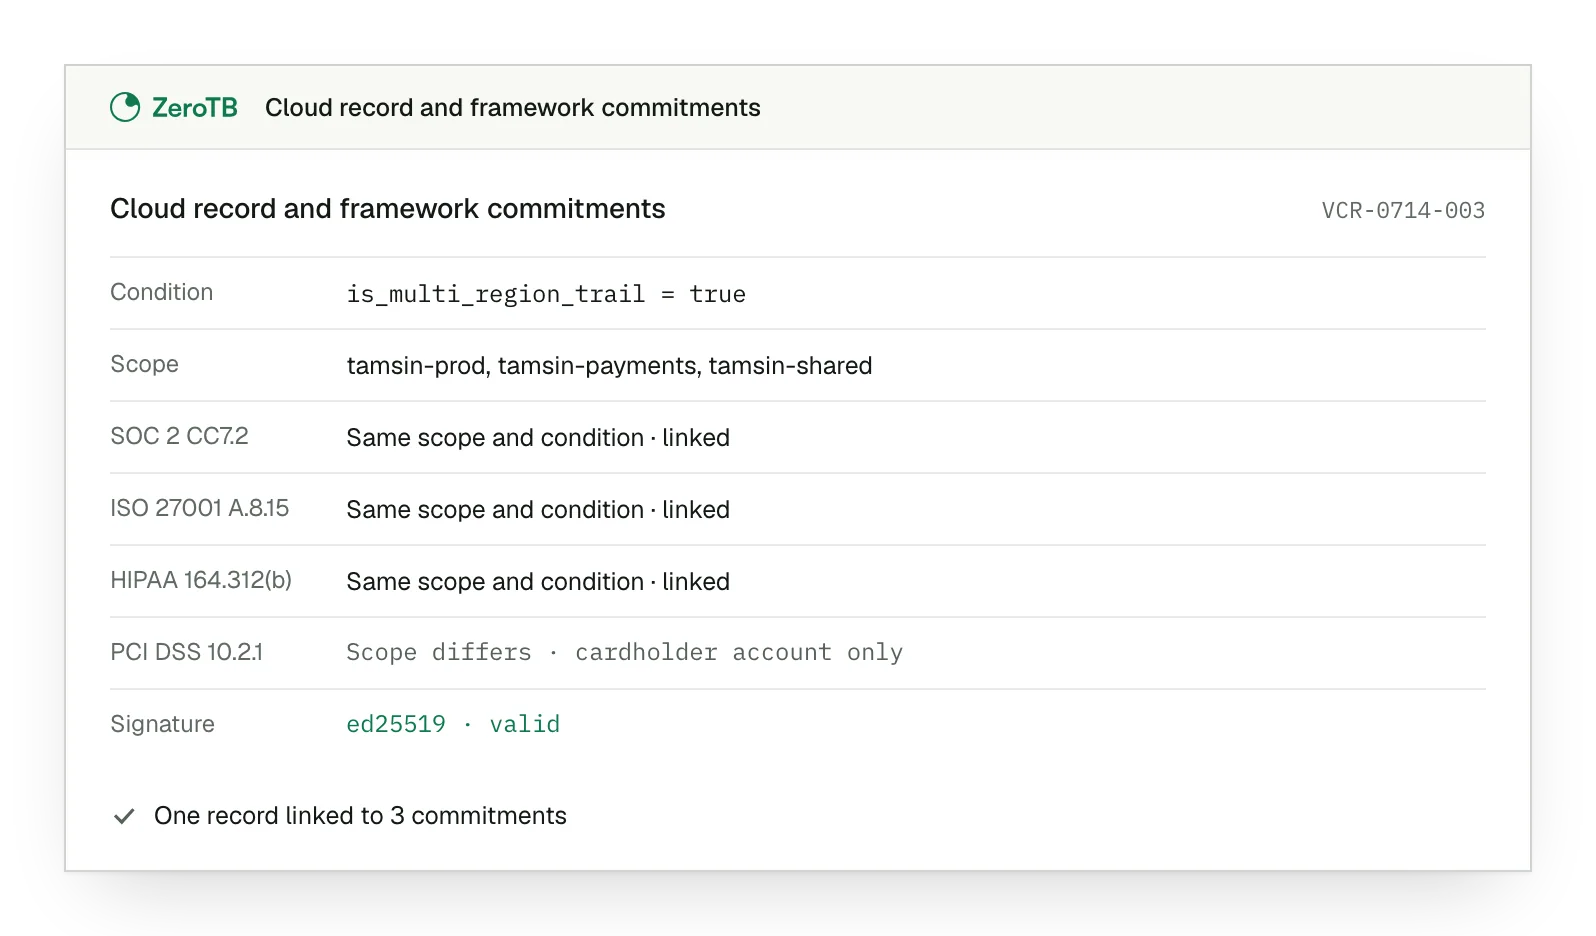
One restored control can support SOC 2, ISO 27001 and HIPAA requirements.
Talk to our team
Talk with our team about AWS controls needing attention and how repairs move through engineering.
FAQ
Does AWS's SOC 2 report cover our AWS configuration?
AWS's SOC 2 report covers AWS's part of the shared responsibility model. Your team remains responsible for keeping your accounts and settings compliant.
What does an AWS Config compliance result tell us?
An AWS Config result answers whether a resource meets a rule. For compliance, that rule must match your own requirement and cover the relevant resources.
How much of our AWS compliance work can run automatically?
ZeroTB runs AWS security compliance checks using approved logic and granted permissions. AI can investigate and propose a fix. People authorize material changes and decide exceptions.
Does a disconnected AWS source mean a control has failed?
A disconnected AWS source means the current condition is unconfirmed. ZeroTB shows unknown, stale or disconnected until a fresh observation establishes whether the requirement holds.
Can production and test environments have different requirements?
Production and test environments can have different requirements when the approved commitment or exception allows it. A check names its environment and the setting expected there.
Does this cover infrastructure changes made with coding agents?
ZeroTB checks AWS settings changed by coding agents against the same commitment. The deployed setting must still meet the approved requirement.
Start with the Pilot
In eight weeks, the Pilot maps up to 25 commitments and takes two real control gaps through verified restoration.