ZeroTB's healthcare compliance software and team keep HIPAA and SOC 2 engineering controls working after audits.
Works with the stack you already run


ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA.
Healthcare compliance software covers policies, training and controls
Healthcare compliance software helps organizations meet HIPAA and other rules through policies, training and incident reports. ZeroTB combines software and hands-on work to maintain healthtech engineering controls under HIPAA and SOC 2.
Who it serves. We support US healthtech companies with 25 to 250 people past their first audit
What it covers. ZeroTB maintains safeguards across accounts, devices, repositories and cloud settings
What it keeps. ZeroTB keeps commitments, checks, repairs and evidence together
Broken access safeguards create gaps in two programs
Changed account permissions can leave unapproved access open under both HIPAA and SOC 2. Handling the same failure separately means coordinating repairs and evidence twice.
Someone still has to find and repair the failed safeguard before it returns as an audit finding.
Account permissions change
Unapproved access remains open
Two compliance programs face gaps
Each failed safeguard keeps an owner until verified
ZeroTB assigns failed HIPAA and SOC 2 safeguards to an owner and carries the repair through to a checked result.
Confirm requirements
AI extracts report and policy commitments. Your team confirms their meaning and scope.
Check daily
We check daily. Each failure gets an owner and response window. People decide exceptions.
Prepare repairs
We draft a runbook, pull request or scoped action for the responsible team's review.
Authorize changes
People approve material changes. We start read-only. Scoped, revocable API permissions require opt-in.
Verify and record
ZeroTB verifies repairs and signs a Verified Control Record of action, approval and result.
Example of restoring access under both compliance programs
This HIPAA and SOC 2 example keeps work access open. ZeroTB blocks a personal-account path and sends the device-hardening work to its owner.
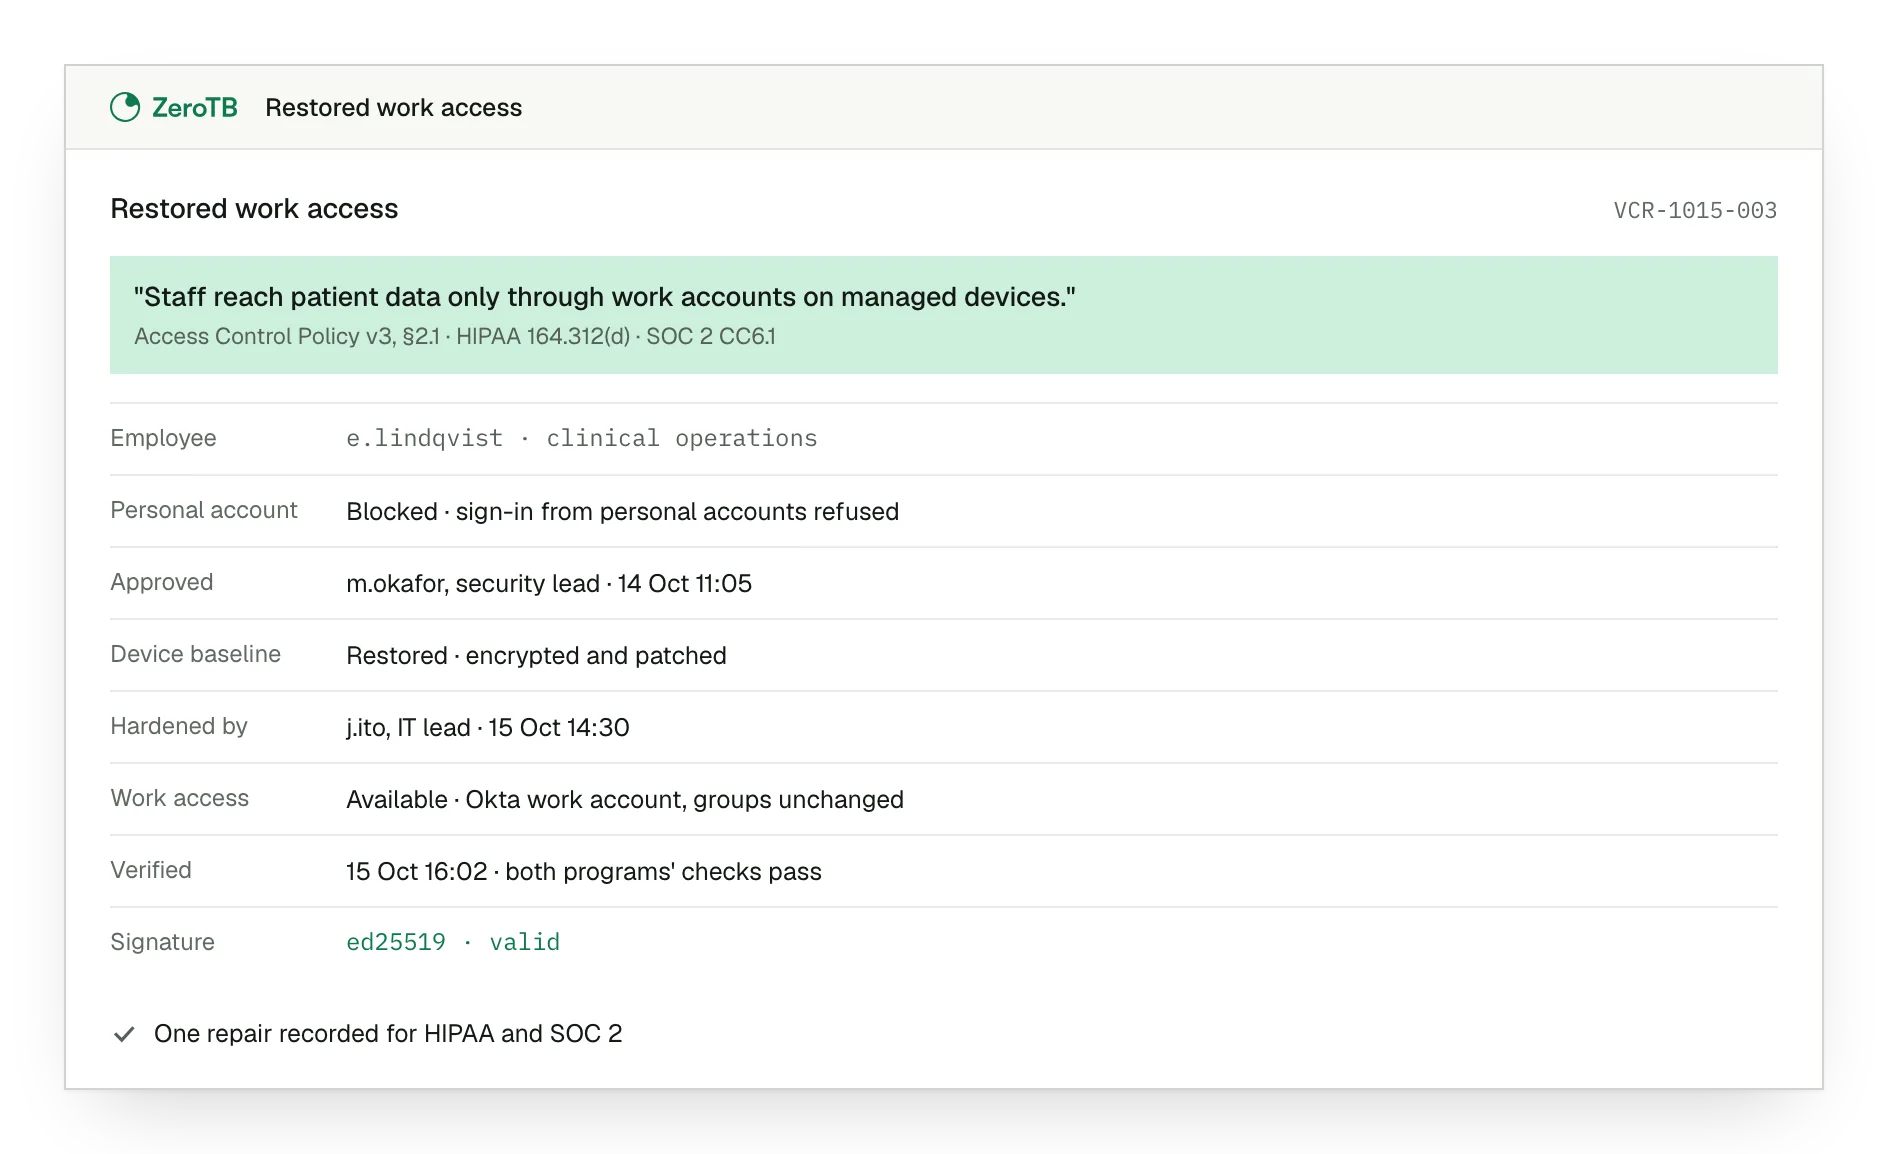
Linked requirements. The account and device requirement connects HIPAA and SOC 2 commitments.
Blocked account path. Blocking the personal account closes its route to company information.
Restored device protections. The device meets the required baseline after its owner completes the hardening work.
Approved work access. The employee can still use the work access that the requirement permits.
Shared safeguards let one repair serve both frameworks
HIPAA and SOC 2 overlap in access control, logging and encryption. ZeroTB operates shared safeguards so one repair can support both where requirements match.
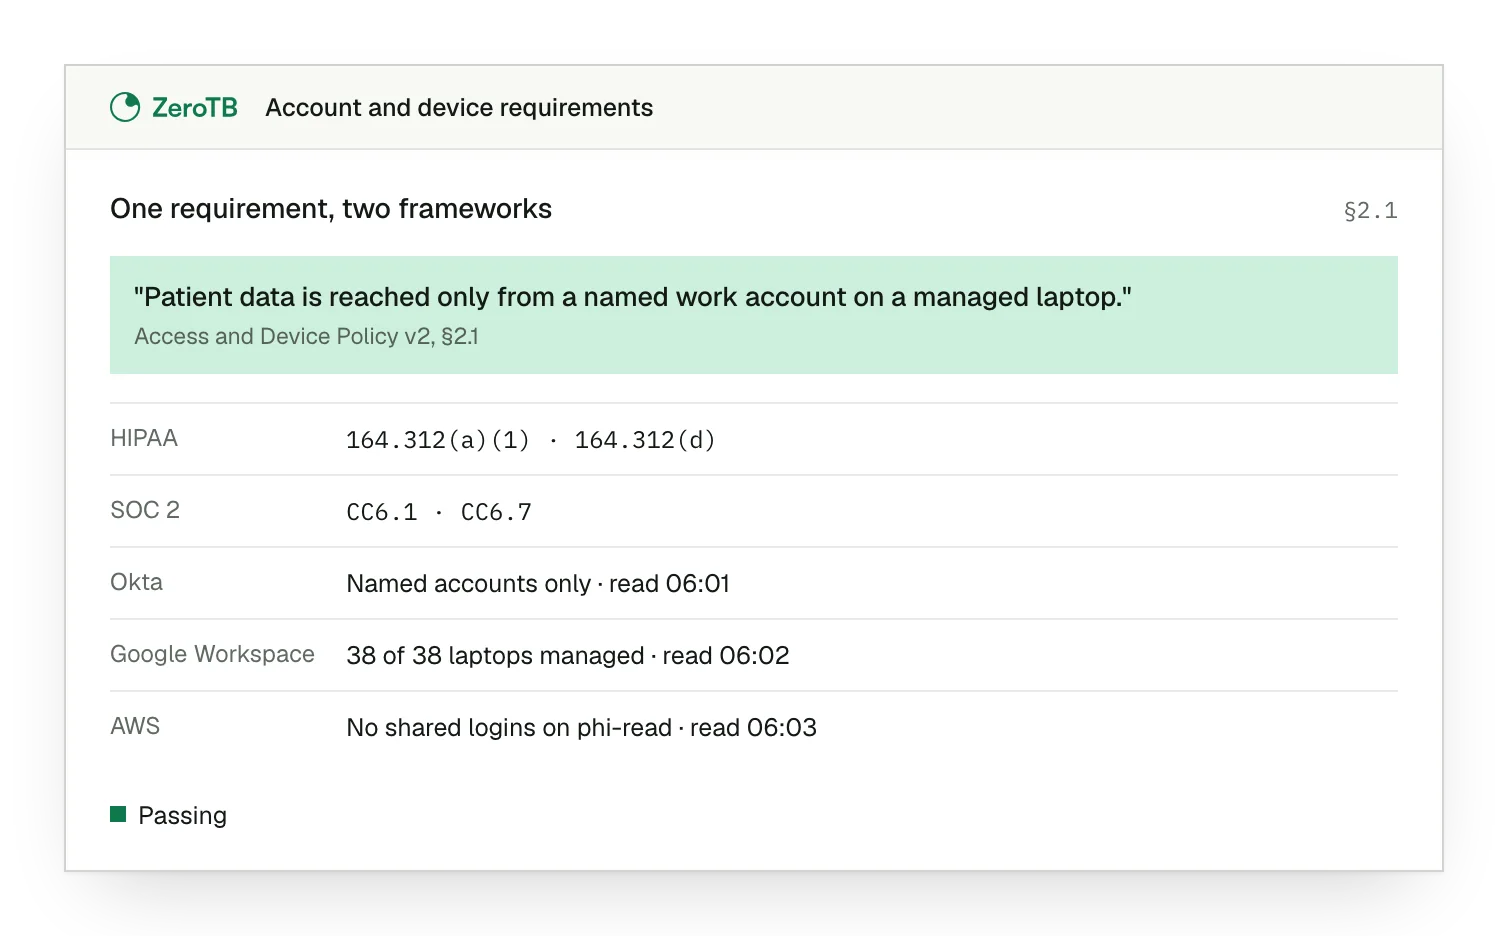
Map each requirement. Each commitment keeps its own scope, owner and expected evidence
Repair once. One restored control can satisfy matching requirements in both frameworks
Schedule people work. We assign training, vendor reviews, incident exercises and policy reviews, escalating overdue work
Healthcare compliance tools cover different parts of HIPAA
Healthcare compliance software often covers one or two areas. A care provider's staff training and a healthtech company's engineering safeguards need different support.
| Task | Policy and training suites | HIPAA program software | Compliance-automation platforms with crosswalks | ZeroTB |
|---|---|---|---|---|
| What it covers | Staff policies, training, incident reports and credentialing | Risk assessments, policies and business associate agreements | Evidence mapped across SOC 2 and HIPAA | Engineering safeguards in accounts, devices, code and cloud |
| Who carries the repair | Staff complete assigned tasks | Your compliance officer | Your team, from alerts | ZeroTB prepares repairs, your team approves |
| What an auditor reads | Training and policy records | Risk assessment and policy documents | Evidence per mapped control | Signed Verified Control Record per repair |
| Fits when | Care providers run staff compliance | The HIPAA program needs building | Your team runs both frameworks itself | 25 to 250 people, safeguards keep drifting |
ZeroTB checks the systems behind a healthtech service
ZeroTB checks work accounts, devices and code against your HIPAA and SOC 2 commitments in the systems you already use.
We read work-account and sign-in settings to find access outside the approved requirements.
We check branch rules, required reviews and CI gates against development requirements.
We compare cloud configuration with the settings your commitments require.
We check enrollment, encryption and patching against the policy baseline.
Our team has run healthtech security and IT
Our team has managed healthtech accounts, devices and security responsibilities, and taken companies through SOC 2 and ISO 27001 programs.
Ran healthtech security. Our team ran security and IT across Asia-Pacific for a US healthtech company
Took companies through audits. Our experience includes SOC 2 and ISO 27001 programs
Audited ourselves. ZeroTB is independently audited, runs this lifecycle internally and provides its report under NDA
Talk to our team
We can discuss where account, device or development changes leave gaps in your HIPAA and SOC 2 safeguards.
FAQ
Do SOC 2 controls cover HIPAA?
SOC 2 controls can cover some HIPAA safeguards, including access control, logging and encryption. Each program still has its own requirements. ZeroTB keeps their scopes clear.
Can we use controls we have already documented?
ZeroTB can use documented controls, reports and policies as commitments. Your team confirms the scope, owner, cadence and expected evidence for each.
Can ZeroTB cover changes made by our coding agents?
ZeroTB checks the repositories your coding agents change: branch rules, required reviews and CI gates. The same development requirements apply, without a connection to the coding agent.
Can we include leavers and access reviews in our scope?
Leavers and access reviews can be included alongside multi-factor authentication and privileges. The approved identity and access requirements determine which accounts ZeroTB checks.
Can our engineers review cloud repairs as pull requests?
ZeroTB prepares infrastructure-as-code pull requests for cloud repairs. Your engineers review and merge them. Direct API actions are opt-in and reversible.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments and takes two real gaps through verified restoration, with signed records of completed work.