ZeroTB maintains cloud compliance by restoring drifted settings through infrastructure-as-code pull requests your team reviews.
Works with the stack you already run


ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA.
Cloud compliance means settings that meet your commitments
Cloud compliance means settings meet SOC 2, ISO 27001 or HIPAA commitments. ZeroTB maintains those controls for US software, AI, fintech and healthtech companies with 25 to 250 people.
Provider secures infrastructure. Under the shared responsibility model, the provider runs and secures its cloud services
You secure configuration. Your team remains responsible for accounts, access and resource settings
Commitments set the bar. Your report and policies define the configuration each resource must maintain
Configuration drift costs you SOC 2 audit findings
Configuration drift occurs when deployments or console edits move production away from its approved baseline. A broken SOC 2 commitment can become an audit finding.
The baseline is approved
A setting changes
Production departs from the commitment
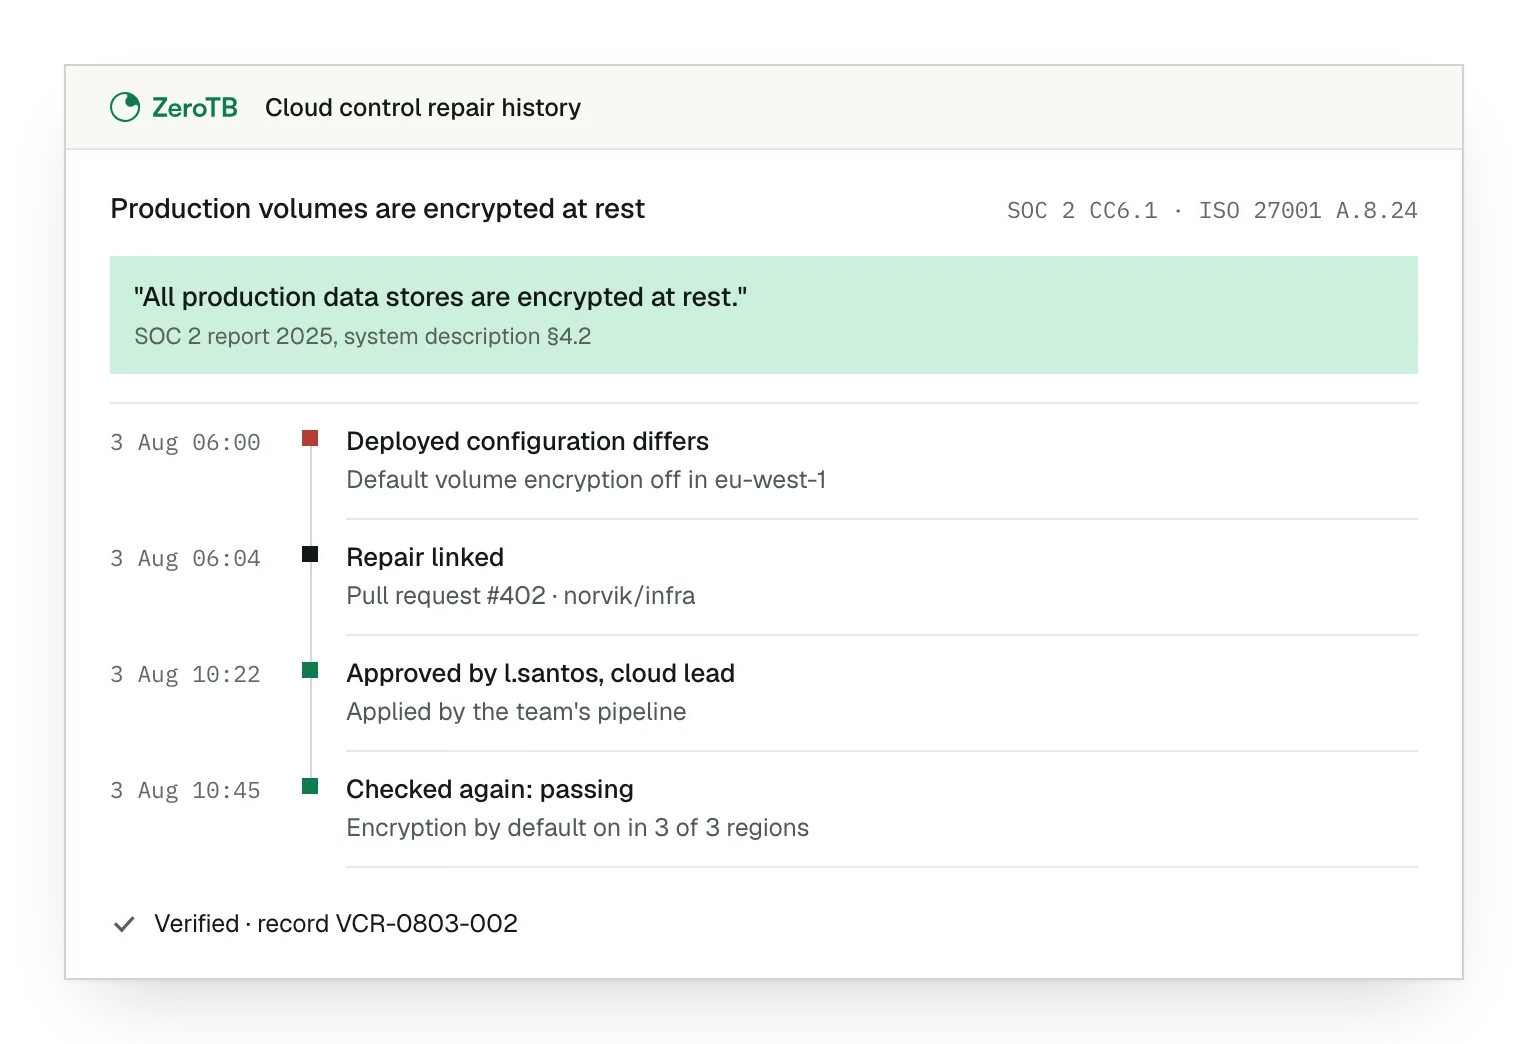
Each finding shows the rule, resource and setting
Configuration drift monitoring shows the owner where production differs from the approved setting, with the resource and source clause attached to the finding.
The owner can read the report or policy clause behind the required setting.
We identify the affected resources within the requirement's scope.
We place the setting observed in production beside the condition you approved.
We check settings again after deployments and console edits, even after an earlier pass.
ZeroTB fixes drift with pull requests engineers review
Engineers receive the proposed cloud repair as an infrastructure-as-code pull request, ready for review through their existing change process.
Confirm the commitment
Your team confirms the covered resources and the condition each must meet.
Check the configuration
We use read-only access to compare production with the approved setting.
Review the change
Your team reviews, approves and merges the infrastructure-as-code pull request.
Check production again
We recheck production and keep its result in the signed, portable Verified Control Record.
Example of restoring an access setting
This example follows a cloud resource whose access exceeds policy. After the reviewed infrastructure repair, a production check confirms that the restriction holds.
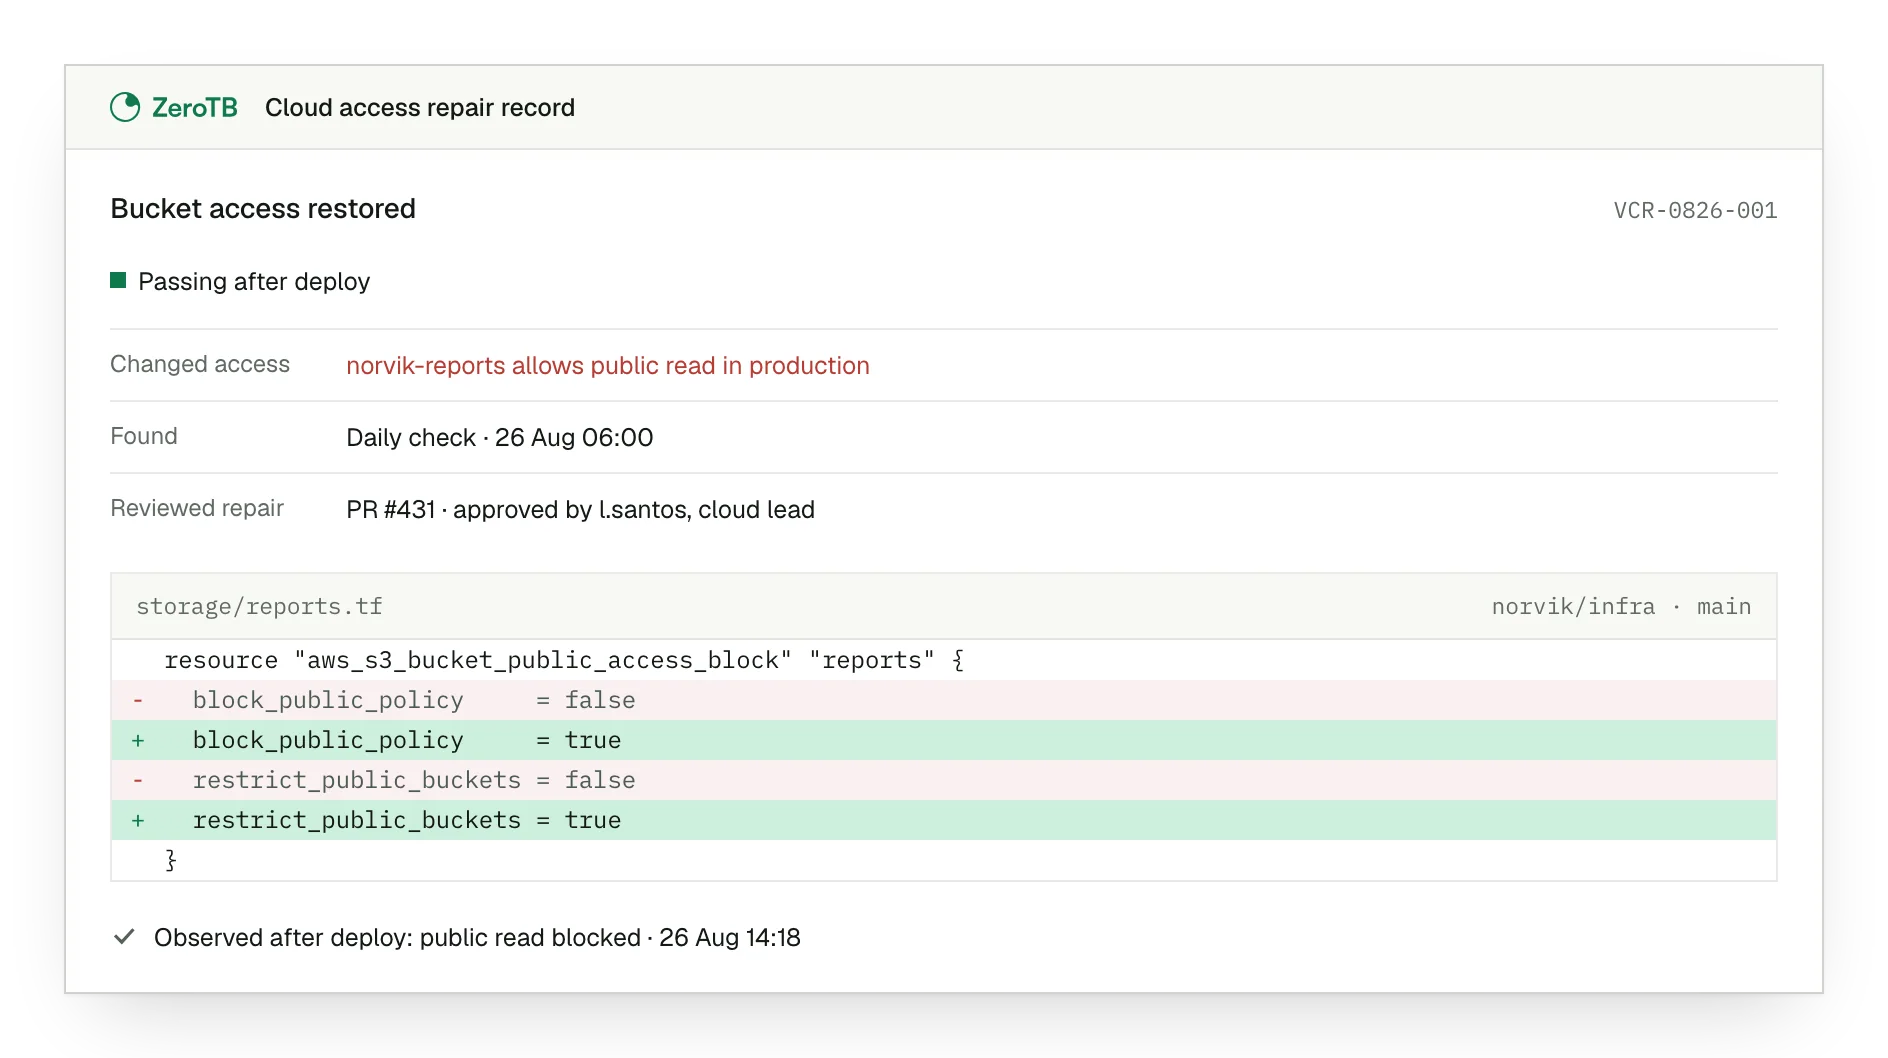
Changed access. The resource's current setting allows access beyond what its policy permits.
Reviewed repair. Engineers review and approve the infrastructure pull request that changes the setting.
Observed result. The check after deployment shows the access restriction operating in production.
Cloud compliance monitoring covers every account in scope
A HIPAA healthtech team's cloud compliance monitoring covers the accounts its commitments name, including resources holding electronic protected health information (ePHI).
Scope from commitments. We map each commitment to the cloud accounts its checks must cover
ePHI accounts included. Accounts holding electronic protected health information belong within the relevant HIPAA scope
Disconnected shows as gap. A disconnected account stays visible as a gap despite an earlier passing check
Talk to our team
Talk with us about cloud repairs your team keeps repeating and account coverage that is difficult to follow.
FAQ
What if the same cloud setting keeps drifting after a repair?
ZeroTB investigates how the cloud setting changed again and can propose a guardrail to block that path. Checks continue as deployments and console edits alter production.
What if the configuration change was intentional?
Your team can approve an exception or confirm a revised requirement for the configuration. Intending the change alone does not make it satisfy the existing commitment.
Can we keep the cloud monitoring tools we already use?
Your existing cloud monitoring tools can stay. ZeroTB handles the work to keep cloud compliance commitments operating and retains evidence from the repairs.
Can one cloud check support SOC 2, ISO 27001 and HIPAA?
A cloud check can support SOC 2, ISO 27001 and HIPAA where requirements overlap. Each commitment keeps its own resource scope and expected condition.
Do cloud checks need permission to change production?
Read-only access lets cloud checks begin. You can later grant revocable writes for specific action classes. Direct API actions require your opt-in and must allow reversal.
Does this cover infrastructure changed by coding agents?
Infrastructure changed by coding agents receives the same checks. ZeroTB examines the deployed settings against the commitment, whoever or whatever made the change.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments and takes two real control gaps through verified restoration.