A team that keeps your controls working
ZeroTB keeps SOC 2, ISO 27001 and HIPAA controls working after the audit.
ZeroTB serves companies of 25 to 250 people
ZeroTB combines software and a hands-on team to keep compliance controls working after the audit for US software, AI, fintech and healthtech companies of 25 to 250 people.
US regulated software. We work with software, AI, fintech and healthtech companies in the US
Past the first audit. Teams often add ISO 27001 or HIPAA to an existing SOC 2 program
No compliance engineers. These companies cannot justify building an internal compliance engineering function
Leftover access and skipped reviews cost audit findings
The program in the audit report starts diverging from production when the auditor leaves.
Laptops miss baselines, departed contractors retain access and repositories skip branch protection. These gaps become audit findings or stall enterprise deals in security review.
Audit records the requirement
Systems change
Control stops working
Your team approves every repair ZeroTB prepares
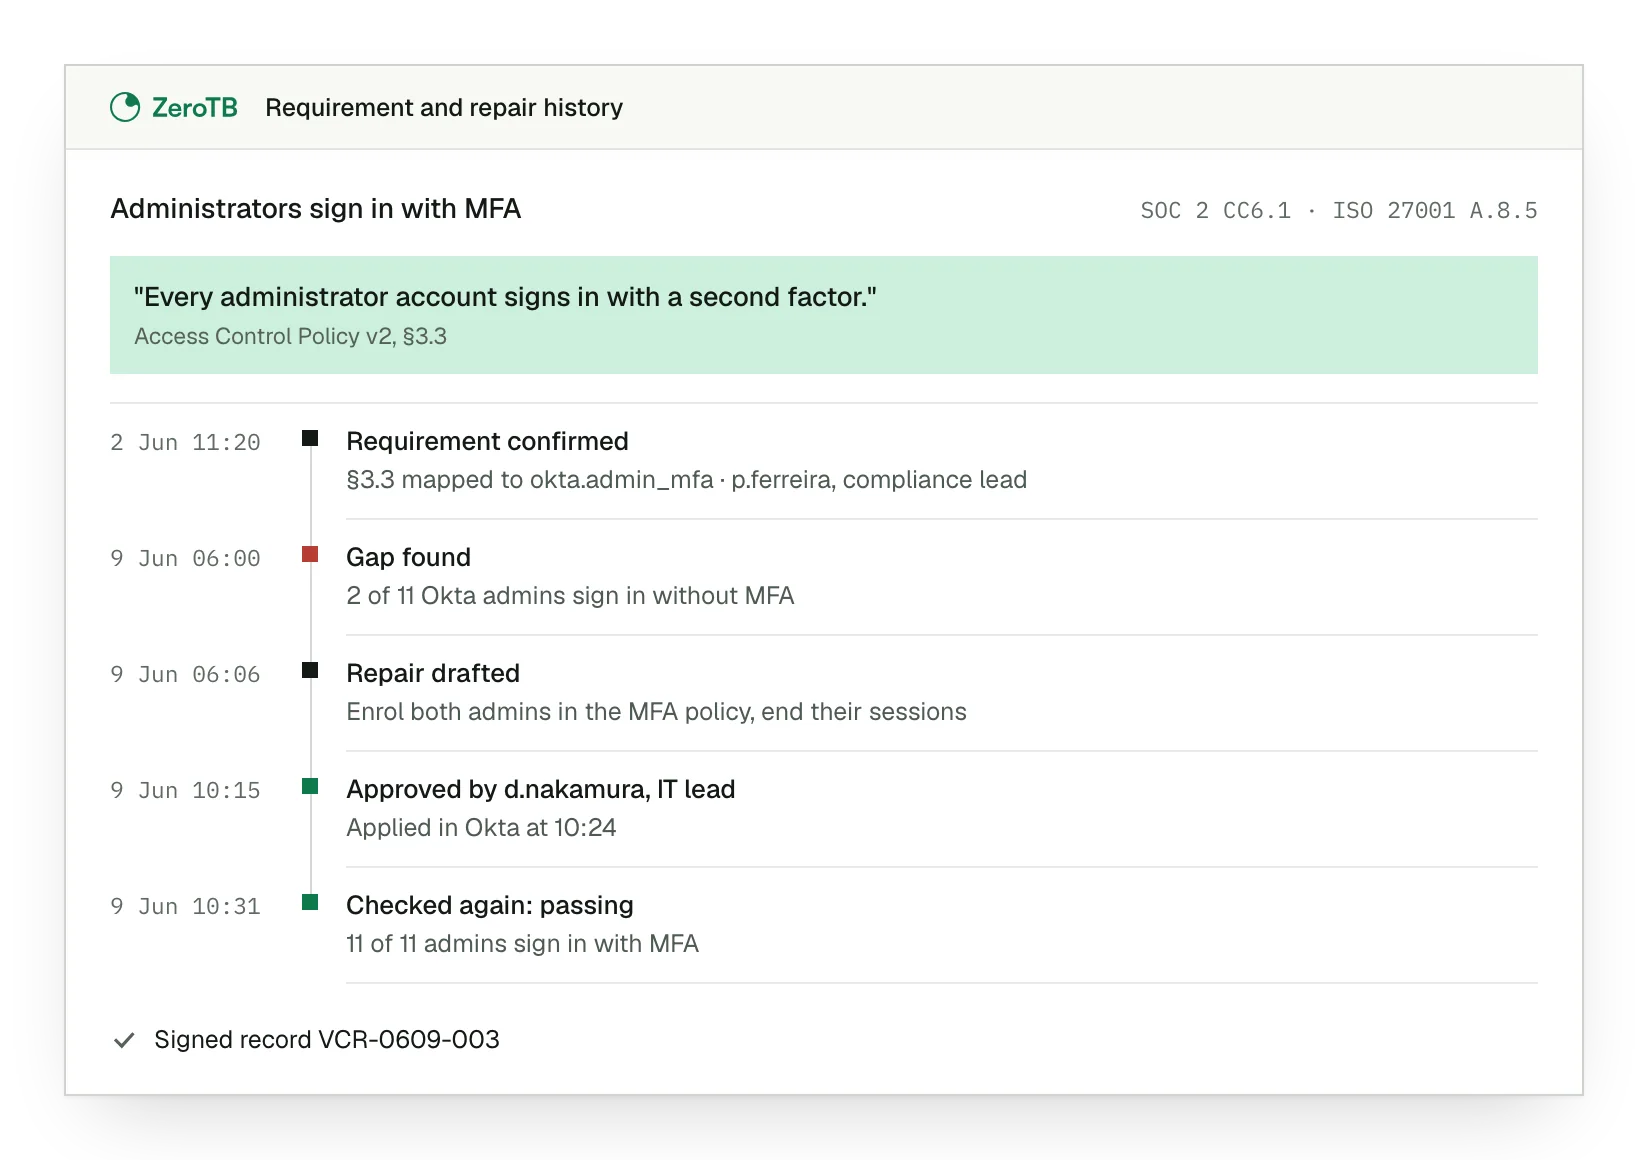
A requirement in your report defines what the system must do. We find the gap, arrange the repair and check the result.
Read commitments
AI extracts requirements and scope from reports and policies for your team to confirm.
Inspect systems
Daily comparisons show where the system falls short of a requirement and why.
Arrange repairs
We prepare the repair with its system owner. People authorize material changes.
Verify results
ZeroTB rechecks the system and keeps a signed Verified Control Record.
Our team has taken companies through SOC 2
Our team comes from security, IT and software engineering. We have handled the work behind SOC 2 programs and answered auditors directly.
Our team ran day-to-day security and IT across Asia-Pacific for a US healthtech company.
At a services firm, our team took clients through SOC 2 and ISO 27001 programs.
The people building ZeroTB also work directly on customer delivery.
Talk to our team
We can discuss the controls that keep failing after your audit and where our team can carry the repair work.
FAQ
Is ZeroTB software or a service?
ZeroTB combines software and service: daily checks against commitments, with our team preparing and carrying repairs. Control operations is the continuing service.
Which companies does ZeroTB work with?
ZeroTB serves US software, AI, fintech and healthtech companies of 25 to 250 people that have completed an audit and own both the requirement and the fix.
Can ZeroTB take us through our first SOC 2 audit?
ZeroTB does not perform audits or provide a first SOC 2 report from scratch. We keep existing controls working. Certification alone falls outside the engagement.
Is ZeroTB itself independently audited?
ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA. See Security.
Where do our commitments and evidence stay?
ZeroTB keeps commitments, checks, repairs and evidence together. Your auditor reads the Verified Control Record in ZeroTB, and you retain a portable signed copy.
What access would we grant at the start?
ZeroTB starts with read-only access. Write access is scoped to classes of action and remains revocable.
How do we get in touch with the team?
The Start a review form reaches our team, which replies within one business day. Contact has the details.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments and takes two real control gaps through verified restoration, with portable evidence.