Beside cloud security posture management tools, ZeroTB carries gaps caused by coding agents to verified restoration.
Works with the stack you already run


ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA.
Cloud security posture management tools check cloud settings
Cloud security posture management (CSPM) tools check cloud misconfigurations and drift. ZeroTB's software and team maintain controls after audits for US software, AI, fintech and healthtech companies with 25 to 250 people.
Find cloud misconfigurations. CSPM tools assess multicloud settings and guide or automate cloud repairs
Cover wider commitments. SOC 2 extends beyond CSPM to repository rules, access, and people and process controls
Check changed systems. ZeroTB checks GitHub, AWS, Google Workspace, identity providers and endpoints
Compliance drift from coding agents becomes audit findings
Compliance drift leaves SOC 2 report commitments unmet as agents change repositories, cloud settings and accounts at machine speed.
Unchecked gaps become audit findings, forcing engineering to repeat investigations and gather screenshots and messages. ZeroTB can close gaps when they appear.
An agent changes a setting
Nobody checks the commitment
The auditor reports a finding
Keeping your commitments working every day
ZeroTB checks your commitments against your systems each day and carries detected gaps through to verified restoration. The same responsibility continues as the company changes.
Confirm requirements
AI identifies commitments in your report and policies for your team to confirm, including scope and required evidence.
Check daily
ZeroTB compares requirements with system state daily, showing the source clause, observation and reason for each finding.
Prepare repairs
Each gap gets an owner and response window before ZeroTB prepares a runbook, pull request, API action or guardrail.
Authorize changes
Your team authorizes material changes before the responsible person or ZeroTB executes the repair within agreed permissions.
Verify and record
You receive verified restoration and a signed record of the commitment, before-and-after states, action, approval and verification.
CSPM, SAST and DevSecOps tools check different layers
CSPM and delivery tools still do their existing jobs. ZeroTB takes on the control gaps that require investigation and repair.
| Task | CSPM tools | Static analysis and SAST tools | DevSecOps platforms | Configuration management and policy as code | ZeroTB |
|---|---|---|---|---|---|
| What it checks | Cloud misconfigurations and drift against standards such as SOC 2 | The code itself, through a scan | Security scans such as SAST within the delivery workflow | Enforces the settings that were approved | Your commitments daily across repositories, cloud settings and accounts |
| What it leaves unchecked | Repository rules, account access, people and process controls | Required repository reviews, even when code passes the scan | A repository review rule governing the approved change process | Deployed settings after an agent's change | Your code scans and wider periodic testing still continue |
| Who carries the repair | Guides or automates the cloud fix | Scan results direct the code's owner to the problem | Scan results direct the owner to the problem | Code enforces the approved settings | ZeroTB prepares pull requests, your team approves, ZeroTB verifies the repair |
| What record the auditor reads | Assessment of cloud settings against compliance standards | Results of the code scan | Results of scans run during delivery | Settings written into the approved configuration | Each repair's signed Verified Control Record |
Static analysis and DevSecOps tools miss control drift
Static analysis and SAST scans in a DevSecOps platform check code. Continuous control monitoring checks SOC 2 controls around changes.
A scan can pass without required GitHub reviews. Restored rules can disappear again.
ZeroTB's continuous control monitoring checks report commitments for reviews, required tests and access daily.
Configuration management sets rules, ZeroTB checks them daily
Configuration management and policy as code enforce approved settings. ZeroTB checks deployed settings against SOC 2 commitments daily, showing each finding's clause, state and reason.
Find configuration drift. ZeroTB finds configuration drift by comparing deployed cloud settings with production policy requirements
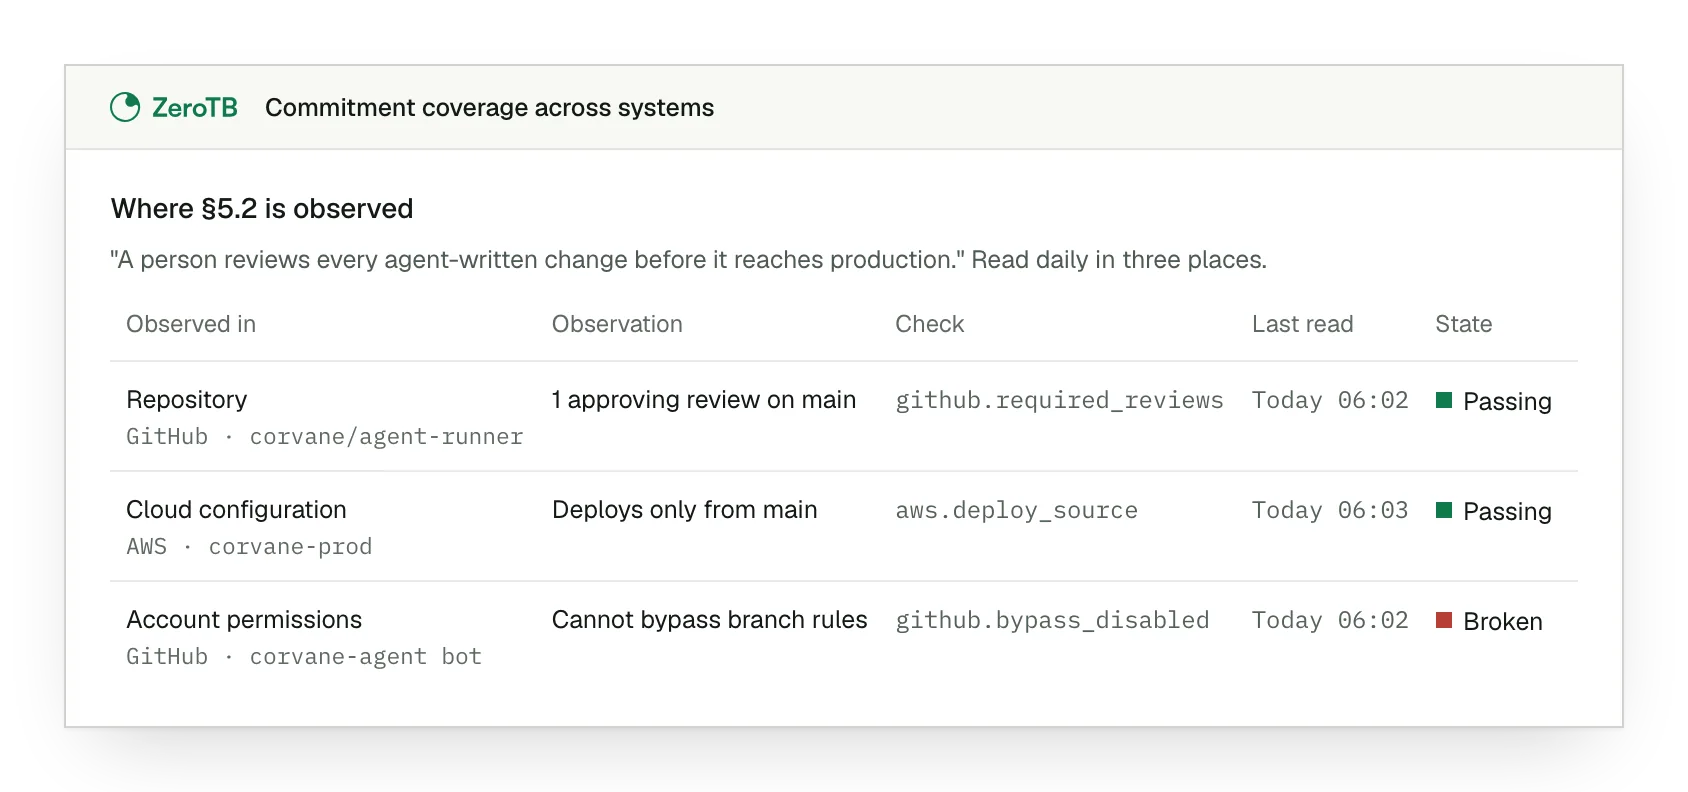
Maintain repository protections. We check GitHub branch rules, required reviews and CI gates on repositories that ship
Resolve excess access. We check privileges, leavers and MFA against approved access, assigning owners to gaps
SOC 2 change management survives agent-written code
SOC 2 change management (CC8.1) still requires the review and testing controls your company committed to when agents change repositories, infrastructure and access.
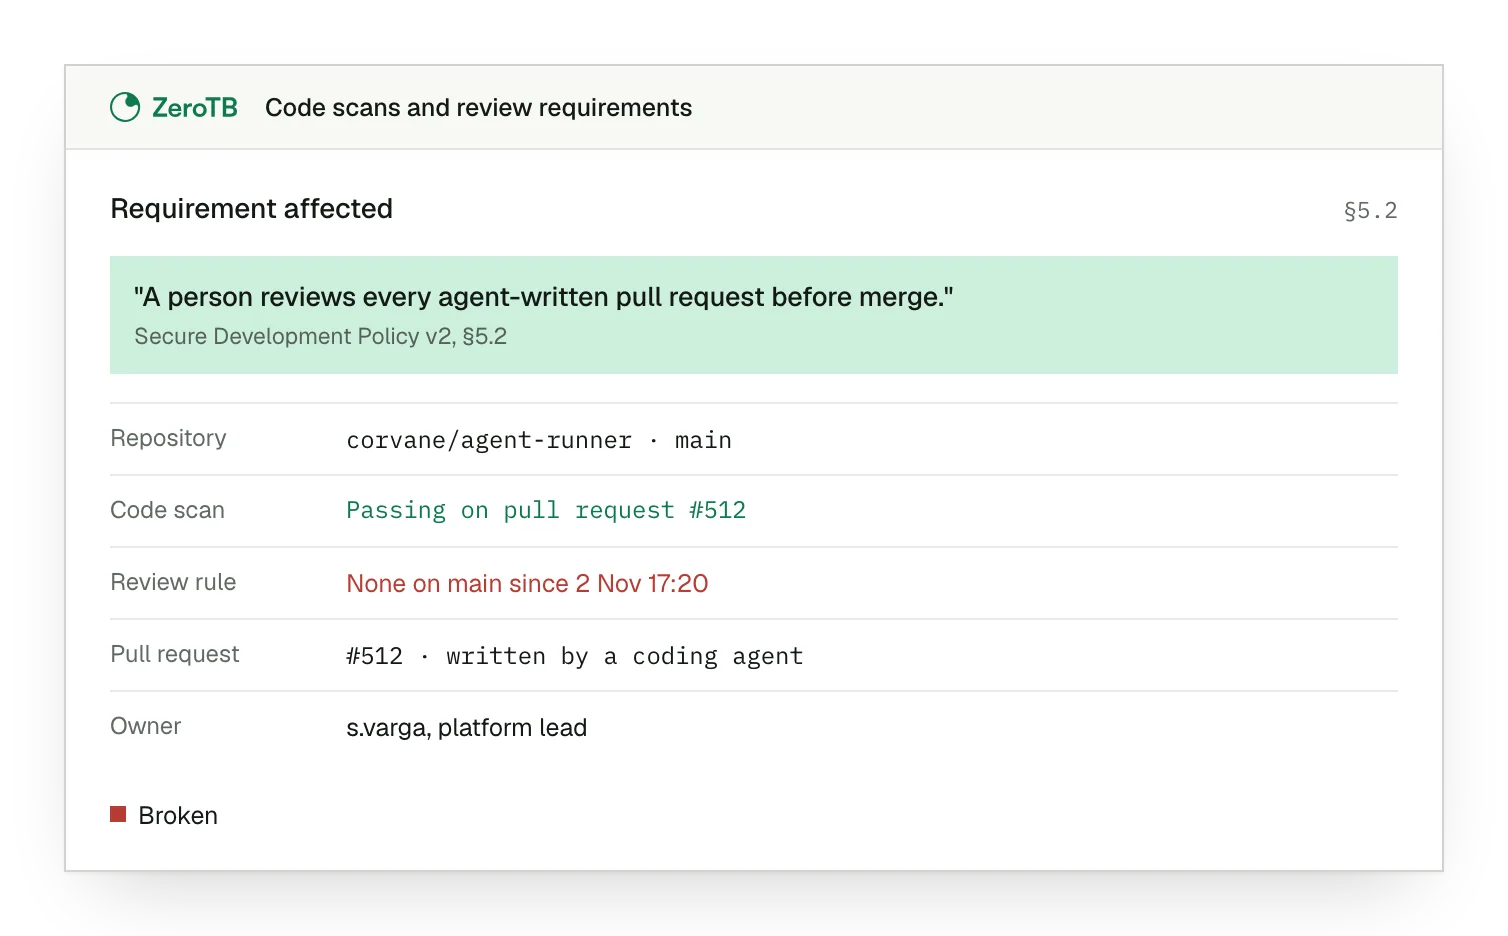
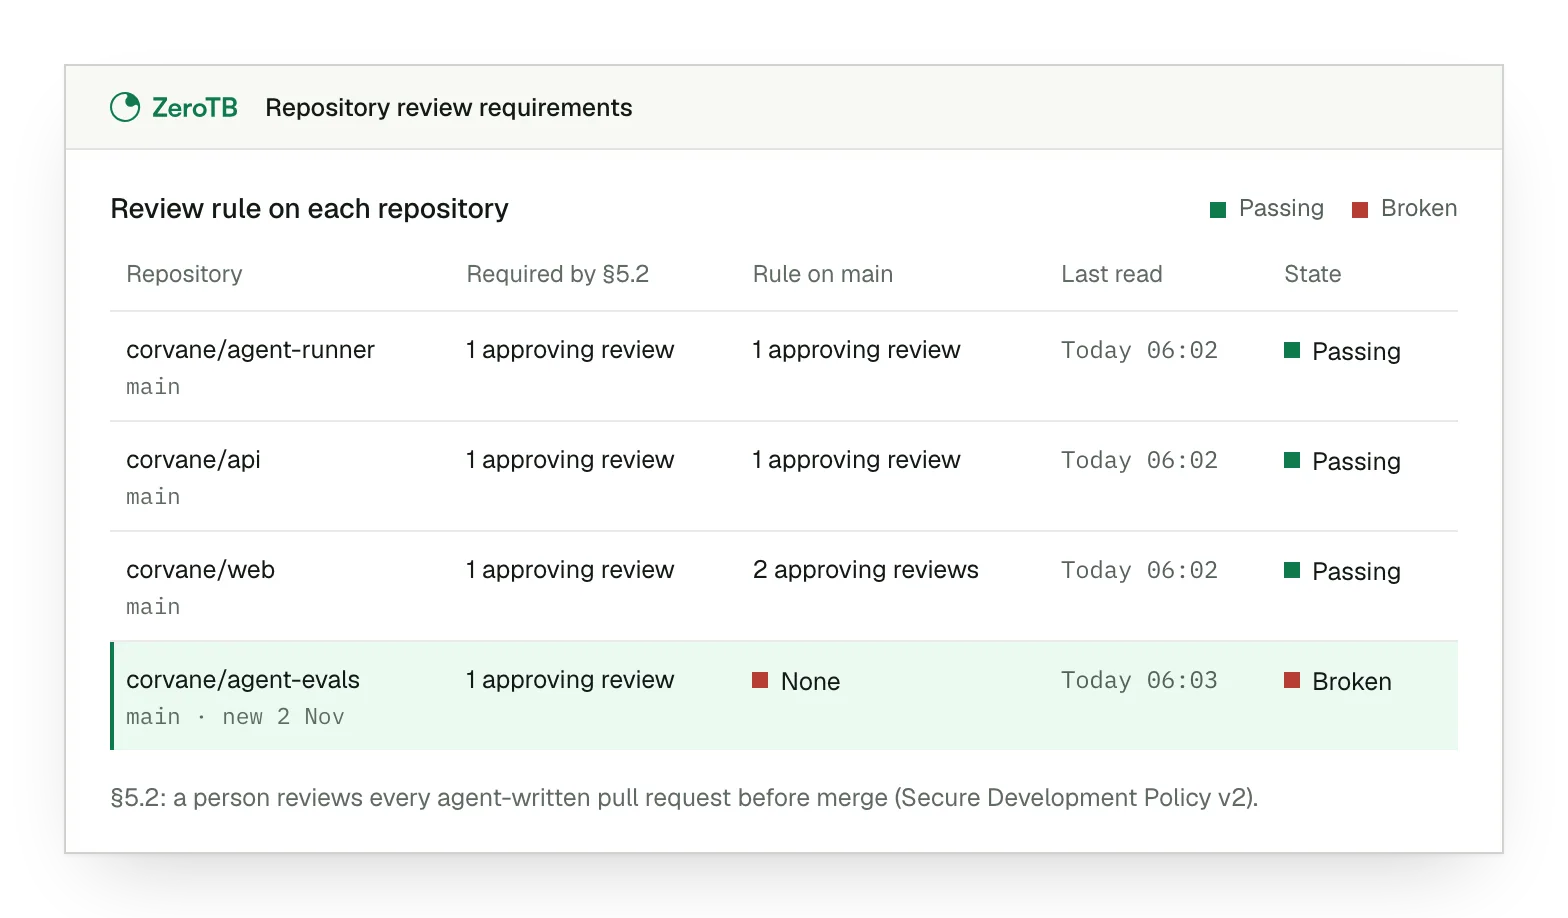
Apply missing branch protection
Agent-written code enters a new repository without the branch protection required by policy.
We prepare the missing review rule as a pull request, and engineering approves it.
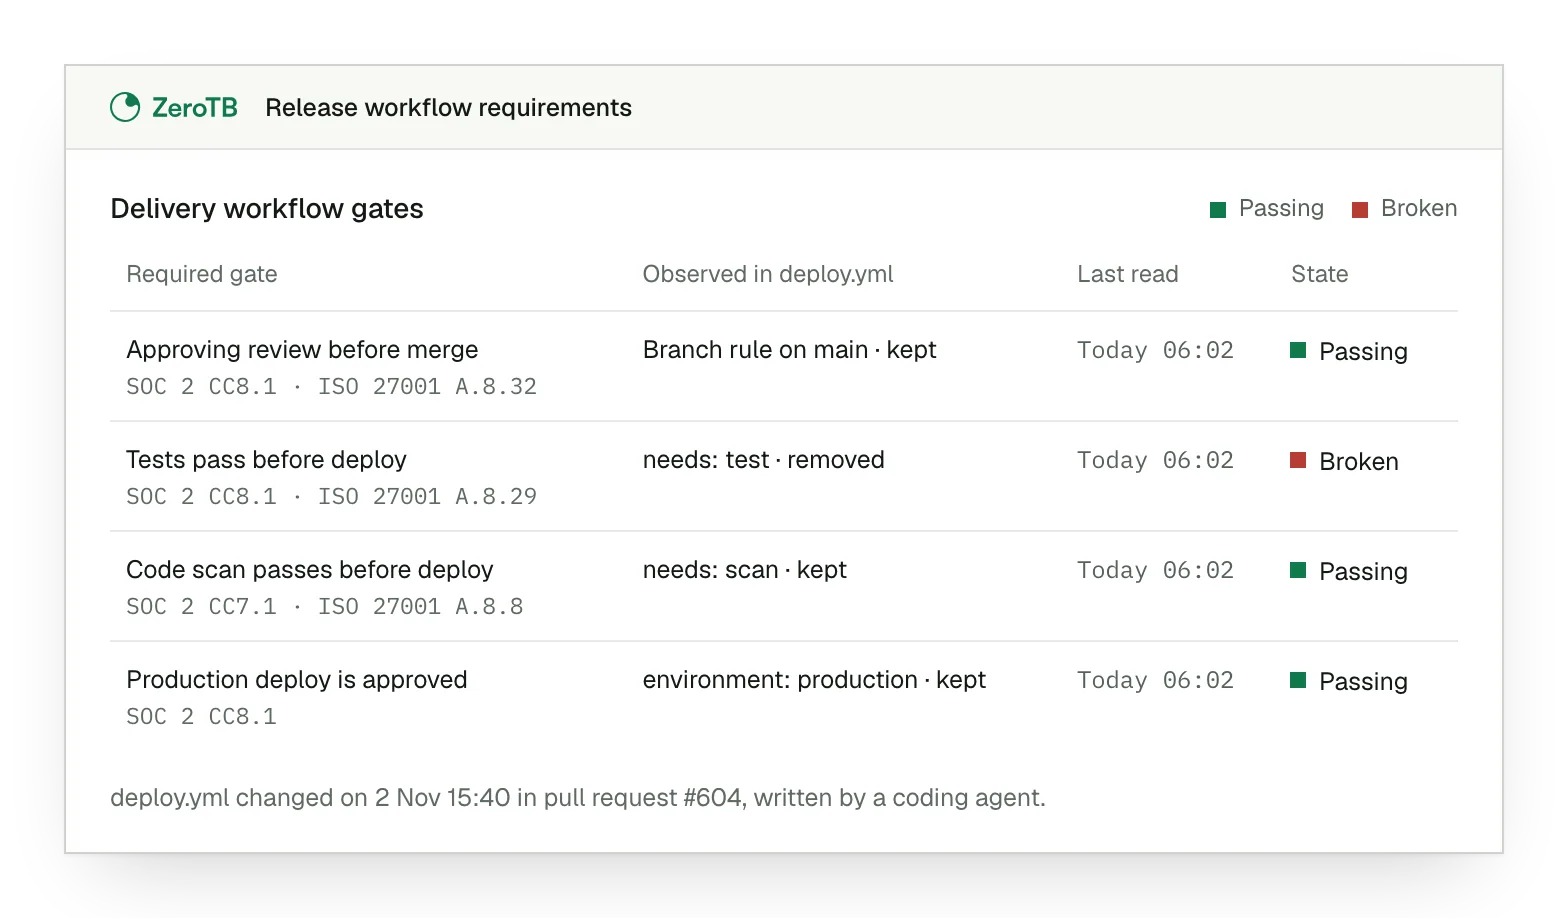
Restore required release gates
An agent edits a delivery workflow, dropping a required test or review from the release.
We prepare the restored gate in release controls for engineering to review.
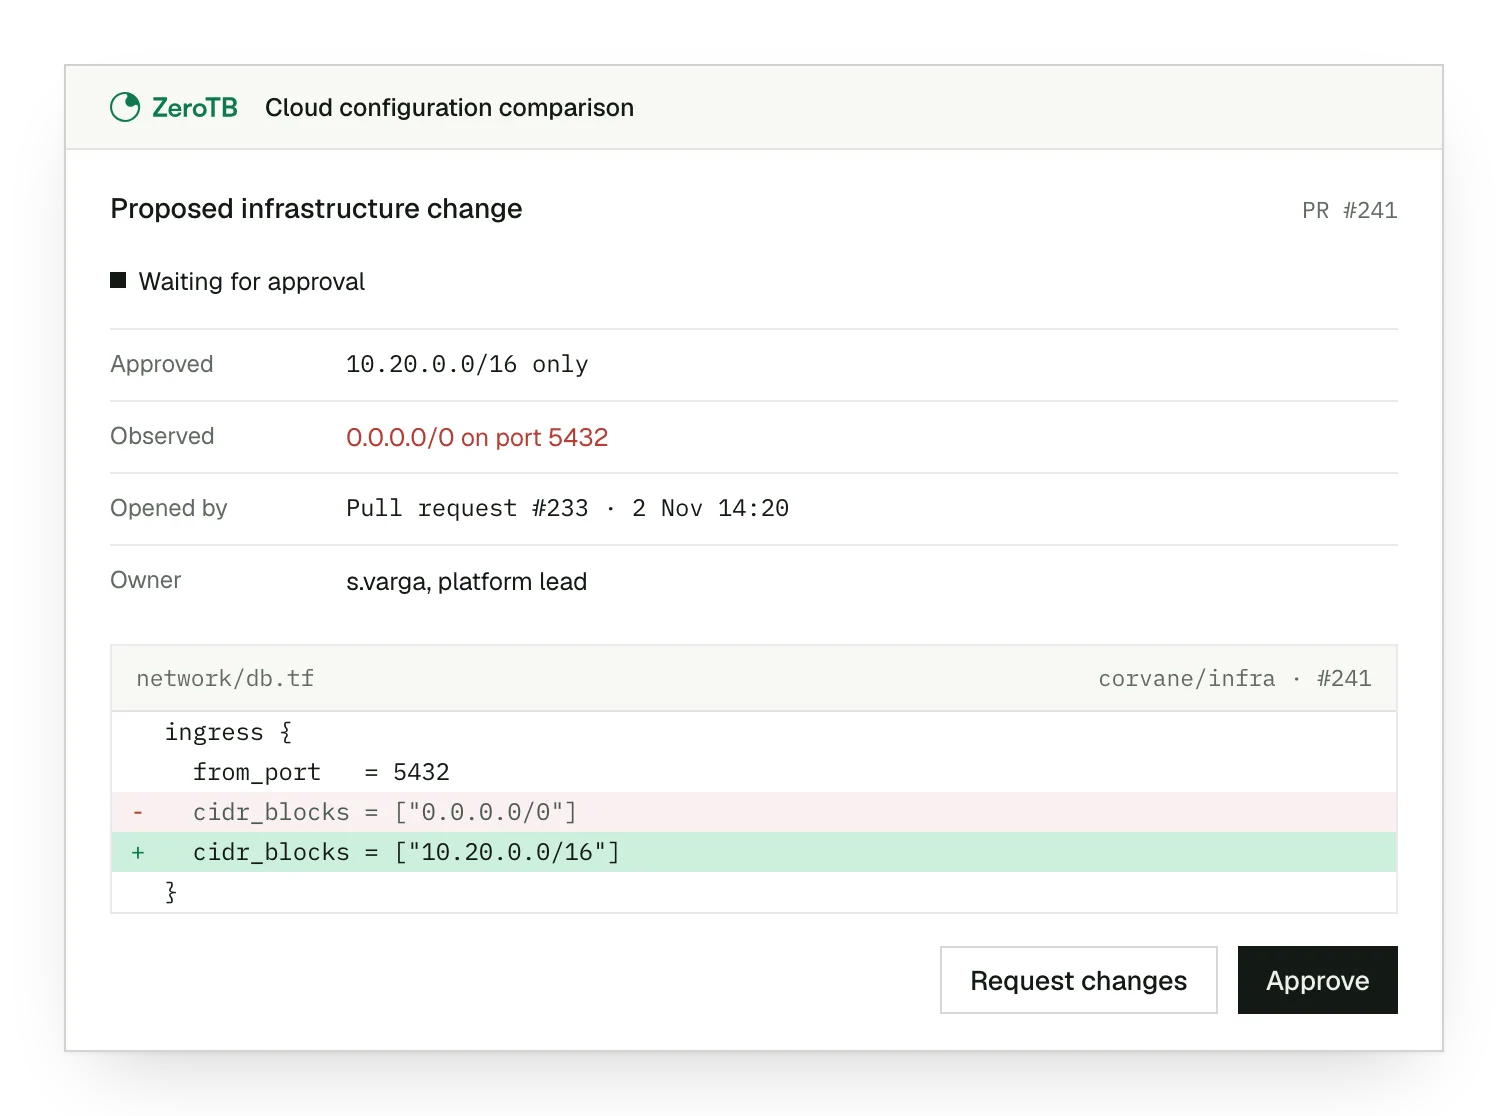
Repair cloud configuration drift
An agent changes infrastructure, leaving a deployed cloud setting outside the configuration policy requires.
We prepare an infrastructure-as-code pull request restoring cloud settings for your review.
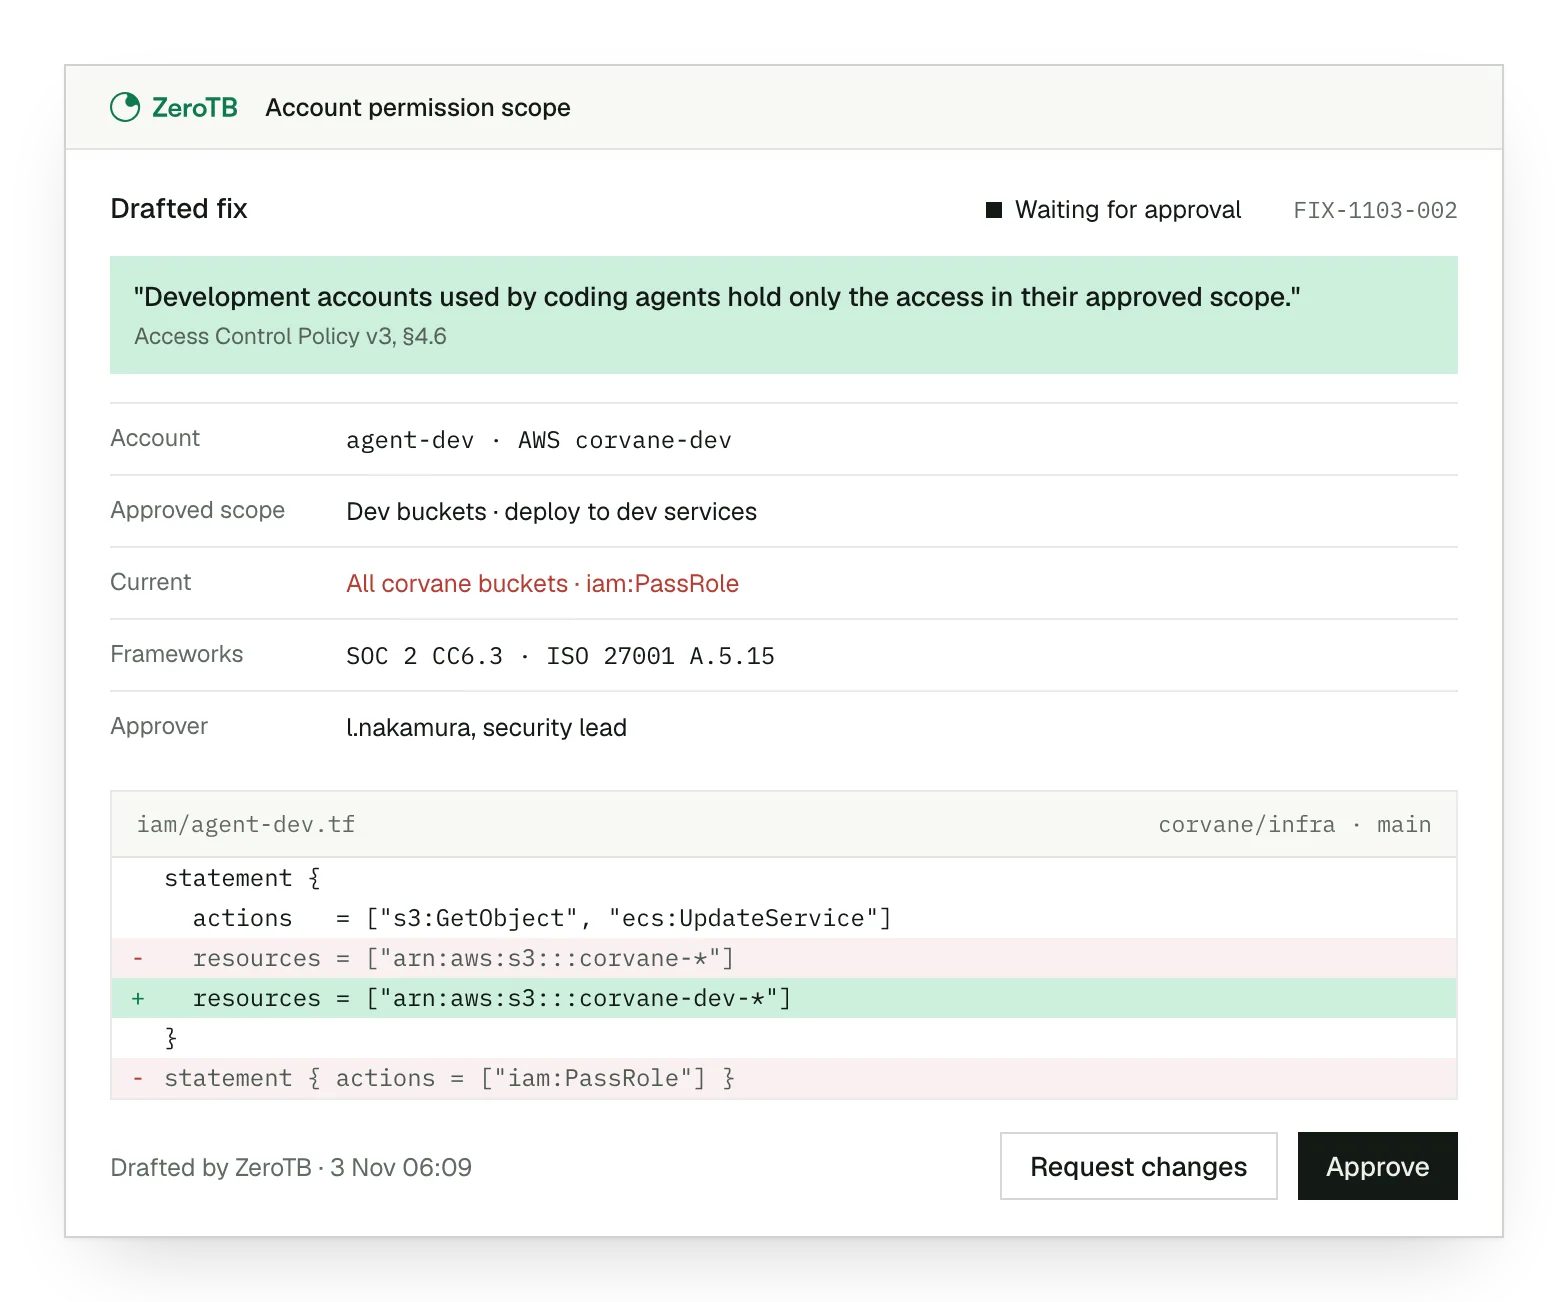
Remove outdated account privileges
A development account retains earlier privileges that exceed what its current work requires.
We list excess privileges for the access owner to approve removing.
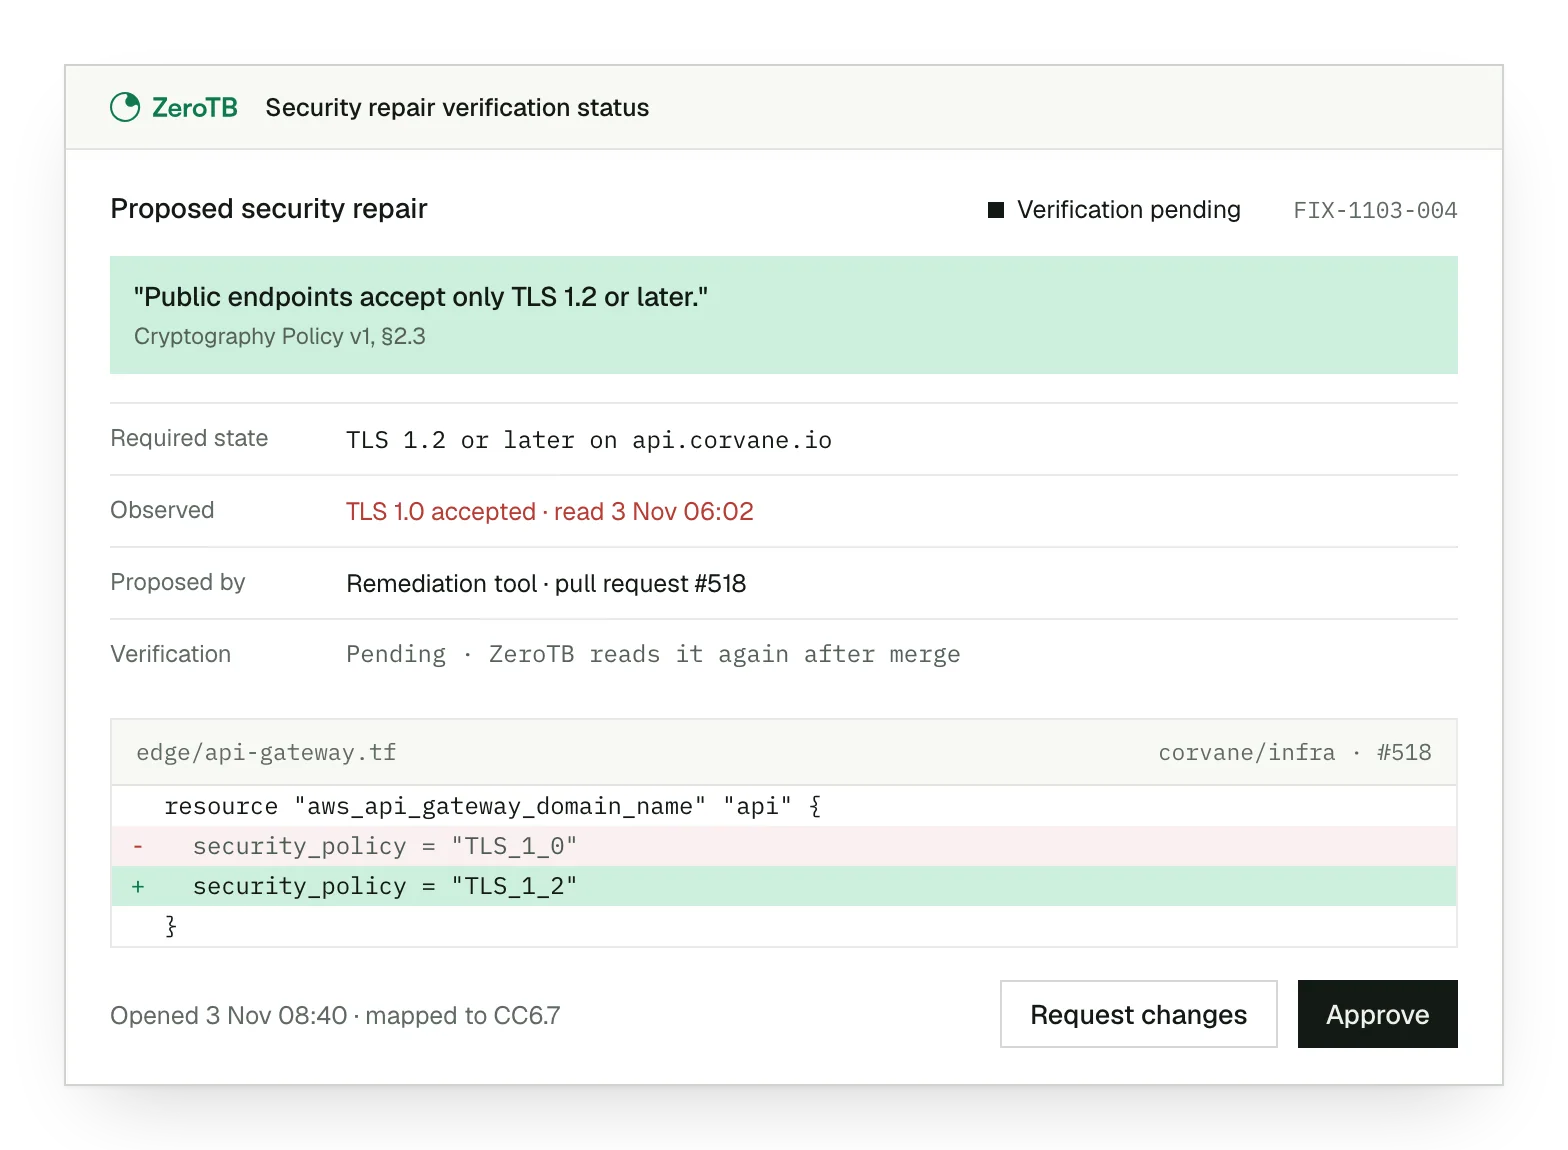
Verify controls after security fixes
Fixes proposed by vulnerability remediation tools such as AWS Security Agent still need compliance evidence.
We check the related commitment after repair and record the result for your team.
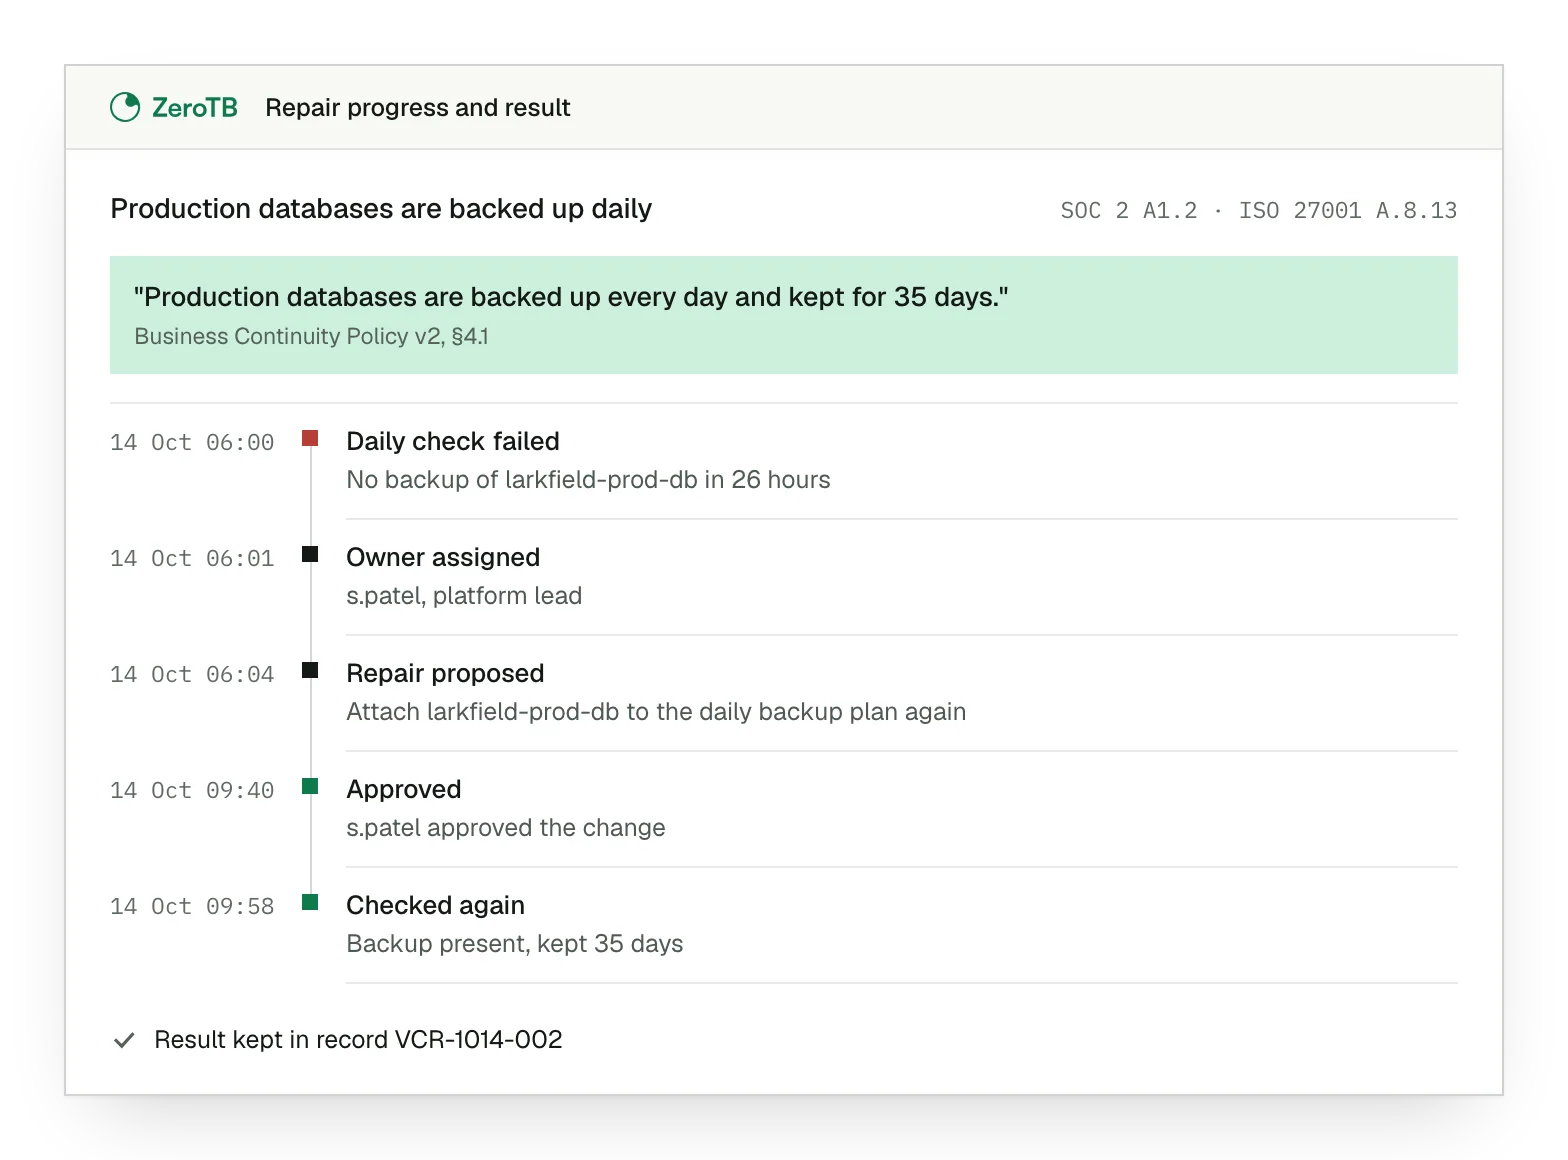
Every repair leaves a signed record
The Verified Control Record keeps the commitment, before-and-after states, action, approval and verification in ZeroTB, where the auditor reads them.
The auditor reads the repair in ZeroTB without asking engineering to reconstruct its history.
You can keep a portable copy of the signed record for the auditor's review.
Unknown, stale and disconnected checks show where current control evidence is missing.
Mean Time to Verified Restoration measures time from detecting drift to verifying the control works again.
Stay compliant with fewer people
ZeroTB takes on recurring control work that would otherwise need a dedicated compliance engineering function, including the repairs and follow-up between teams.
Finish recurring repairs. We carry gaps through verified restoration, sparing an internal compliance engineer the chasing
Reduce team follow-up. We prepare repairs and check systems, reducing follow-up across compliance, IT and engineering
Cover several frameworks. One repair can satisfy SOC 2, ISO 27001 and HIPAA requirements at once
Talk to our team
Tell us where agents change repositories, cloud settings and accounts, and which commitment concerns you.
FAQ
Do CSPM tools cover SOC 2 control drift or only cloud misconfigurations?
CSPM tools check cloud misconfigurations and drift against SOC 2. ZeroTB also checks SOC 2 repository rules, account access, and people and process controls.
How is ZeroTB different from a CSPM tool?
ZeroTB checks cloud, repository and access commitments daily. CSPM tools assess cloud settings against standards. Our team repairs gaps, rechecks controls and keeps a signed Verified Control Record.
What should we look for in a CSPM tool for compliance?
A CSPM tool should cover your cloud accounts, find misconfigurations, map to SOC 2, detect drift and guide or automate repairs. Ask who handles controls outside that coverage.
Does ZeroTB connect to Claude Code or other coding agents?
ZeroTB connects to no coding agent, CSPM, static analysis or DevSecOps tool. ZeroTB checks the systems they change: GitHub, AWS, Google Workspace, identity providers and endpoints.
Does ZeroTB need write access to our repositories and cloud accounts?
ZeroTB starts read-only. Your team reviews and merges repair pull requests. Write access is revocable by action class. Direct API actions are opt-in and reversible. AI cannot independently mark controls healthy or close them.
Does compliance drift detection replace periodic internal control testing?
Compliance drift detection supplements periodic internal control testing. The wider testing plan remains. Reviewers use observations between tests to assess when controls operated and where evidence was missing.
Related pages
Claude Code security
Read about the development controls affected by changes made with Claude Code.
Change and development
Explore the branch rules, required reviews and release checks behind production changes.
Compliance without more headcount
Read how ZeroTB handles recurring repairs across compliance, IT and engineering.
Start with the Pilot
The eight-week Pilot maps up to 25 report commitments and takes two real control gaps through verified restoration. Chosen commitments and repositories define scope. You keep repaired controls and signed records.