ZeroTB keeps the access and change controls that SOX compliance software tests working between audits.
Works with the stack you already run


ZeroTB has undergone an independent audit and operates this control lifecycle in its own compliance program. Its report is available under NDA.
SOX compliance software tests financial reporting controls
SOX compliance software centralizes financial-reporting controls, runs tests and keeps evidence. ZeroTB combines software and people to maintain fintech SOC 2 controls after the audit.
Who it serves. We support US fintech companies with 25 to 250 people past their first audit
What it covers. ZeroTB operates SOC 2, ISO 27001 and HIPAA commitments
What it keeps. ZeroTB keeps commitments, checks, repairs and evidence together
Unchecked access and code changes cost clean audits
A contractor leaves with access still open. A new repository lacks required reviews. Either failure can remain until the next SOC 2 review.
The program record describes the old condition while someone still needs to find the failure and finish the repair.
Control passes its test
Access or software changes
The next review finds the failure
ZeroTB carries each gap to a verified repair
ZeroTB turns report requirements into daily checks and repairs, leaving a signed Verified Control Record when the repaired condition is confirmed.
Confirm requirements
We read reports and policies, then your team approves what each commitment means.
Check daily
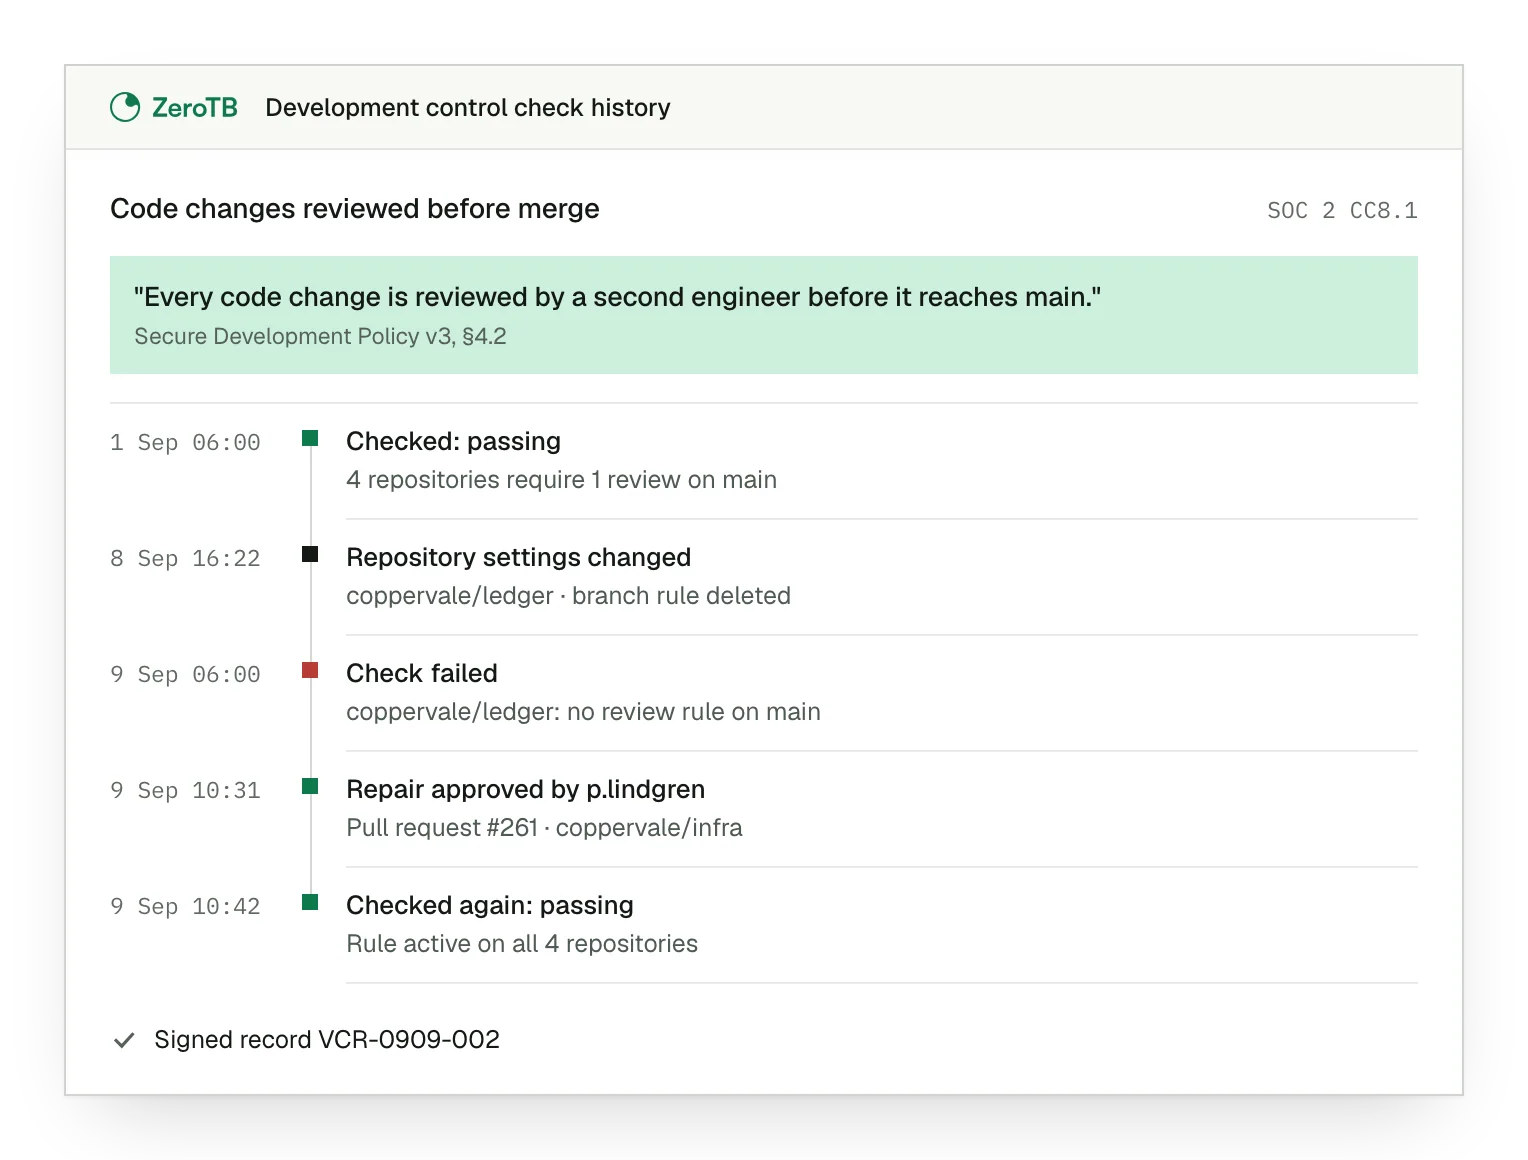
We compare settings daily. Failed checks get an owner and a response window.
Prepare repairs
We prepare a runbook, pull request or API action within agreed permissions.
Authorize changes
People approve material changes. We start read-only, with opt-in, revocable API actions.
Verify and record
ZeroTB checks the repaired state and signs a Verified Control Record.
Example of restoring required code reviews
A missing repository rule let changes skip code review. This change management example restores that rule before later changes enter the protected branch.
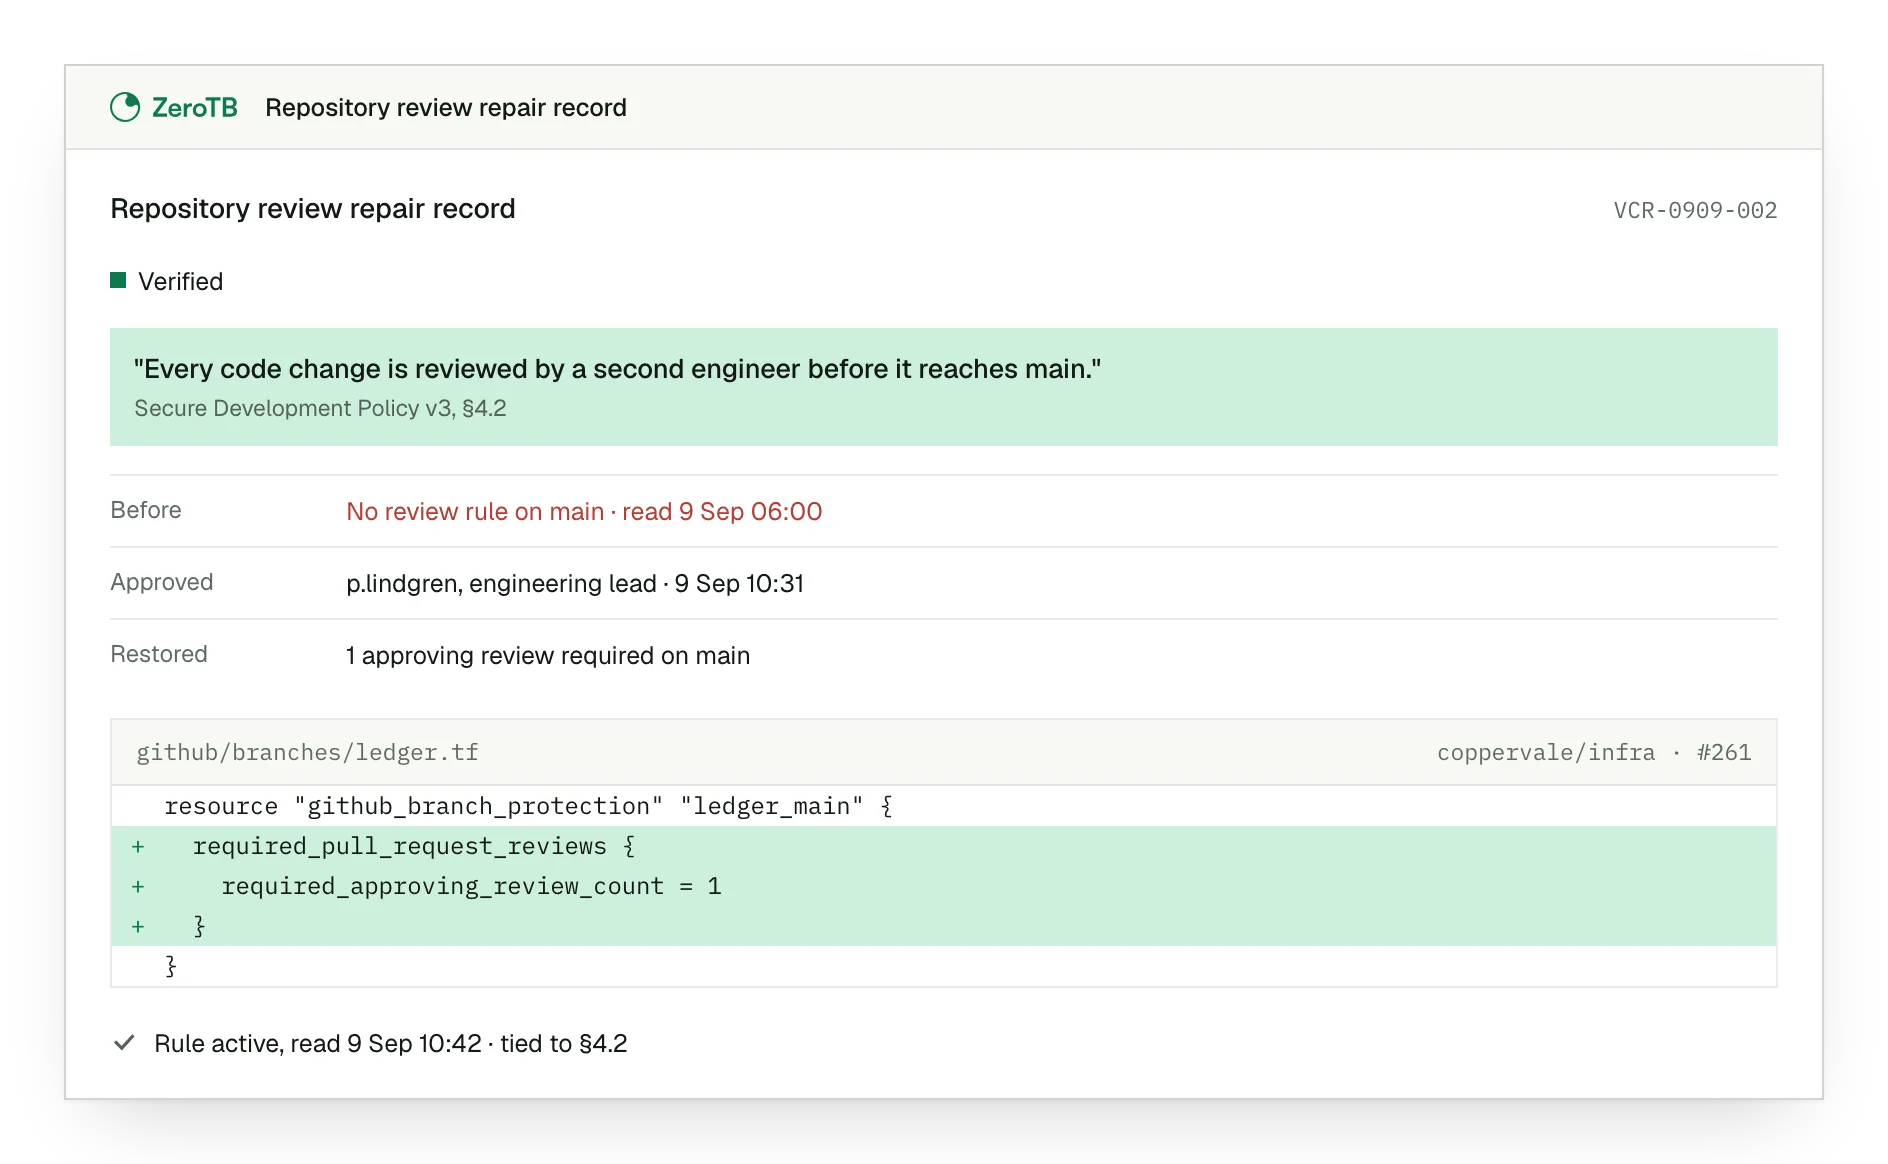
Required review. The commitment requires a review of code changes.
Missing rule. Before the repair, code changes could pass without review.
Restored setting. Changes now need review before entering the protected branch.
Verified condition. A fresh check confirms the rule and attaches its result to the commitment.
SOX compliance tools differ in who carries repairs
Choose SOX compliance software around the work you need: program tests, ITGC evidence or access reviews. ZeroTB handles the daily SOC 2 repair work.
| Task | Internal-controls suites | Compliance-automation platforms with a SOX ITGC module | Access-governance tools | ZeroTB |
|---|---|---|---|---|
| What it runs | SOX program, testing and certification | SOC 2 evidence and SOX ITGC checks | Access reviews for financial systems | Daily SOC 2 access and change checks |
| Who carries the repair | Control owners, tracked in workflows | Your team, from alerts and tasks | Reviewers revoke or confirm access | ZeroTB prepares repairs, your team approves |
| What the tester reads | Test results and sign-offs | Evidence collected per control | Access review records | Signed Verified Control Record per repair |
| Fits when | Large programs need one testing system | SOC 2 holders add SOX ITGC evidence | Finance-system access needs review | 25 to 250 people, repairs nobody owns |
Daily checks add evidence between SOX compliance tests
SOX compliance testing examines how a control was designed and how it operated during the period. PCAOB AS 2201 describes that assessment.
Daily checks add dated passes, failures, response owners and verified repairs between quarterly tests. The wider testing plan still applies.
SOC 2 controls support SOX where scope matches
SOX covers IT general controls (ITGCs) for financial reporting: access, program changes and computer operations. Some access and change controls also support SOC 2.
Financial reporting sets scope. The financial-reporting assessment determines which systems SOX covers
Systems must match. An access review helps only where SOX covers the systems reviewed
Evidence serves each program. Shared controls must meet each program's evidence requirements
ZeroTB checks GitHub, AWS, Okta and Google Workspace
ZeroTB compares GitHub rules, cloud settings, account access and device conditions with the requirements approved for each system.
We check branch rules, required reviews and CI gates against development requirements.
We examine cloud settings for changes from the conditions in approved commitments.
We check leaver access and privileges against approved access requirements.
We check enrollment, encryption and patching against the policy baseline.
Talk to our team
We can discuss the access and change controls you need to maintain, including repairs that involve several teams.
FAQ
Is ZeroTB SOX compliance software?
ZeroTB operates SOC 2, ISO 27001 and HIPAA commitments. Its access and change controls can support SOX where scope and evidence match. ZeroTB does not perform audits.
Which compliance service fits a fintech that already holds SOC 2 Type II?
Fintech teams holding SOC 2 Type II need a service matched to the remaining work: advice, assurance or daily control operation. ZeroTB operates controls, with repair ownership defined.
Can our developers keep using coding agents under the same change controls?
Coding-agent changes follow the repository's development requirements. ZeroTB checks branch rules, required reviews and CI gates, without connecting to the coding agent.
What happens when a system disconnects before a control check?
ZeroTB shows unavailable checks as disconnected, stale or unknown. An earlier pass cannot establish the current state.
What access does ZeroTB need to our systems?
ZeroTB starts read-only. Write access is scoped by action class and revocable. Your team reviews material changes as pull requests. Direct API actions are opt-in and reversible.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments and takes two real gaps through verified restoration, with portable repair records.