Compliance without more headcount
ZeroTB takes on the recurring control work that would otherwise need a dedicated compliance engineering function. Our team and software check systems and prepare repairs, reducing the follow-up between compliance, IT and engineering. Decisions about material changes and exceptions stay with your people.
Works with the stack you already run


Compliance follow-up across teams
A failed control leaves compliance with several people to follow up with. IT or engineering may have made the repair, but the approval and evidence sit elsewhere. Before the next review, someone still has to establish what changed and whether the requirement now holds.
A control fails
Repair details spread across teams
Compliance chases the evidence
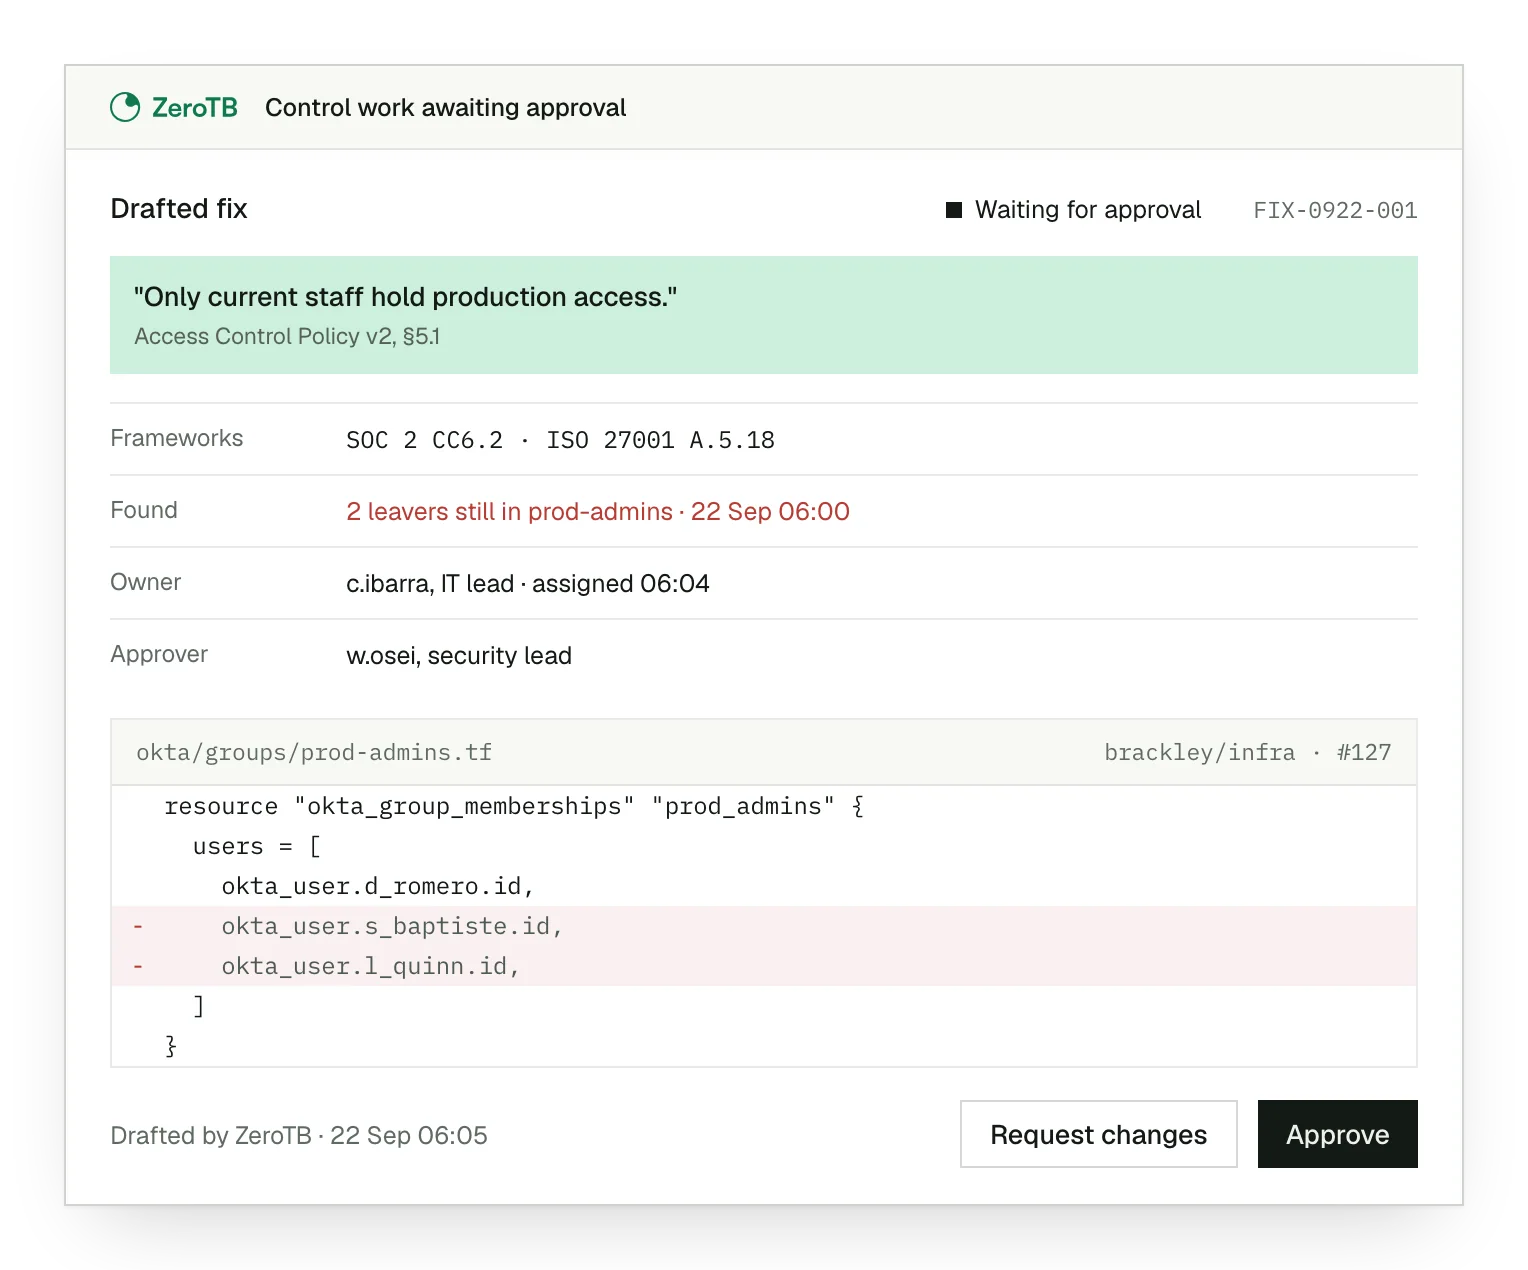
Control work from requirement to evidence
We read the reports and policies, get commitments approved and check them against what the systems do.
We give the gap an owner and prepare the repair. Approved changes run within the permissions granted.
We check that the repair worked before closing it, then save the result with the action and approval.
Example of blocking a personal account while preserving work access
The Verified Control Record lets compliance review a repair without asking each team to reconstruct its part. Here, the repair blocks a personal account from company data. The record shows why that restriction was needed and confirms that approved work access still functions.
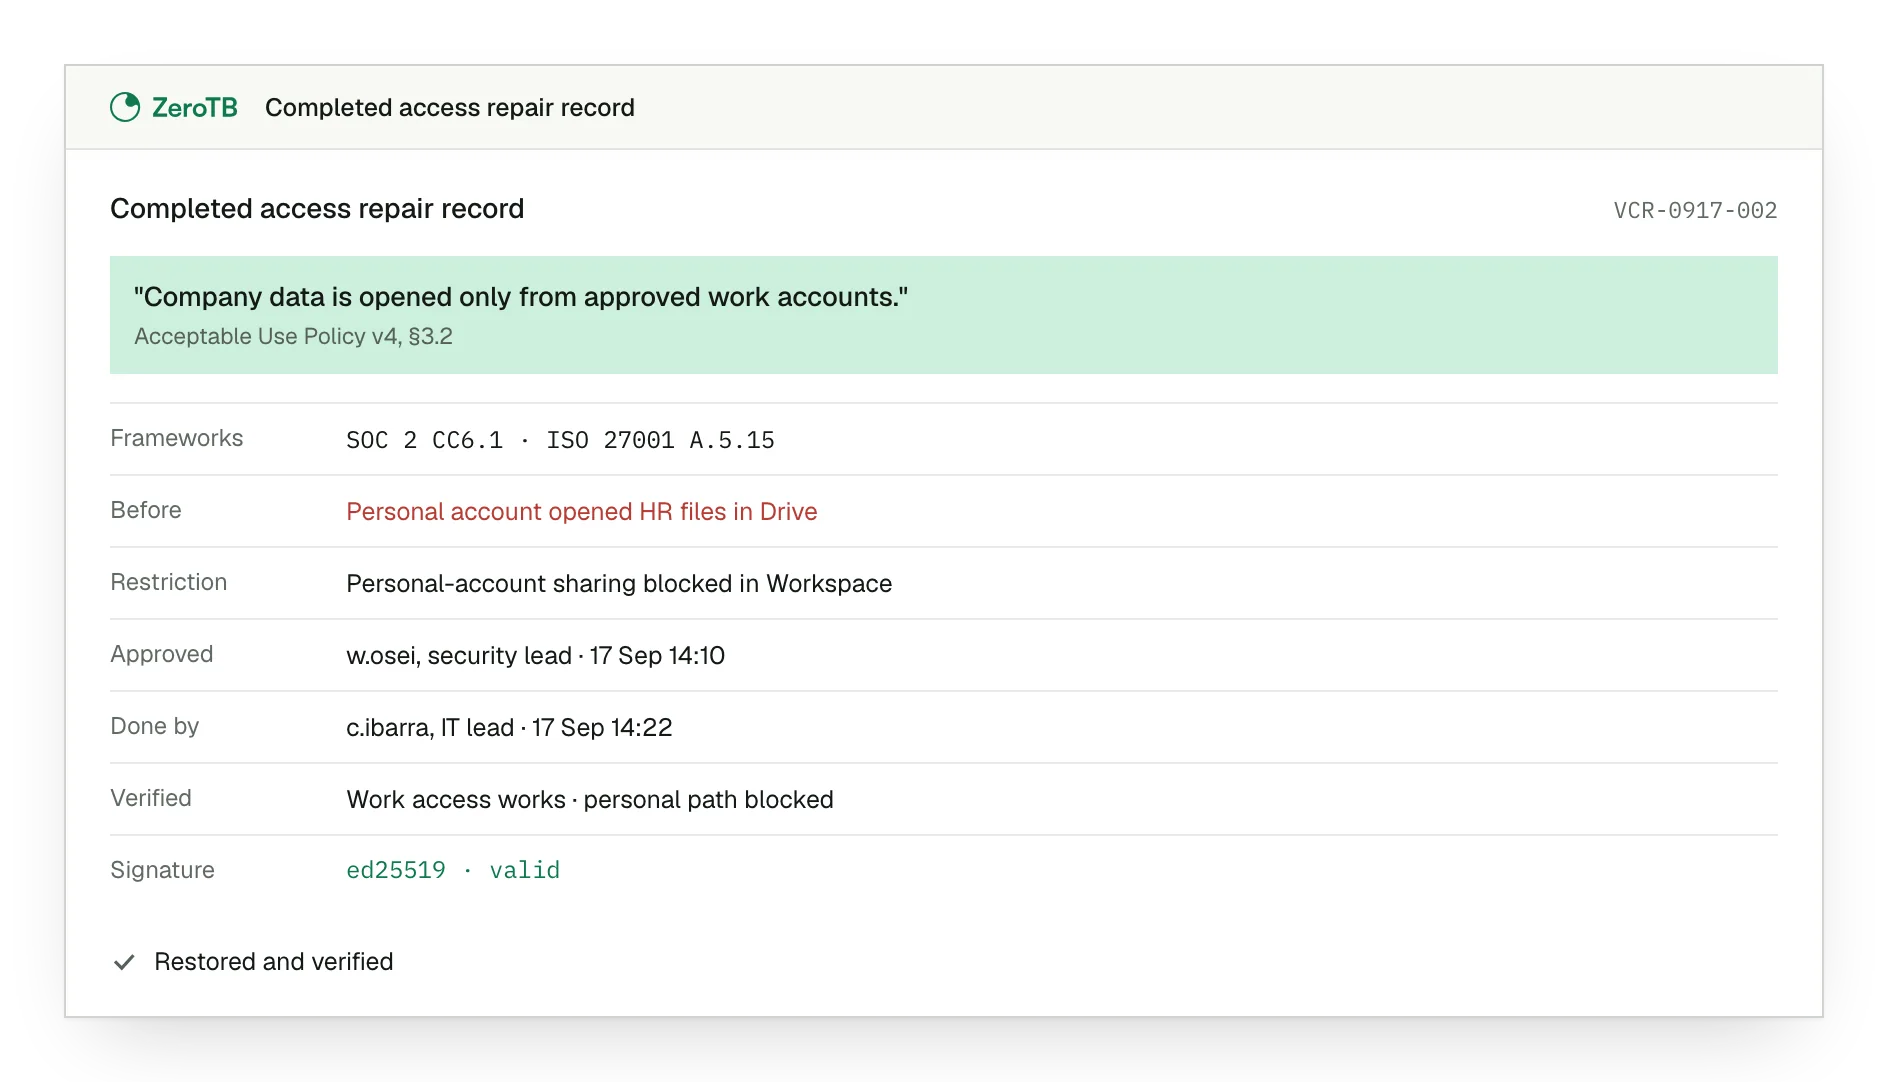
Original gap. A personal account had access to company data despite the requirement for approved work accounts.
Approved action. The restriction appears with its approval, so the reviewer can establish who authorized the change.
Verified result. The check after the repair shows that approved access works and the unauthorized path is blocked.
Support for the existing program
ZeroTB keeps commitments, checks, repairs and evidence together. ZeroTB supplies signed, portable evidence from its control work, so your team can retain a copy for audit review. Auditors can also read those records directly in ZeroTB.
Keep control work and records in ZeroTB
Retain portable evidence for auditor review
Keep people responsible for approvals and exceptions
Talk to our team
Talk with us about the compliance work that takes repeated follow-up and where your team needs help between audits.
FAQ
Is this suitable when compliance is only part of someone's role?
It can be. ZeroTB works with teams that own the requirement and can authorize the fix, including those without a compliance engineering function. The useful question is which recurring control work needs support and who has authority over those systems.
Can the same work support our second compliance framework?
Yes, where the frameworks depend on the same control. ZeroTB works from your commitments under SOC 2, ISO 27001 and HIPAA. Restoring a shared control can satisfy more than one requirement, so the same repair can support several parts of the program.
Does the work extend beyond engineering repositories?
Yes. ZeroTB also checks devices, identity and access, cloud infrastructure, and people and process. For example, it can observe device protections and track whether required access reviews or training have happened. The company’s commitments determine the checks.
Do we need to grant permission to change systems during the initial review?
No. The initial access is read-only. You can later grant and revoke write permissions for particular classes of action. Material changes normally go through pull requests. Any direct API action requires opt-in, a way to reverse it and limits on what it can affect.
Can a system owner carry out a repair manually?
Yes. A runbook that a person executes is one supported response. ZeroTB proposes a response suited to the gap, which can also be a pull request, an approved API action or a preventive guardrail. People keep authority over material actions.
How will we know when ZeroTB lacks current evidence?
ZeroTB displays unknown, stale and disconnected states. Those states make missing observations visible, so the team can see where the system lacks enough evidence to establish that a control is operating.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. It gives your team working controls and portable evidence from an engagement in your own systems.