The SOC 2 Common Criteria cover nine areas: governance, communication, risk assessment, monitoring, control activities, access, operations, change management and risk mitigation. For each area, establish what your service promises, which controls support that promise and who operates them. Include how the team will detect a failure and confirm that a repair worked.
Security requirements often cross team boundaries. Compliance owns the policy, an application owner decides who needs access, and IT removes the accounts. Understanding the Common Criteria helps those teams connect their work, including the decisions and checks that keep an approved policy effective as systems change.
Scope and commitments
SOC 2 security requirements need a defined service and system boundary before a team can choose suitable controls. The Common Criteria span CC1–CC9. Together, they cover the organizational responsibilities and operating practices that support security within that boundary.
Start with the commitments your company makes about the service, then identify the systems and activities each commitment covers. A requirement for approved work accounts, for instance, needs a clear description of the applications and information those accounts can reach.
Governance and communication
CC1 addresses the responsibilities and authority behind the security program. CC2 addresses the information people use and how it reaches them. Together, these areas help explain how a decision made by one team becomes part of another team's daily work.
When an access policy changes, the people maintaining account settings need the revised rule. They also need to know who can answer questions or approve an exception. Record how the change reaches them and how an implementation problem reaches the person responsible for the policy.
Risk assessment
CC3 asks the company to assess risks to its objectives. The assessment gives a reason for the controls it selects. It also helps the team explain why one unresolved gap needs attention before another, given the systems and information at risk.
Reconsider the assessment when the service changes. Moving data into another application, for example, introduces a destination that the previous review may not have covered. Examine who can access it and whether the existing controls extend to that application before relying on the earlier conclusion.
Control activities and monitoring
CC5 concerns the activities selected to address risk. CC4 concerns evaluating their operation and communicating deficiencies. For each control, the team needs to understand what action is required and how someone will establish whether that action had the intended result.
Consider an access review that identifies accounts for removal. Finishing the review leaves a decision for the application owner to implement. The records need to connect that decision with removal and a check of the resulting access, including any account that remains unresolved.
Logical and physical access
CC6 covers protection against unauthorized access to systems, information and physical resources. Account approval, permissions and access removal are part of that work. Physical access also needs attention wherever facilities or equipment fall within the service's defined system boundary.
Access protections depend on the routes people can use. A change to an account, application or device can affect those routes. Check that the approved restriction reaches the relevant systems, and keep the reason for retained access or an exception with its approval.
System operations
CC7 concerns the work of detecting security problems, evaluating events and responding to incidents. An alert begins that work. Someone must investigate the observation, establish which systems it affects and decide what response is needed. Those responsibilities belong in the operating process.
The source of an alert also needs attention. If a connection fails, silence tells the team little about the system it was observing. Check the age and coverage of observations, and leave the control's state unresolved while the information needed to evaluate it is unavailable.
Change management
CC8 concerns authorizing, testing and implementing system changes. A review rule in a development policy depends on the release path enforcing it. Repository permissions and deployment settings therefore matter alongside the record of who approved a particular change and what the tests found.
The same requirement applies when an engineer uses a coding agent. The code still needs the agreed reviews and tests before release. As workflows change, inspect whether a route now permits deployment without those steps, even though the team continues to describe its process as reviewed.
Risk mitigation
CC9 concerns risks from business interruptions and from vendors or business partners. A company's service can depend on systems it does not operate itself. Its assessment needs to account for those dependencies and the effect their failure could have on its commitments.
A vendor review or incident exercise can identify work for several teams. Keep the resulting decisions with an owner responsible for following them through. When a dependency changes, revisit the earlier assessment to see whether the agreed response still fits the way the service works.
Check frequency and coverage
The right check frequency depends on the work being checked. Permissions and configuration can change daily, making daily observations useful. A policy review or incident exercise follows a schedule. Its owner needs to know when the work is due and what constitutes completion.
Use system observations for conditions that can be checked directly. An exception decision needs a person with authority to accept it. Whichever method applies, the reviewer needs to know its coverage and whether the information is current enough to support a conclusion.
Repair responsibility
A failed check needs someone who can carry the issue across the teams required to resolve it. Compliance may own the requirement while IT or engineering controls the affected system. Agree who decides the response and who can authorize the proposed change.
ZeroTB connects that work: it reads approved commitments, checks the systems, drafts a fix, obtains human approval and verifies the result before recording closure. This gives the control owner a checked outcome and the evidence behind it. The Security page explains the access and approval boundaries.
Evidence of operation
A reviewer needs to understand what the company promised and what happened when people carried out the work. Keep the dated observation with the relevant commitment. If it revealed a failure, connect it to the approved response and the result of verification.
A screenshot shows a condition at one time. Later observations help explain whether that condition continued. For a repaired control, the record should make it possible to see why the owner accepted the result, including which change was approved and what the subsequent check found.
Example of restoring deployment reviews
In this example, a production branch accepts changes without the review required by policy. The repository owner approves restoring the review rule. A test then establishes whether the release path enforces that rule, giving the control owner a basis for closing the gap.
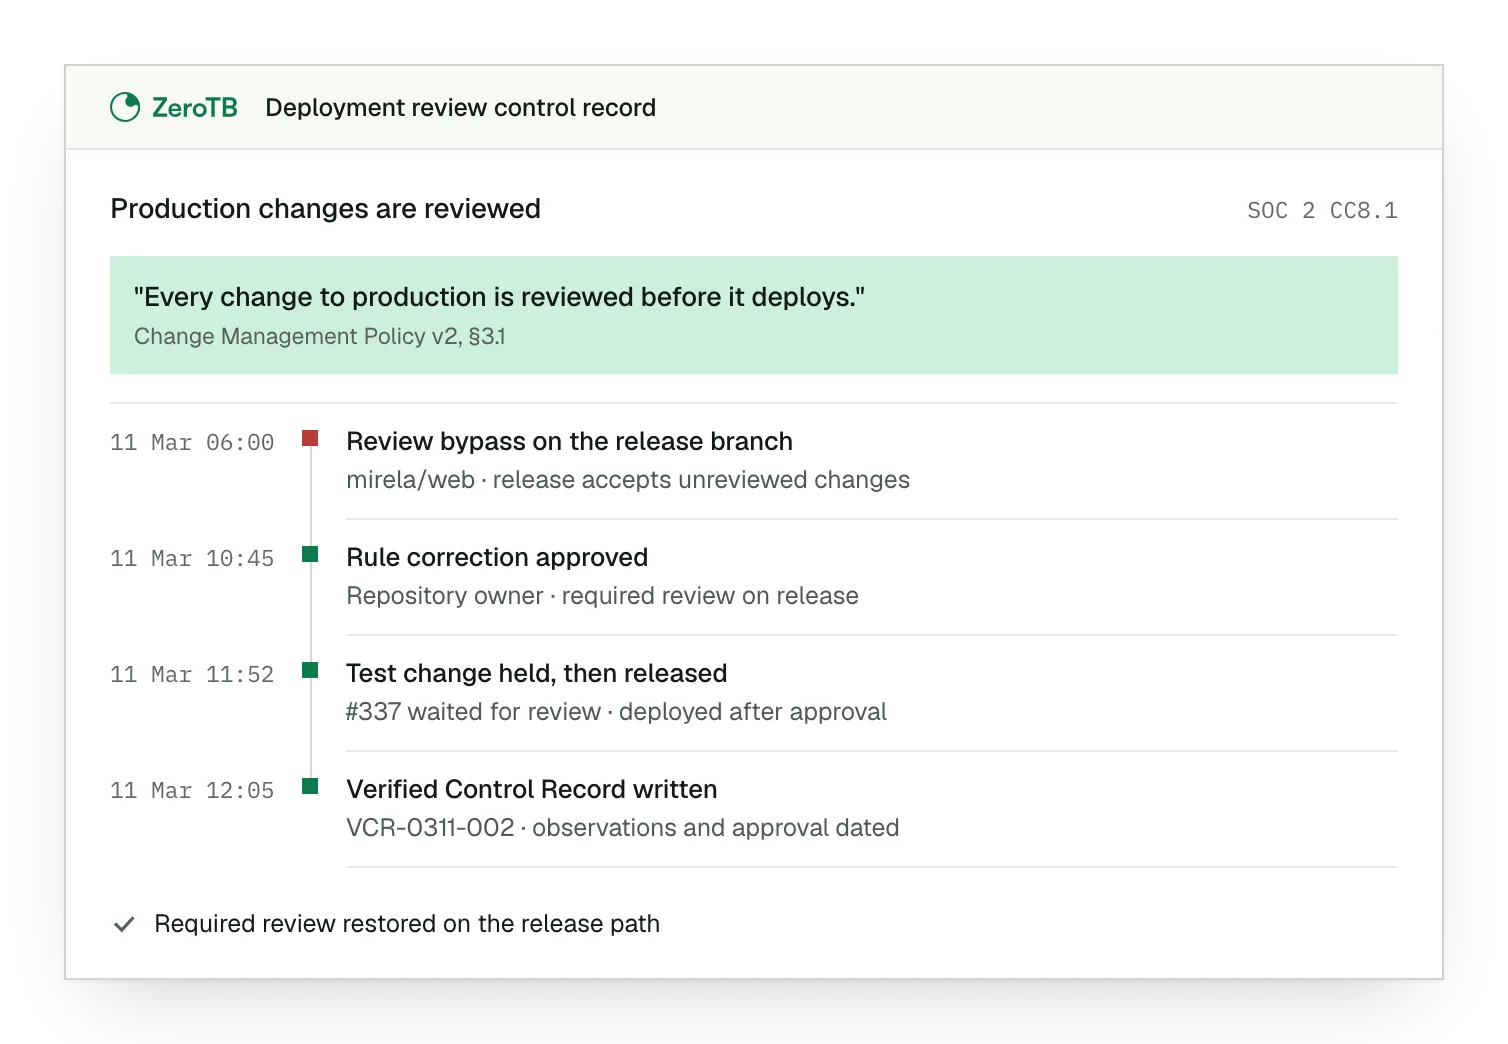
Missing review gate. The branch permits a change to proceed despite the policy requiring a review first.
Approved rule correction. The owner checks the deployment path and approves the proposed correction to its review rule.
Release path tested. The test first waits for review, then proceeds after approval through the intended release path.
Verified result retained. Dated observations and approval remain together in the Verified Control Record for the repaired requirement.
Security control checklist
Select a requirement from the approved policy or report and state the condition that must hold in the affected systems.
Establish who owns the requirement, who can change the system and who approves a response when the control fails.
Compare the systems covered by the commitment with the available observations, including their age and any disconnected sources.
Review the proposed correction with the system owner, including its effect on approved work and any exception that must remain.
Verify the condition after the approved change, then retain the observations and approval with the result and continuing check schedule.
Sources
- AICPA & CIMA, 2017 Trust Services Criteria with revised points of focus, 2022 revision.
- ZeroTB, Control operation and verified restoration, 2026.
- ZeroTB, Recurring SOC 2 findings, 2026.
Start with the Pilot
Talk with our team about the controls you want to keep operating. During the eight-week Pilot, we map up to 25 commitments and take two real control gaps through verified restoration. The work includes records of the approved repairs and results.