vCISO
ZeroTB helps teams keep controls working after the audit, with ongoing support from our team and software. If your vCISO search is driven by unfinished checks and repairs, we can carry that work. Your security lead retains material decisions and gets a record of each completed repair to review.
Works with the stack you already run


Unfinished control work
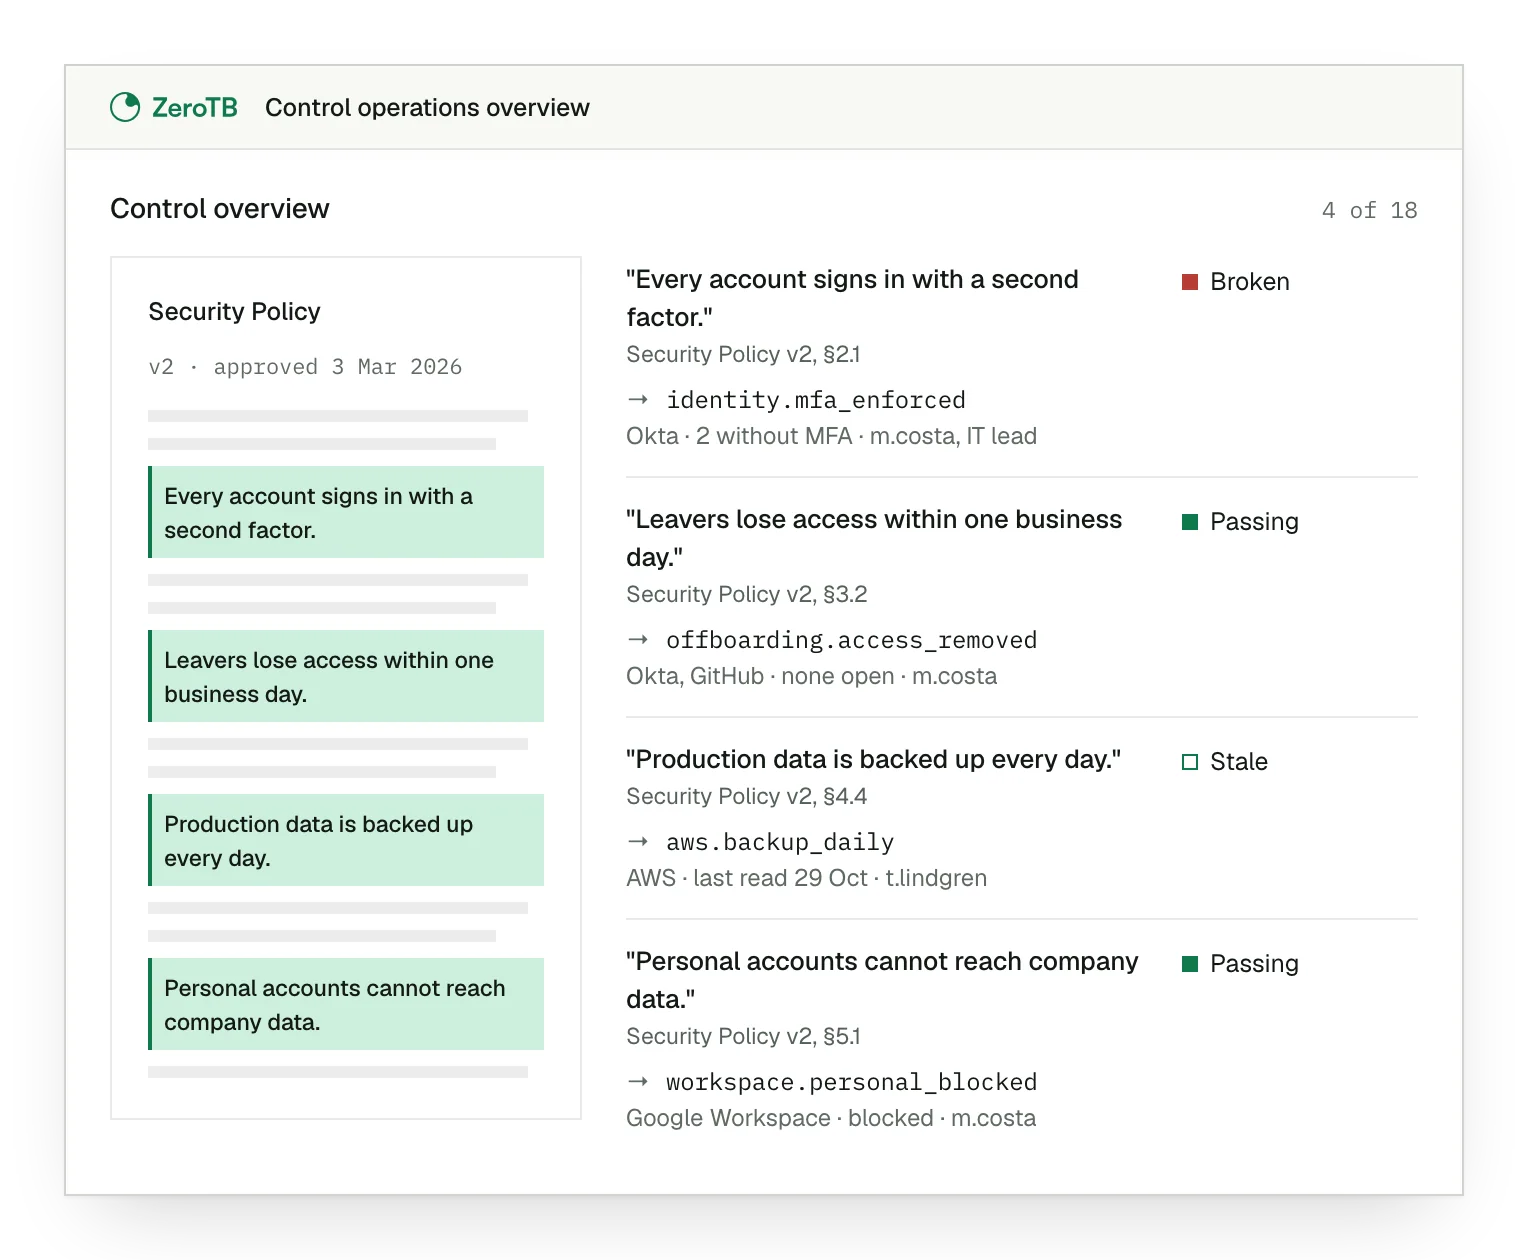
A control still needs attention after someone has written its policy. Accounts change, employees leave and repositories gain new settings. If a repair passes between compliance, IT and engineering, the security lead can be left asking whether anyone checked that it worked.
Systems change after the audit
Repairs pass between teams
Control gaps remain open
Control operations alongside security leadership
ZeroTB fits teams that already have security leadership and need help operating their controls. Some vCISO engagements include implementation as well as leadership. The scope of that engagement determines whether ZeroTB would take on the control work or work alongside the vCISO.
Security leadership sets priorities and directs the program
ZeroTB carries ongoing checks and approved repairs
People retain decisions about risk and exceptions
Control work from start to finish
ZeroTB reads the commitments in your reports and policies, gets your approval and checks the systems they apply to.
ZeroTB proposes how to repair the gap through a runbook, pull request, API action or guardrail. People authorize material changes.
ZeroTB rechecks the control after repair, then records the commitment, states, action, approval and verification in a signed record.
Example of blocking personal accounts while preserving work access
The Verified Control Record lets a security lead inspect the outcome of an access repair. In this example, a personal account has access to company information. The repair blocks that path, and a check establishes whether approved work access was preserved.
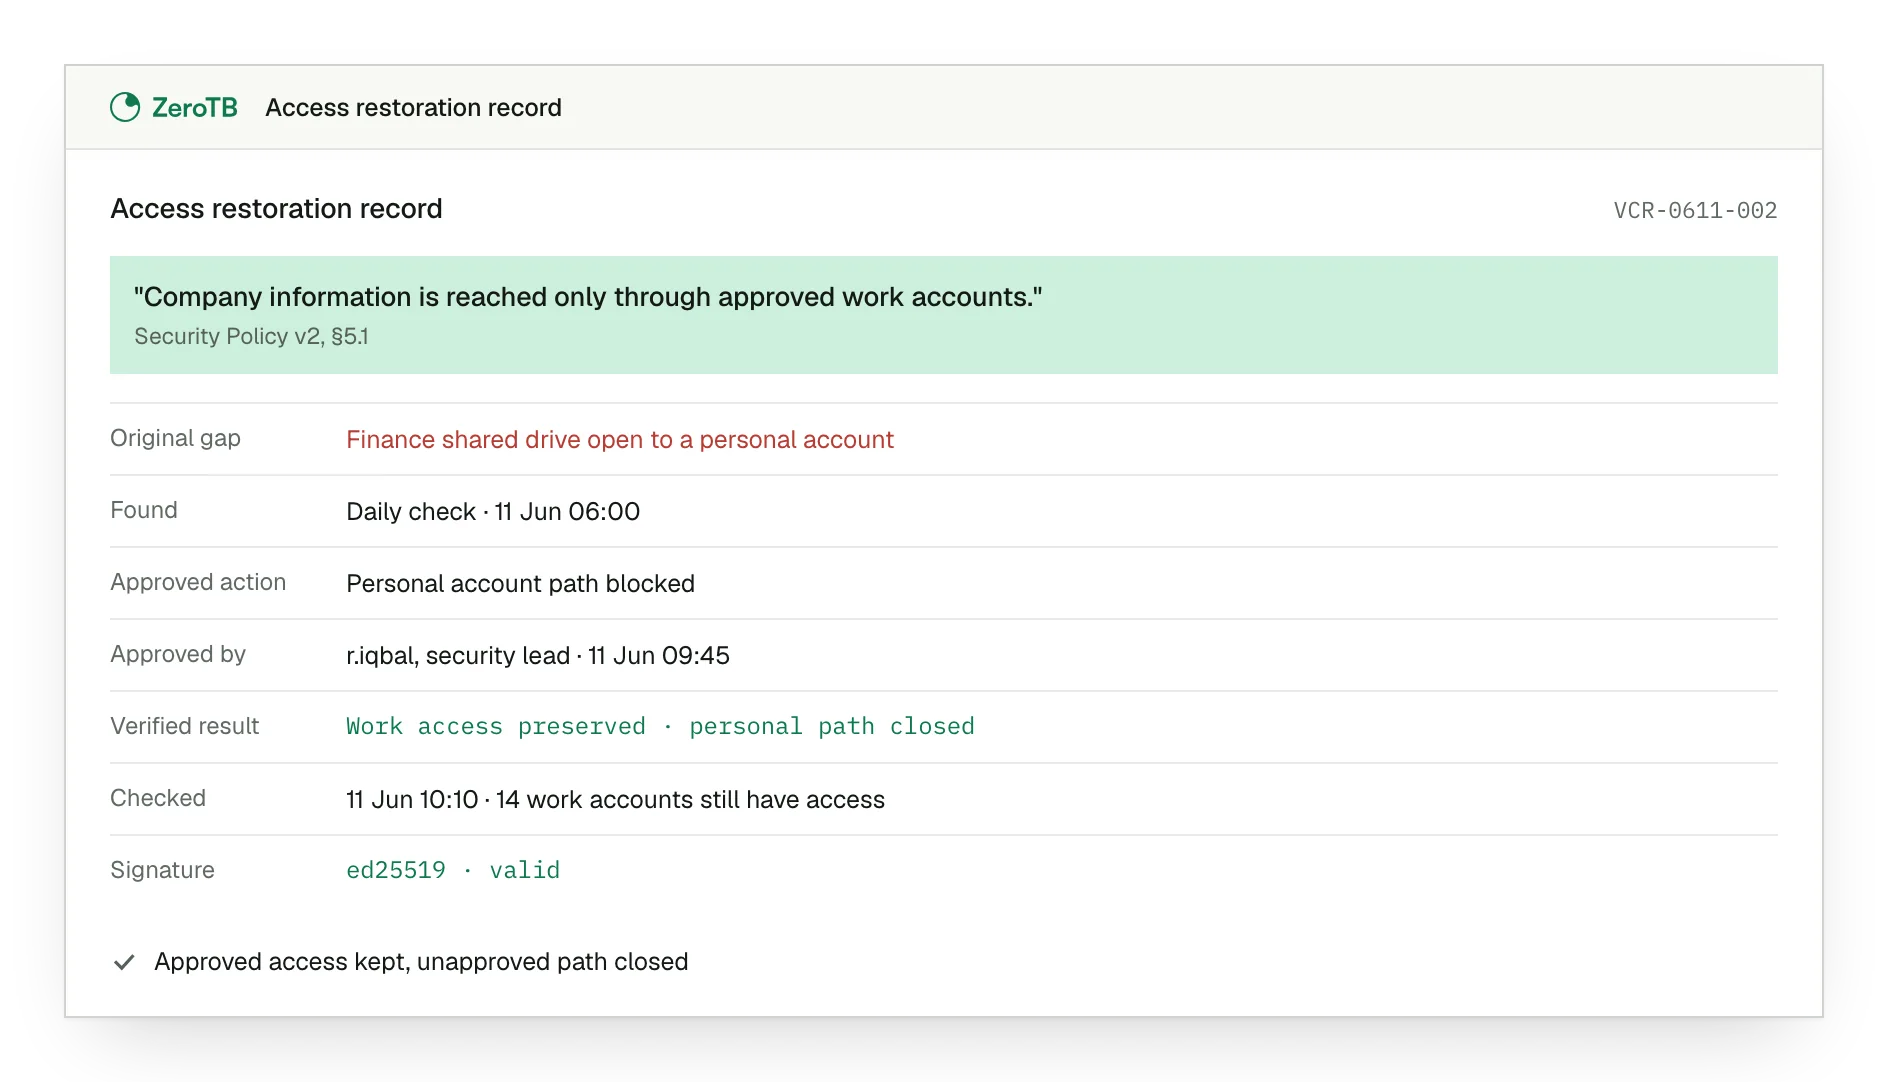
Original gap. Company information is accessible through a personal account, contrary to the approved work-account requirement.
Approved action. The blocked access path appears beside the approval that permitted ZeroTB to make the change.
Verified result. The observed result shows approved work access preserved and the personal account path closed.
Capacity between audits
ZeroTB can carry recurring control work when a company cannot justify its own compliance engineering function. Hiring someone full-time may cover a broader set of duties. Our service suits the part of that need concerned with keeping controls operating and retaining evidence of completed repairs.
Control operations covers continuing checks and repairs
Existing security leadership retains program decisions
Verified Control Record shows what each completed repair achieved
Talk to our team
Talk with our team about the control work you need covered and how it fits with your security leadership.
FAQ
Can our vCISO work with ZeroTB?
Yes. The vCISO can direct the program while ZeroTB handles control operations. For each completed repair, the vCISO can inspect what changed, who authorized it and what the check found. People retain the decisions about material actions and legitimate exceptions.
Where would we keep the records of control work?
Your control records stay in ZeroTB. It holds the record of commitments, checks, repairs and evidence for the controls we operate. The evidence from a repair is portable. An auditor can also open the Verified Control Record in ZeroTB to inspect the completed work.
Can this cover both our SOC 2 and ISO 27001 work?
Yes. ZeroTB works with commitments from SOC 2, ISO 27001 and HIPAA. Those requirements can sometimes depend on the same control. When that is the case, one restoration can support several requirements; the approved commitments in your reports and policies determine which ones apply.
Does the service cover controls outside cloud infrastructure?
Yes. ZeroTB also works with endpoints, identity and access, development, and people and process. The work can involve a device baseline, a repository rule or a scheduled review. The commitment your company made determines which check applies.
What system access would we authorize?
ZeroTB begins with read-only access. If write access is needed, it is scoped to an action class and remains revocable. Material changes normally go through pull requests. Direct API actions require opt-in, a way to reverse the change and limits on what it can affect.
Who decides whether an exception is acceptable?
Your people decide. AI can help interpret the policy, investigate what happened and propose a response, but accepting a legitimate exception remains a human decision. The same authority applies when confirming a commitment and authorizing a material action.
How would we know if an observation was missing?
ZeroTB displays unknown, stale and disconnected states when observations are missing or no longer current. A security lead can see that the control needs a fresh observation. Until a check establishes the result, there is no basis to call it healthy.
Is there ongoing support after the Pilot?
Yes. The continuing service is Control operations. The Pilot covers an initial set of real control gaps, and ongoing operations carries the checks and repairs between audits. That work continues as accounts, devices, infrastructure and processes change.
Start with the Pilot
In the eight-week Pilot, ZeroTB maps up to 25 commitments from your report and takes two real control gaps through verified restoration. The work gives you operating controls and portable evidence from repairs in your own systems.