SOC 2 compliance services
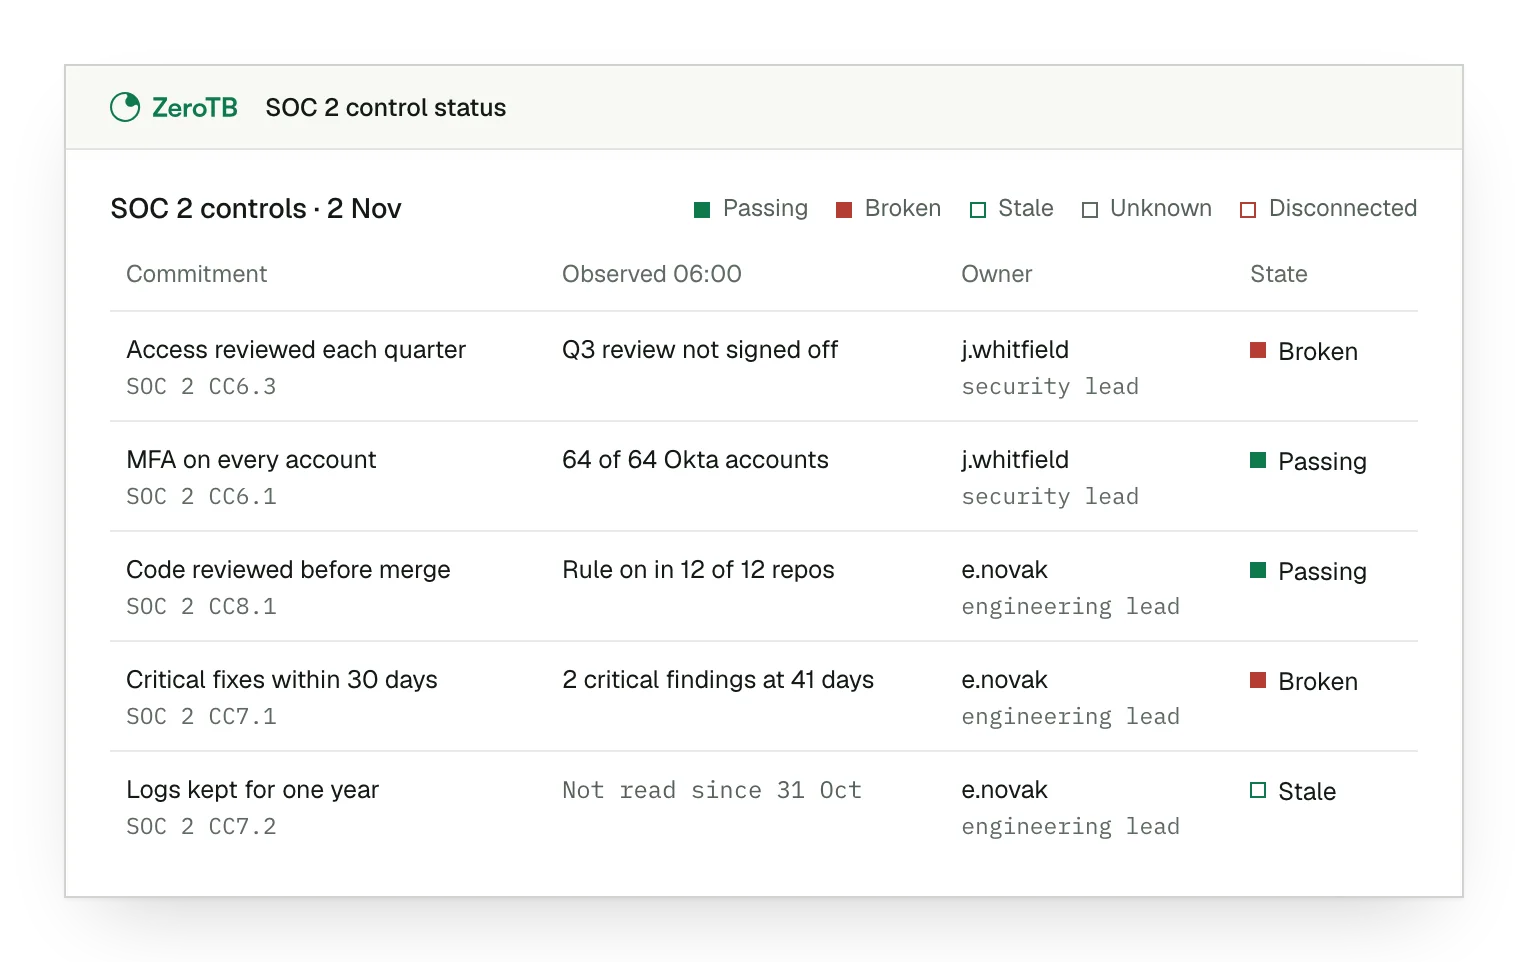
ZeroTB maintains SOC 2 controls after the audit, reducing the work your compliance team has to coordinate with engineers. As accounts, devices and infrastructure change, we handle checks and repairs against your commitments. Your people approve material changes and get evidence showing the result.
Works with the stack you already run


Control gaps between audits
A control that worked during the audit can fail after a system changes. An account survives a contractor’s departure, or a repository permits changes without review. Compliance then needs someone to investigate, arrange the repair and establish whether it worked before the finding returns.
Systems change after the audit
Required protections stop working
Findings return at audit time
Our control operations process
Reports and policies supply the commitments. We identify them for your approval and check the systems they cover.
ZeroTB investigates a gap and drafts its fix. We execute authorized actions within the permissions granted by your people.
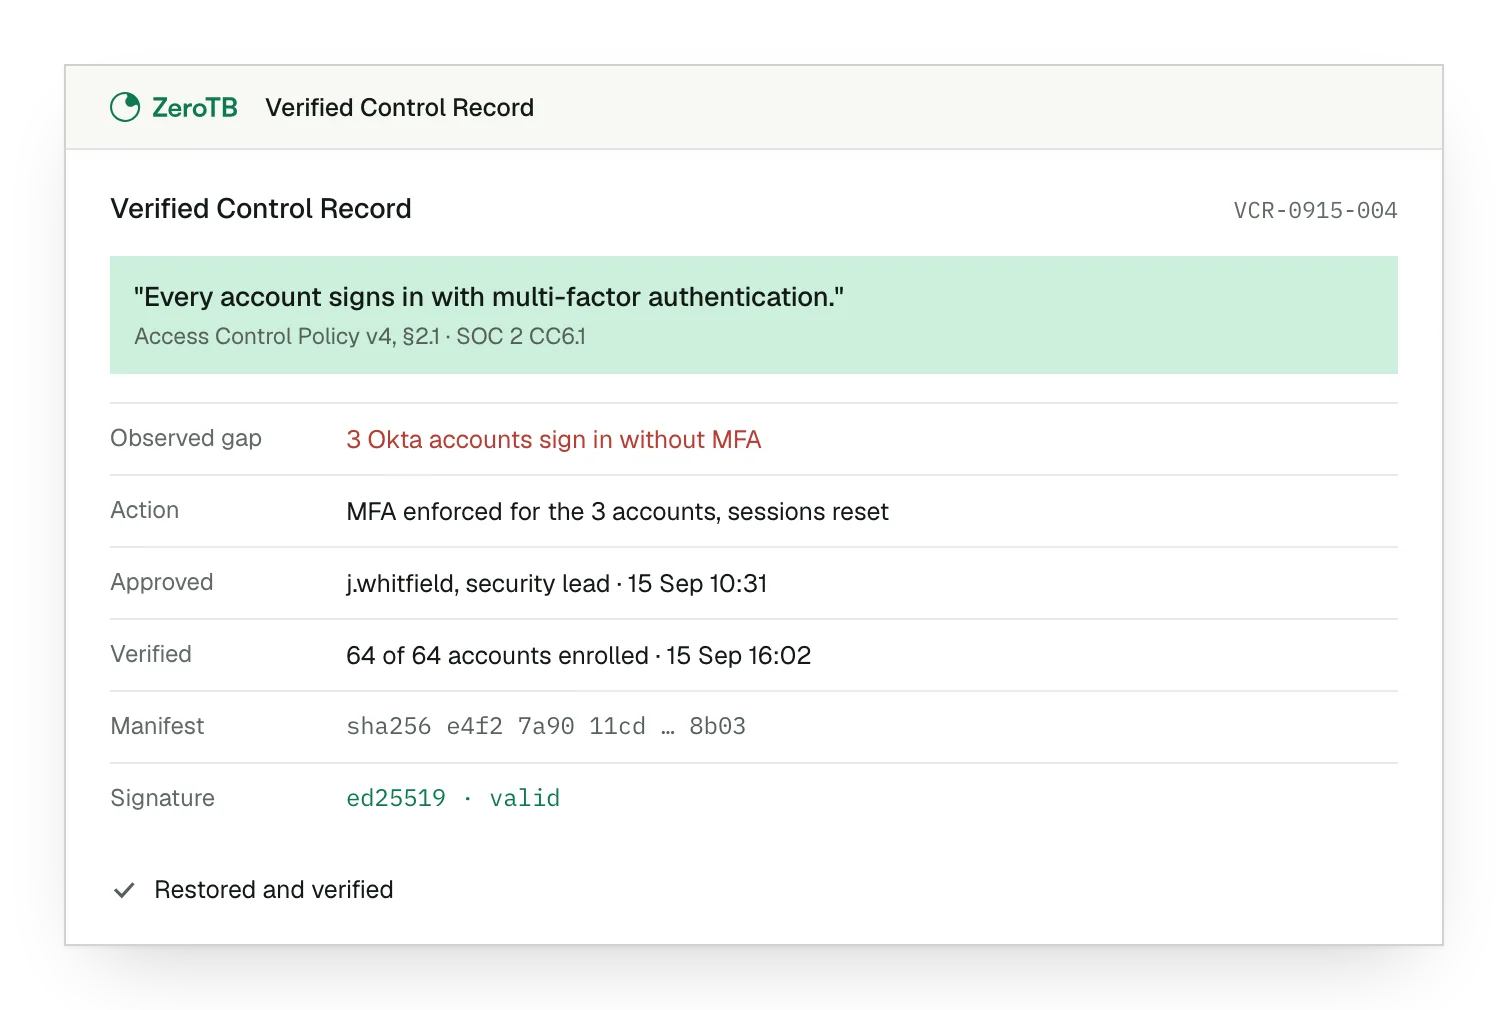
A fresh check establishes the result before we close the work. The record keeps that evidence and the approval.
Records for audit review
Each Verified Control Record gives compliance a signed, portable account of a completed repair. It connects the commitment to the before-and-after state, action, approval and verification. Auditors can inspect the record directly in ZeroTB, and your team can keep a copy.
Support for compliance and engineering
ZeroTB supports teams that need controls to work but cannot justify a dedicated compliance engineering function. Our team has run security and IT in healthtech and taken companies through SOC 2 and ISO 27001. That experience helps us connect requirements with repairs.
ZeroTB keeps commitments, checks and repair evidence together
ZeroTB assigns control gaps to responsible owners
People decide which exceptions are legitimate
Talk to our team
Talk to us about the SOC 2 findings that keep returning and the control work your engineers are handling.
FAQ
Is ZeroTB a fit if we need a provider for our SOC 2 audit?
Our service covers control operations after the audit. You engage an independent auditor to review evidence and issue the report. We maintain the controls that must keep working as people, permissions and systems change.
Which parts of our systems can the service cover?
The service covers five areas: endpoints, identity and access, change and development, cloud infrastructure, and people and processes. Your commitments determine the checks. These can include managed-device requirements, access and code reviews, and scheduled policy reviews.
Can ZeroTB help when the same SOC 2 finding keeps returning?
Yes. ZeroTB investigates the requirement and the system condition behind a recurring finding. It can propose a preventive guardrail, such as a required review rule, when that addresses the cause. Later checks establish whether the control continues to operate.
What permissions would we grant for ongoing work?
ZeroTB starts with read-only access. Write permissions are scoped by action class and remain revocable. Material changes use pull requests by default; direct API actions require opt-in, must be reversible and stay within the agreed limits on affected systems.
How does the service handle an intentional exception to a policy?
Your people decide which exceptions are legitimate. AI can interpret a requirement and investigate a gap, but your team retains authority over the decision. That separates the proposed response from the approval to act.
What happens if a connected system stops supplying evidence?
ZeroTB shows unknown, stale and disconnected states when observations are missing. Those states identify where it cannot establish that a control is working. AI cannot declare the control healthy or close the work on its own.
Can this work also support our ISO 27001 or HIPAA commitments?
Yes. We work with commitments from all three frameworks. Some requirements depend on the same underlying control, so restoring that control can satisfy several requirements. The approved commitments determine which checks apply.
How can we continue the work after the Pilot?
You can discuss Control operations, our service for ongoing checks and repairs. The Pilot gives you working controls and portable records to assess. That lets the conversation about continuing support start with work completed in your systems.
Start with the Pilot
The Pilot gives your team eight weeks to assess ZeroTB on real control work. We map up to 25 commitments from your report and take two real control gaps through verified restoration, with portable evidence of the repairs.