HIPAA compliance consultant
ZeroTB takes on the daily work of maintaining controls behind your healthtech company's HIPAA commitments. Our team handles checks and repairs that would otherwise need coordination between compliance, IT and engineering. You can see which controls have been restored and use the repair evidence in later reviews.
Works with the stack you already run


Controls that change between reviews
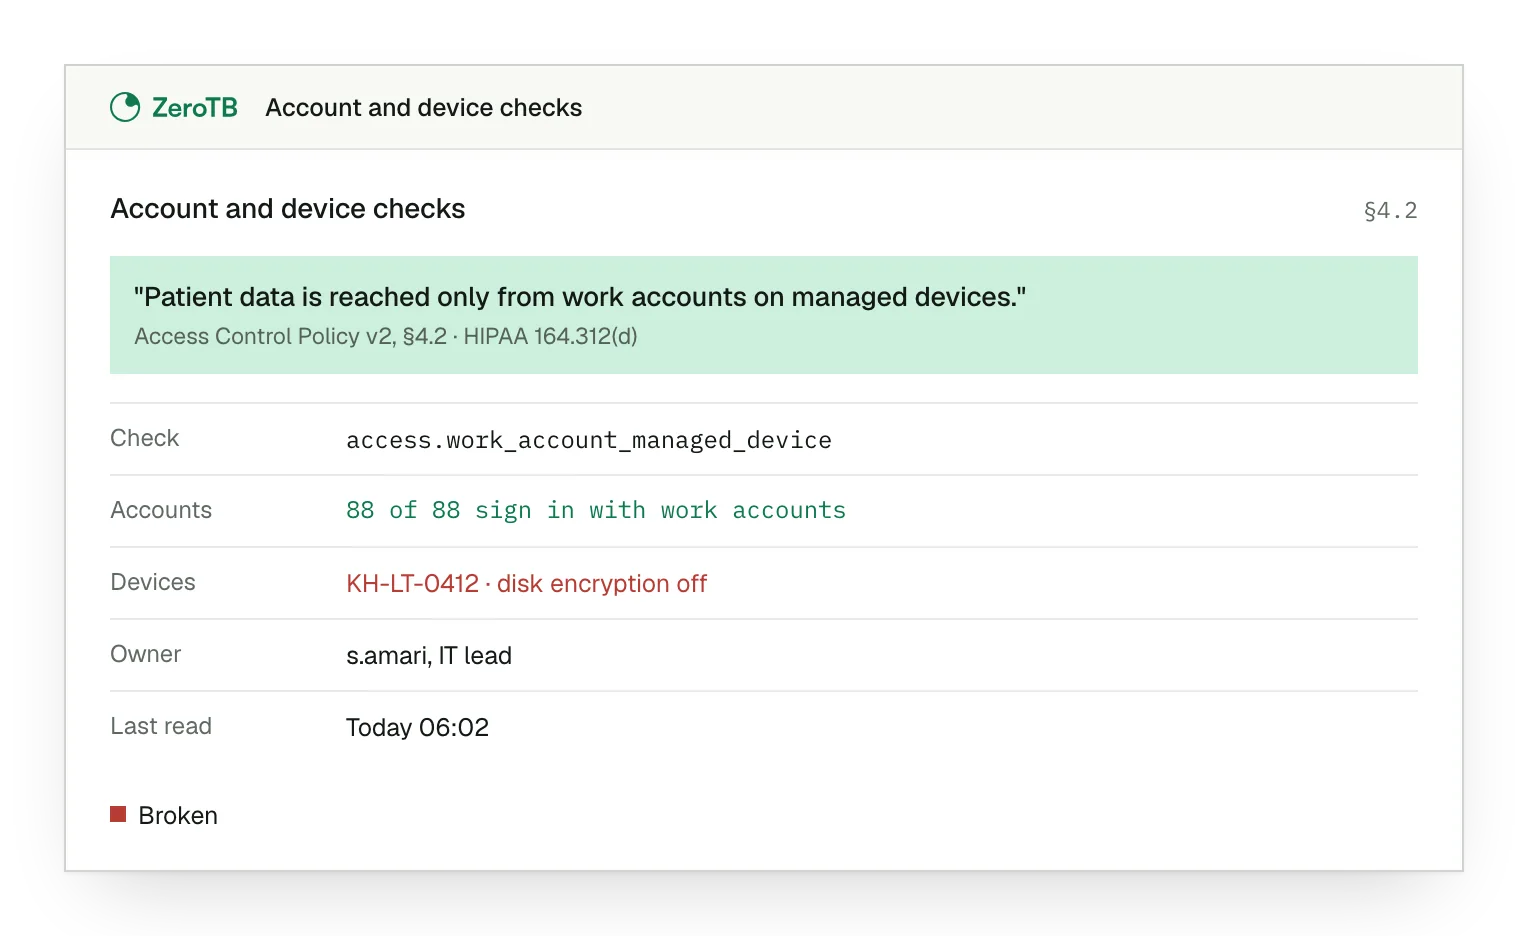
Changes to accounts and devices can leave a healthtech company outside its own access policy. A former employee may still have access, for example, while a laptop no longer meets its required baseline. The last review's evidence describes an earlier state of those systems.
Accounts and devices change
Previous evidence becomes outdated
Access breaks the policy
Healthtech operating experience
Our team has operated security and IT in a US healthtech company, with responsibility for the systems behind the requirements. We have also taken companies through SOC 2 and ISO 27001. That experience informs the control work we handle for customers every day.
Security and IT experience in healthtech
Control work across IT and engineering
Continuing responsibility for control repairs
Daily control operations
We extract commitments from reports and policies. Once approved, they become checks against the relevant systems.
We propose a repair for each gap, then perform or coordinate the work with approval for material changes.
We check the result before closing the work. The signed Verified Control Record retains the repair, approval and verification.
Example of blocking personal account access
This example shows a repair covering both the account and the device used for work. The policy requires approved accounts on managed devices. The record shows that the personal account path has been blocked, the device protections restored and approved work access preserved.
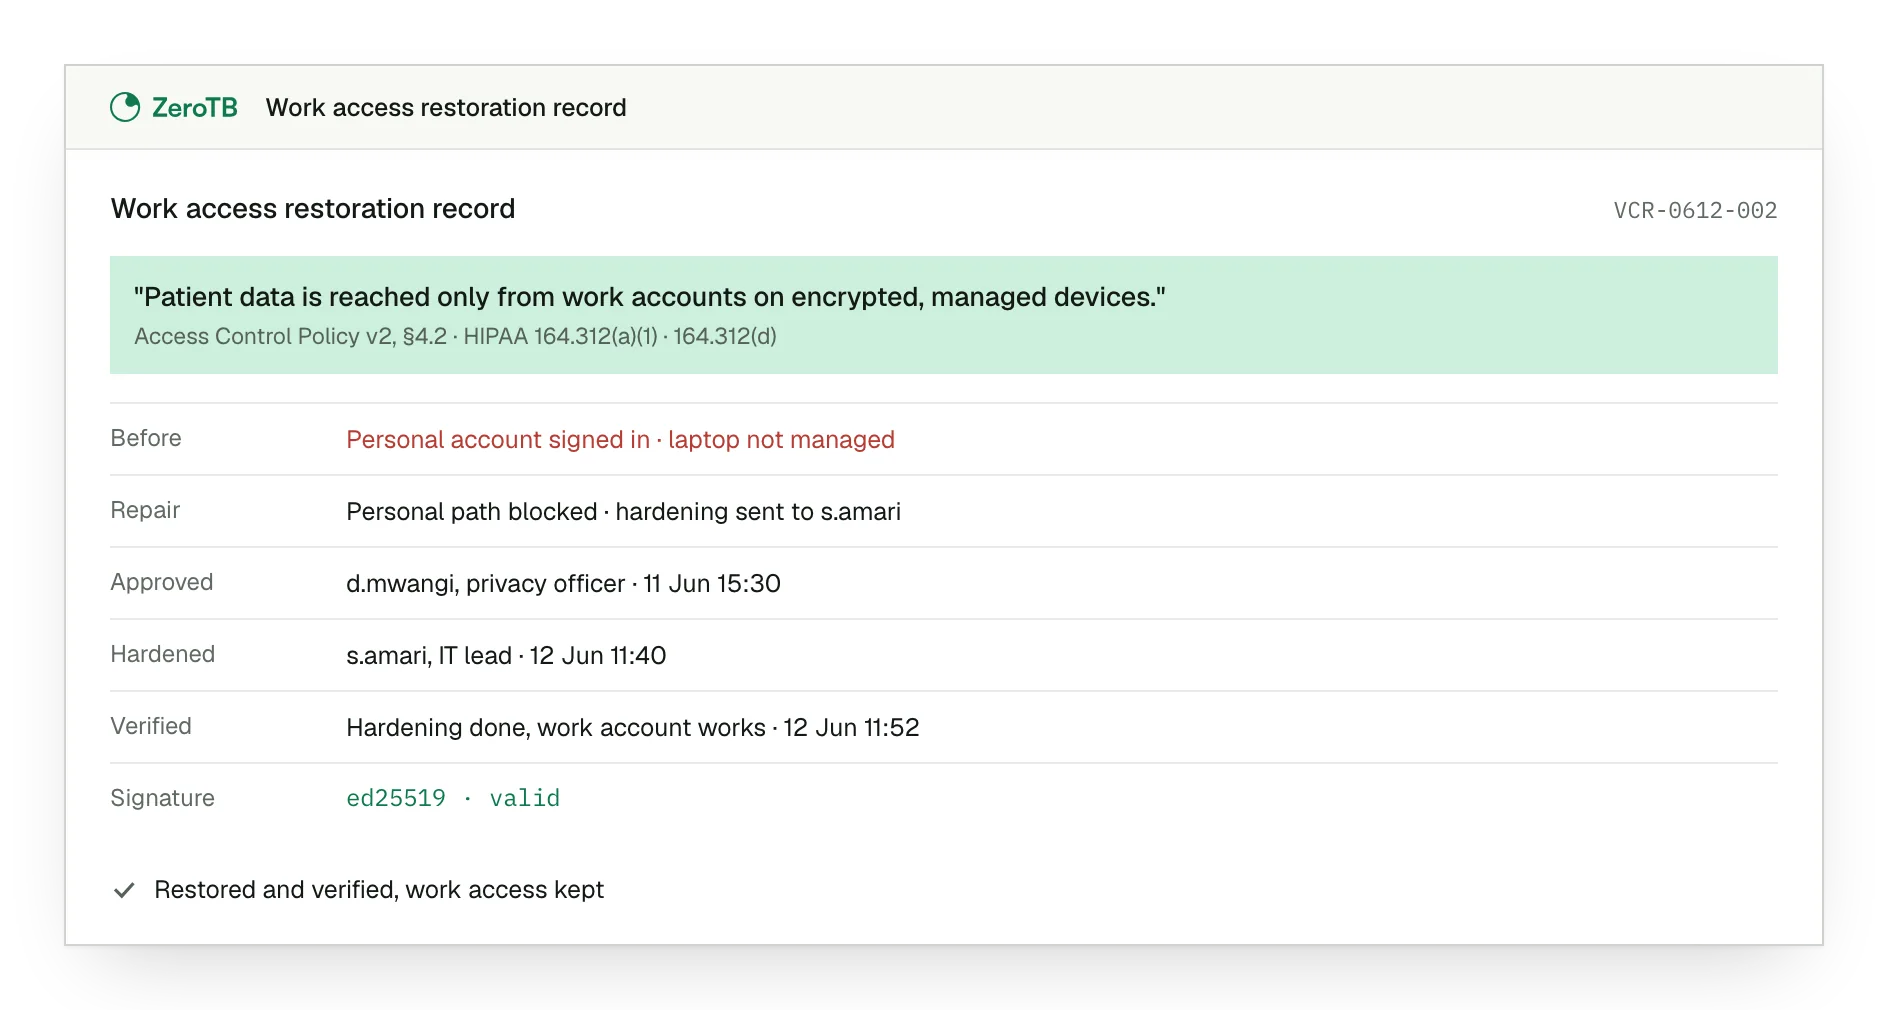
Required conditions. The account and device must both meet the policy's conditions for access to company information.
Completed repair. The approved action restricts the personal account path and assigns device hardening to its owner.
Verified access. The result confirms that hardening is complete and the approved work account remains available.
Shared controls across frameworks
Control work can serve several frameworks at once. Where HIPAA, SOC 2 and ISO 27001 commitments depend on the same control, restoring it can satisfy requirements in each. ZeroTB handles that work and keeps the shared commitments, checks and repair evidence together.
Shared controls support several framework requirements
Repairs remain tied to company commitments
ZeroTB keeps the compliance record
Talk to our team
We can talk through the HIPAA control work your team is handling and where account or device problems keep recurring.
FAQ
Who decides whether a change to our healthtech systems can go ahead?
People in your company make that decision. They approve material actions and decide which exceptions are legitimate. AI reads the requirement, investigates the gap and proposes a response. ZeroTB then works within the granted permissions; AI cannot close the control on its own.
Can ZeroTB inspect our account and device controls with read-only access?
Yes. Read-only access is the starting point. If the work later requires write access, your team grants that permission for a specific class of action. Each permission has a defined scope, and you can revoke it.
How are direct changes controlled when a pull request is unsuitable?
Your team must opt in to direct API actions, with a policy that limits their scope. Those actions must also be reversible. Depending on the gap, a runbook executed by a person may be the safest suitable way to complete the repair.
What happens if an account or device check has no current observation?
ZeroTB keeps the missing observation visible as unknown, stale or disconnected. A control with no current observation cannot be treated as healthy. These states let compliance distinguish a verified result from a check that still lacks evidence.
Can we retain a signed copy of the repair evidence?
Yes. The Verified Control Record is signed and portable. It keeps the requirement, the state before and after the repair, the action taken, its approval and the verification together. You can retain a copy, and the auditor can inspect the record in ZeroTB.
Does the work include commitments that depend on people completing a task?
Yes. ZeroTB schedules training, vendor reviews, incident exercises and policy reviews according to the relevant commitments. Each task goes to an owner, with escalation if it is late. ZeroTB also verifies completion, so compliance can see whether the required work was done.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. Our team works with yours to leave those controls operating, with portable evidence of the completed repairs.