Guardrails for AI agents
ZeroTB helps you keep compliance controls working as AI agents change code, configuration and access. Our team handles the investigation and prepares repairs within defined permissions. You retain approval over material changes and can inspect the evidence that a repaired control works.
Works with the stack you already run


Unchecked changes to working controls
An agent can complete its task while leaving a compliance control unable to meet the requirement your company approved. A change to repository rules, cloud settings or permissions can remove a protection that was working at the last check.
Agent changes a system
Required protection stops working
Compliance commitment goes unmet
Limits on automated changes
ZeroTB starts with read-only access, so investigating a control gap does not require permission to change the system. Write permissions apply to specific action classes. Material changes normally arrive as pull requests for your team to review and merge.
Observation starts without permission to make changes
Write access stays scoped and revocable
Approved logic follows the same rules each time
How control repairs run
ZeroTB reads policies and reports, then checks systems against the commitments your team approves.
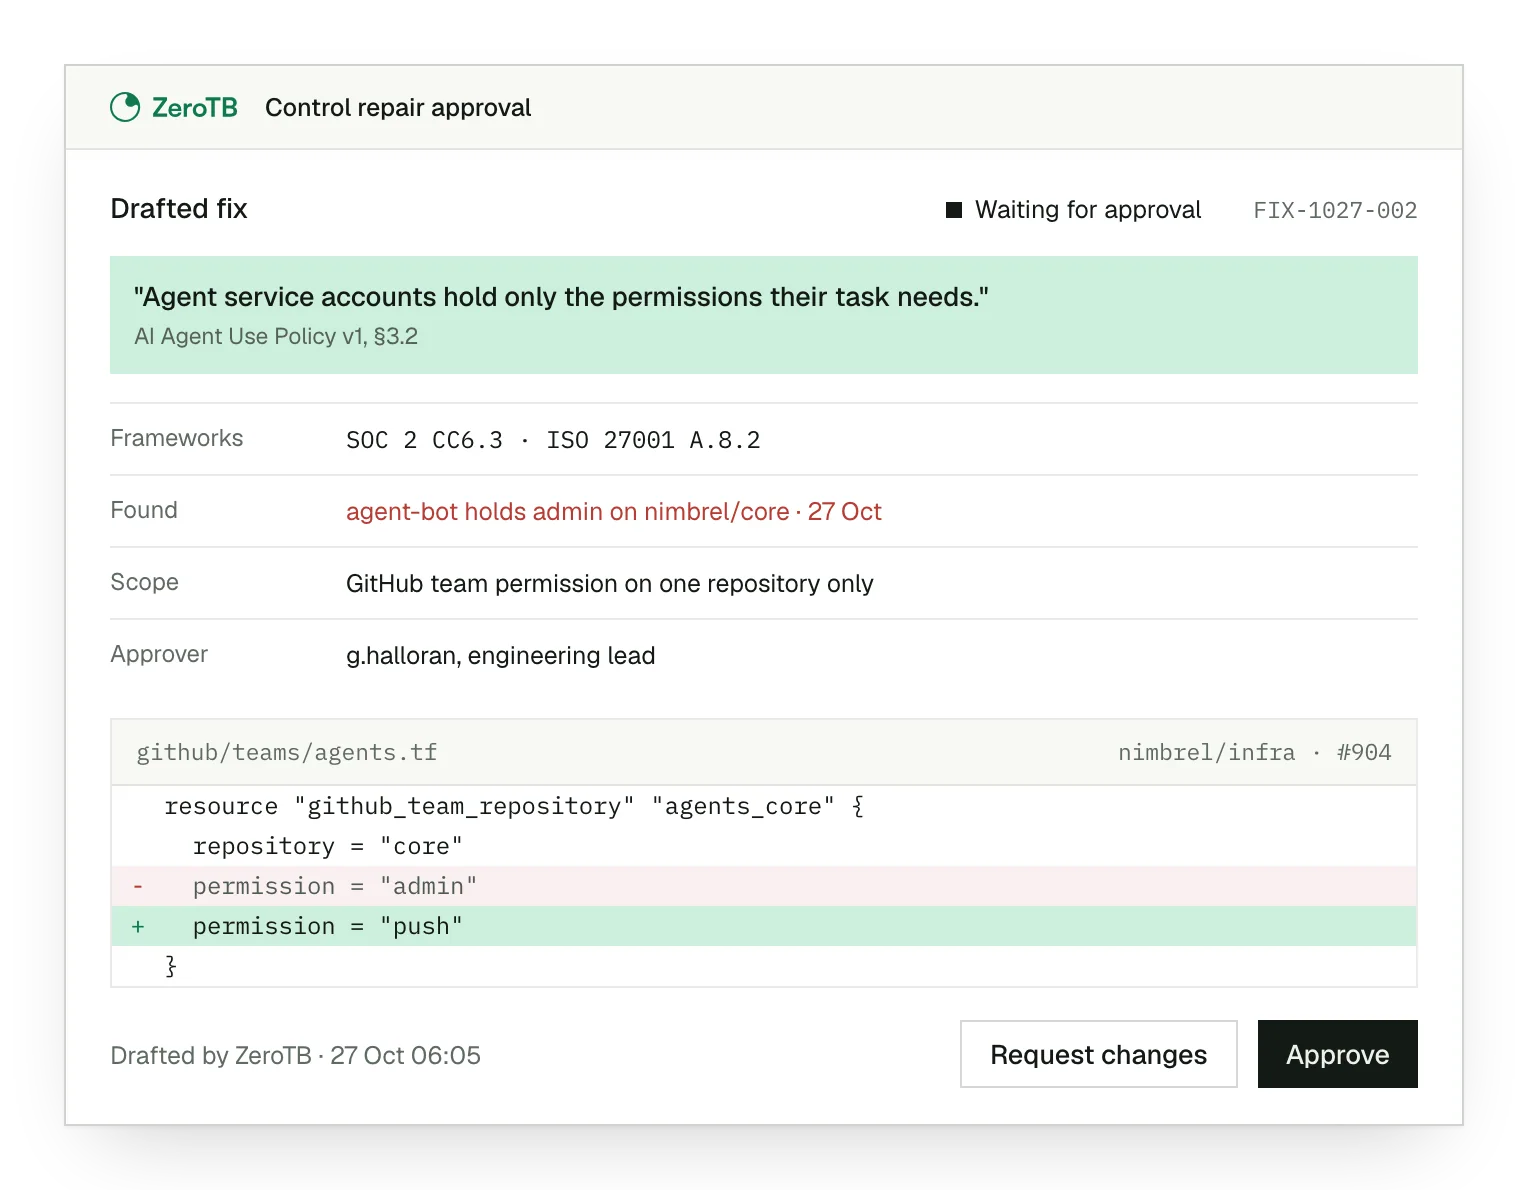
ZeroTB diagnoses the gap and drafts a suitable fix. People authorize material changes before execution.
ZeroTB verifies the result and creates a signed Verified Control Record with the action, approval and before-and-after evidence.
Decisions before execution
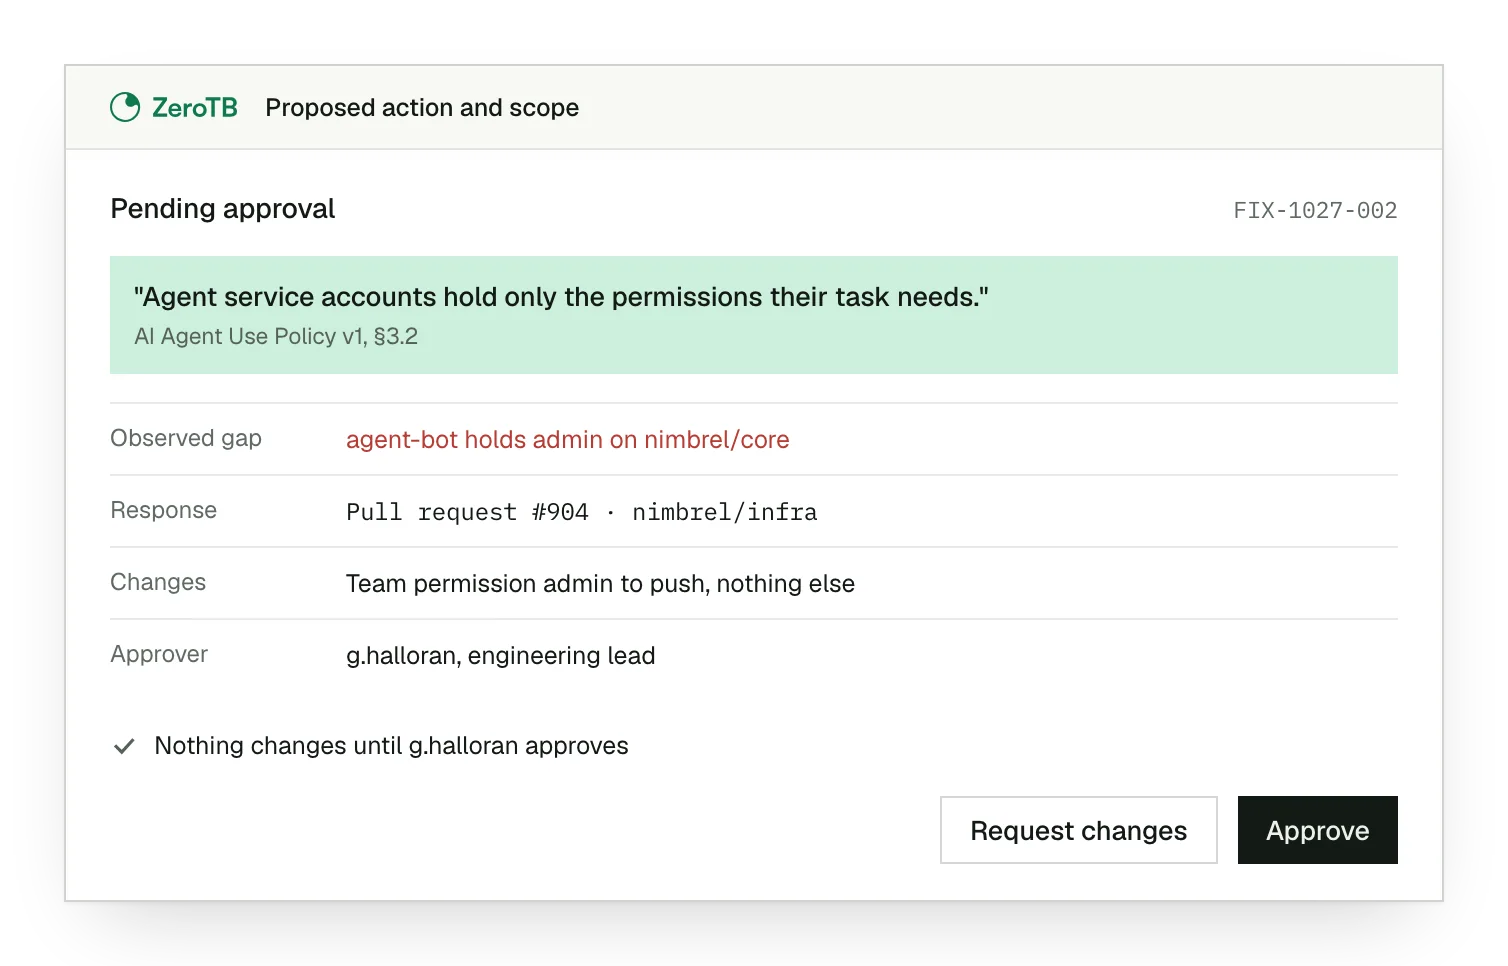
A reviewer can see the requirement, the observed gap and the proposed response before authorizing a material change. ZeroTB explains the finding so the reviewer can assess whether a pull request, runbook or approved API action fits the affected system.
Talk to our team
Talk with our team about where agents act, which changes need approval and how control failures reach the right people.
FAQ
Can ZeroTB make a change without a pull request?
Yes. Your team can opt into direct API actions for a particular class of work. Each action must have a way to reverse it. A policy also limits how much of the system the action can affect.
Can we withdraw permission for automated repairs?
Yes. Your team can revoke write permissions. Because these permissions apply by action class, granting access for one kind of repair gives ZeroTB authority within that scope.
What happens when ZeroTB cannot observe the result?
The finding stays open until ZeroTB can verify the result. Unknown, stale and disconnected observations remain visible. An AI conclusion alone cannot establish that the control works or close the finding.
Who decides when a legitimate exception applies?
Your team owns legitimate exceptions. ZeroTB uses AI to interpret requirements and investigate gaps, but people decide what a commitment means and when an exception is acceptable.
Can this work cover changes outside repositories?
Yes. ZeroTB covers endpoints, identity and access, development, cloud infrastructure, and people and process. The checks follow the requirement. For example, a device commitment may call for a baseline check, while a process commitment may require a scheduled review.
Where does ZeroTB record the controls it operates?
ZeroTB records the controls and keeps their commitments, checks and repair evidence together. ZeroTB operates them and produces portable evidence from repairs. You can retain a portable copy of that evidence for audit review.
Related pages
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. Talk with us about the controls you need to maintain and where the Pilot could help.