GRC engineering
ZeroTB gives compliance and engineering teams support to keep controls working after the audit. GRC engineering means applying technical work to governance, risk and compliance requirements. We provide the software and delivery to do that work, for companies that cannot justify a separate compliance engineering team.
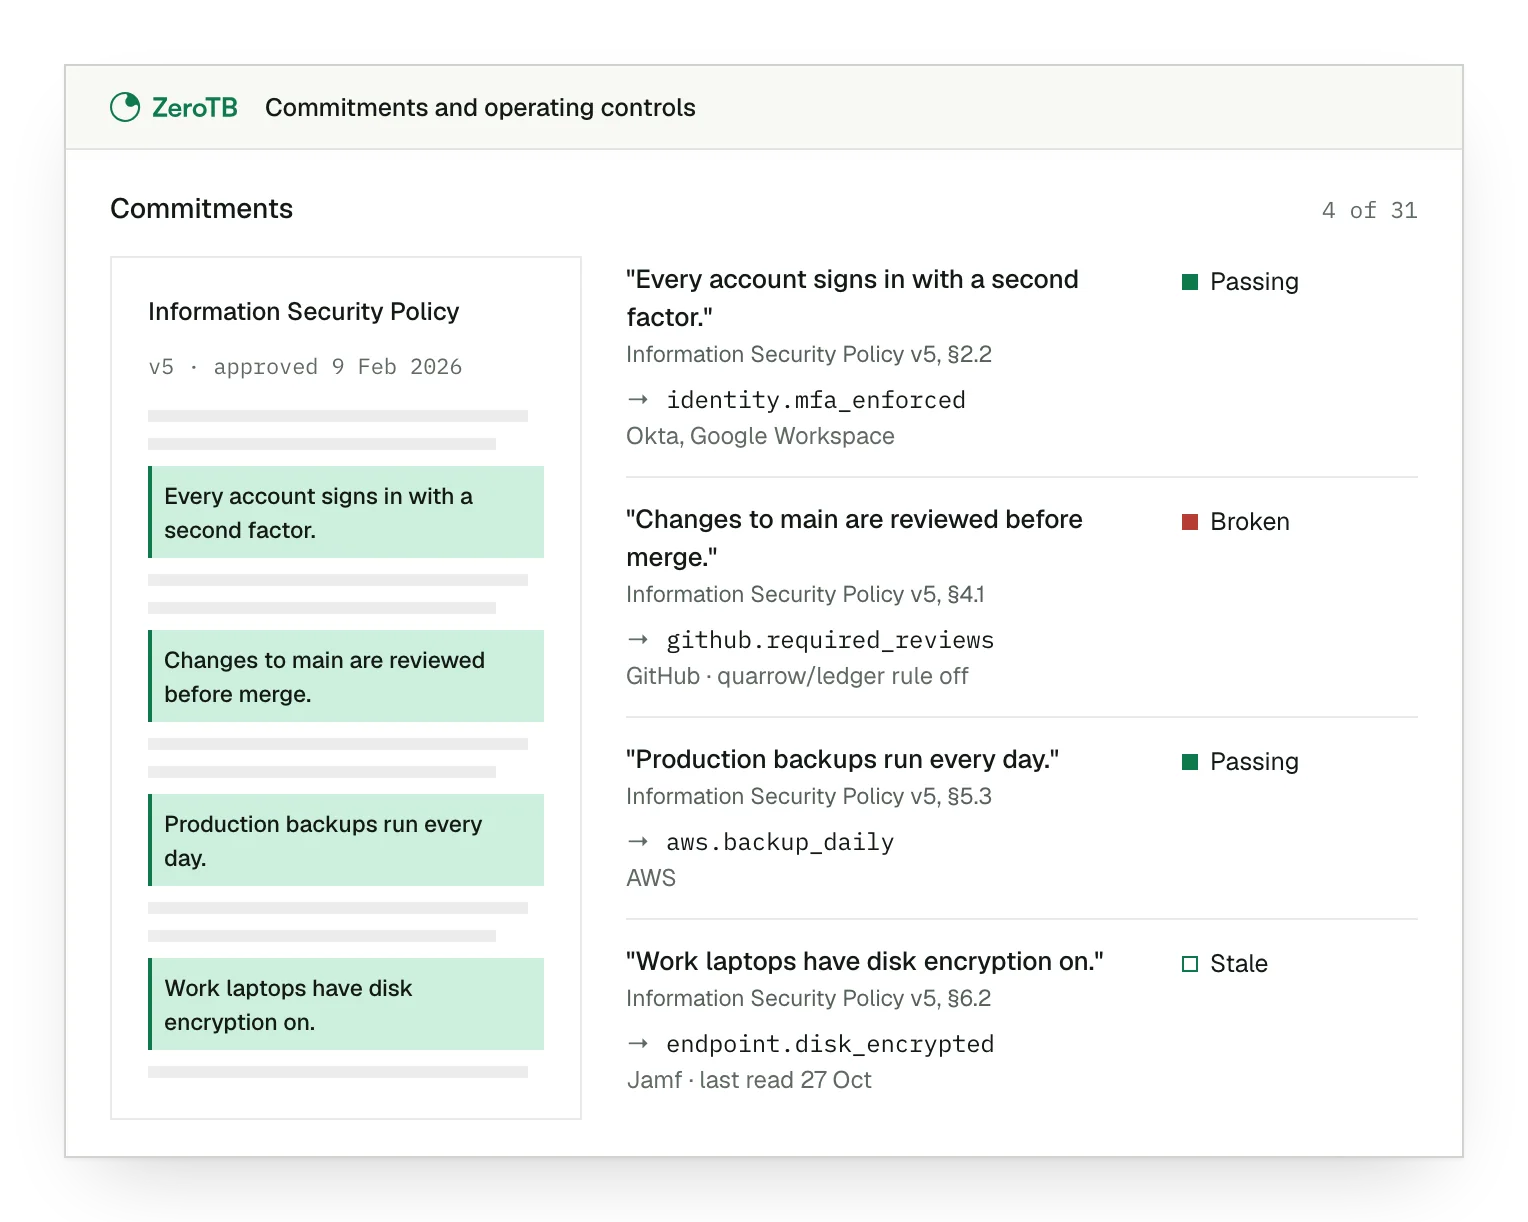
Works with the stack you already run


Control work between audits
A documented control still needs someone to keep it working as systems change. New repositories, changed permissions and cloud settings can leave the original requirement unmet. Compliance and engineering then have to investigate the gap and coordinate the repair while their other work continues.
Requirements enter the report
Systems change after review
Controls drift between audits
Control restoration
ZeroTB carries a commitment from its source clause through to a verified repair. It checks systems against the approved requirement and drafts a fix. People authorize material actions; ZeroTB checks the resulting state before closing the work and preserves the evidence.
Checks follow the company's own approved commitments
Each control gap has an owner
Missing observations remain visible as unknown
Controls across the company
ZeroTB checks branch rules, required reviews and cloud settings against the commitments that govern software delivery.
ZeroTB checks approved accounts, access permissions and device baselines against the requirements for using company information.
ZeroTB schedules training, vendor reviews and incident exercises from commitments, assigns owners and verifies completion.
Example of blocking personal account access while preserving work access
The Verified Control Record shows compliance what changed and why the repair satisfied the requirement. This example concerns work accounts and device protections. The record retains the policy clause, the failure and the verified result, with a signature and a portable copy for the auditor.
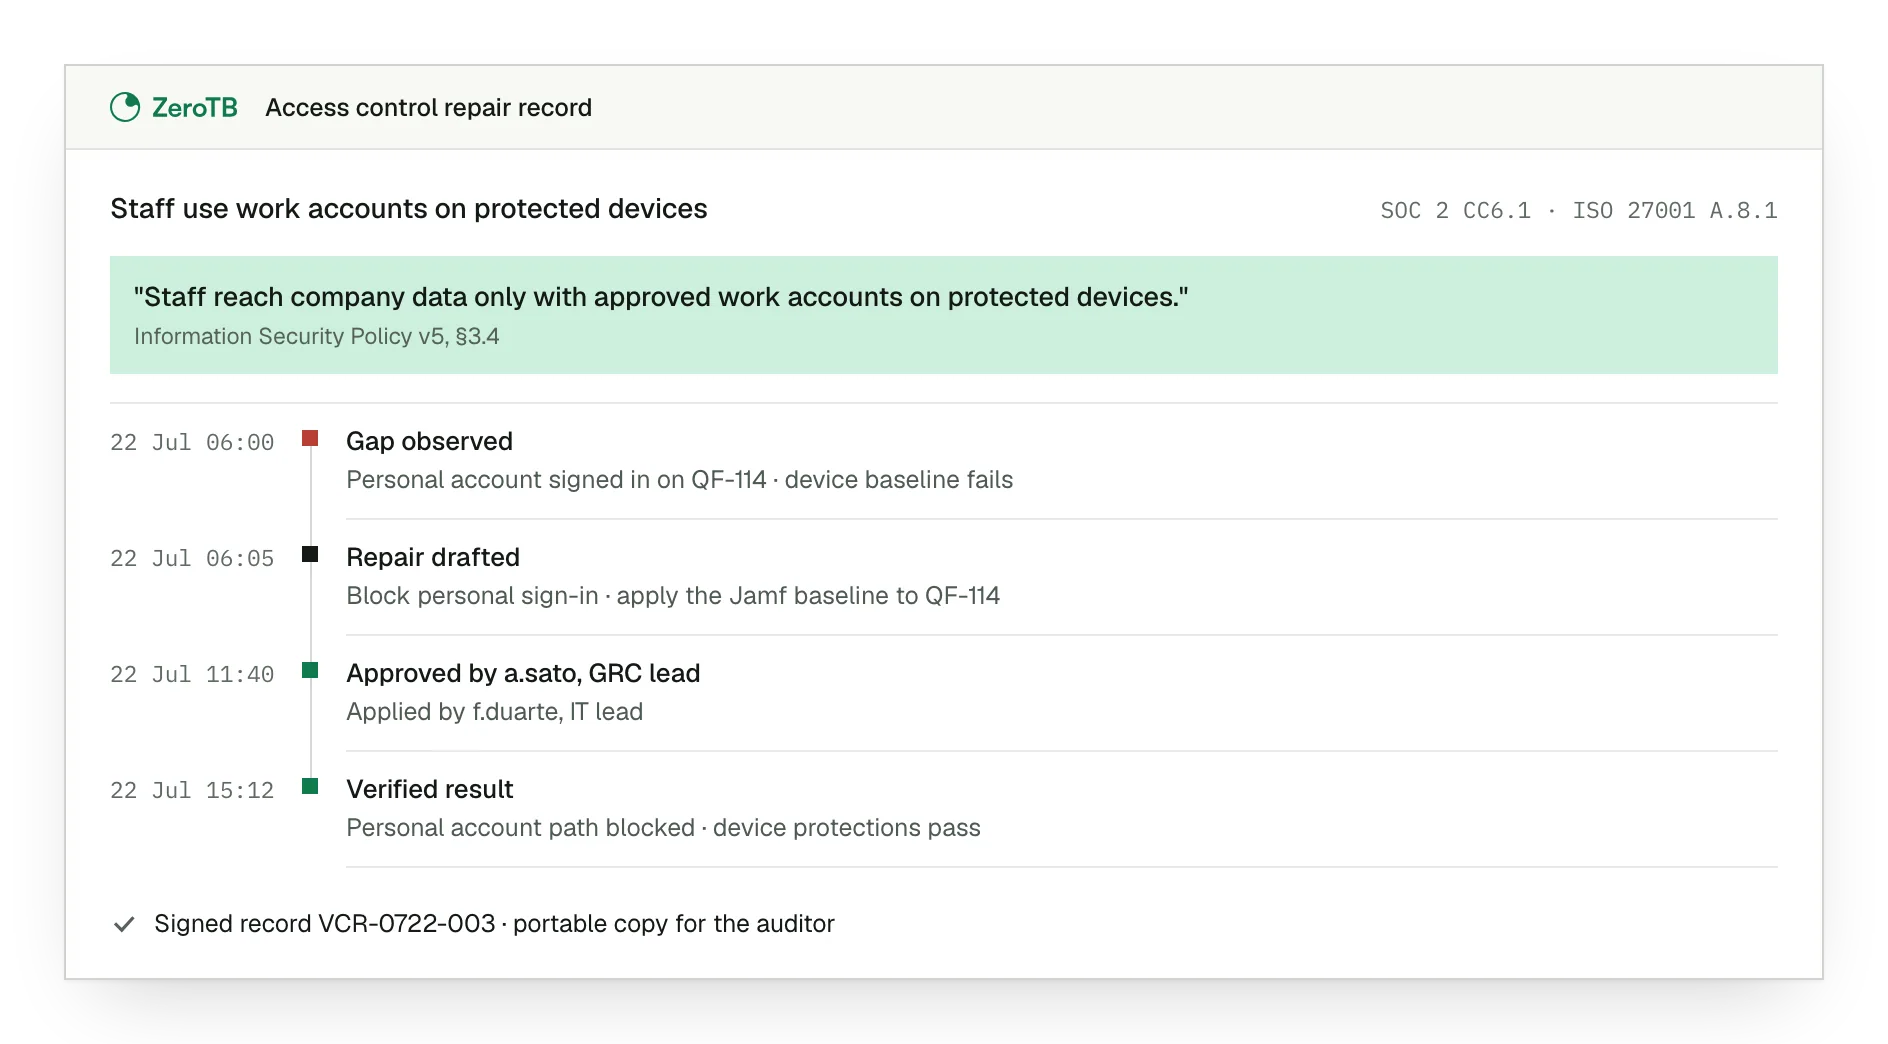
Source requirement. The company requires staff to use approved work accounts on protected devices.
Observed gap. The device has an active personal account and does not meet its security baseline.
Verified result. The check confirms that the personal account path is blocked and device protections now pass.
Compliance engineering support
Our team brings experience running security and IT in healthtech and taking companies through SOC 2 and ISO 27001. With Control operations, ZeroTB handles the continuing work of maintaining controls as the company changes, alongside your compliance and engineering teams.
ZeroTB keeps commitments, checks and repair evidence together
Engineers retain approval of material changes
Auditors can inspect records directly in ZeroTB
Talk to our team
Talk with us about the control work that falls between compliance and engineering, and where your team needs support.
FAQ
Can we use ZeroTB alongside our existing control scripts?
Yes. An existing script may already support a requirement in your report. ZeroTB checks the resulting system state against that requirement. Where a gap remains, our team investigates it and proposes a repair.
Can this help when coding agents change our development systems?
Yes. Agents can change the code, configuration or access that a control depends on. ZeroTB examines branch rules, delivery checks and required reviews as part of that work. See our coding-agent compliance solution for the development-specific coverage.
Can the same control support more than one framework?
Yes. One access control, for example, can support requirements in SOC 2, ISO 27001 and HIPAA. ZeroTB uses your reports and policies to establish those connections. Restoring that control can then satisfy the requirements that share it.
What permissions would we grant at the start?
Read-only access comes first. You can grant and revoke write permissions separately for each class of action. Pull requests are the default for material changes; your engineers review and merge them through their development workflow.
How do you handle repairs that cannot use a pull request?
ZeroTB can propose a runbook for a person to execute or an approved API action. Direct API actions require opt-in, must be reversible and are limited to the systems and scope allowed by your policy.
Who decides when an exception is acceptable?
Your team decides which exceptions are legitimate. AI can interpret a requirement and investigate a gap, but people confirm the commitment's meaning and authorize material decisions. AI cannot declare a control healthy or close the work on its own.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. You receive working controls and portable evidence from the repairs, with our team supporting the work in your systems.