Founder-led control review
Work with our team to resolve the control gaps that remain after an audit. We bring experience in security operations and compliance to the engineering work those repairs need. The founder-led review keeps that work together, with your people deciding which material changes to approve.
Works with the stack you already run


Control work between teams
Control gaps stay open when compliance, IT and engineering have to coordinate every repair. A policy identifies the requirement, but someone still has to investigate the system, arrange the change and establish that it worked. That work continues after the audit.
Compliance identifies a gap
Repair work passes between teams
The control remains unresolved
Experience with operating controls
Our team has run security and IT in healthtech and taken companies through SOC 2 and ISO 27001. We apply that experience to Control review, bringing engineering into the work of maintaining your controls.
Experience running security and IT operations
Direct work with regulated technology companies
Engineering involved in customer delivery
Control review and repair
We read your reports and policies, establish the commitments you approve, and check them against the systems involved.
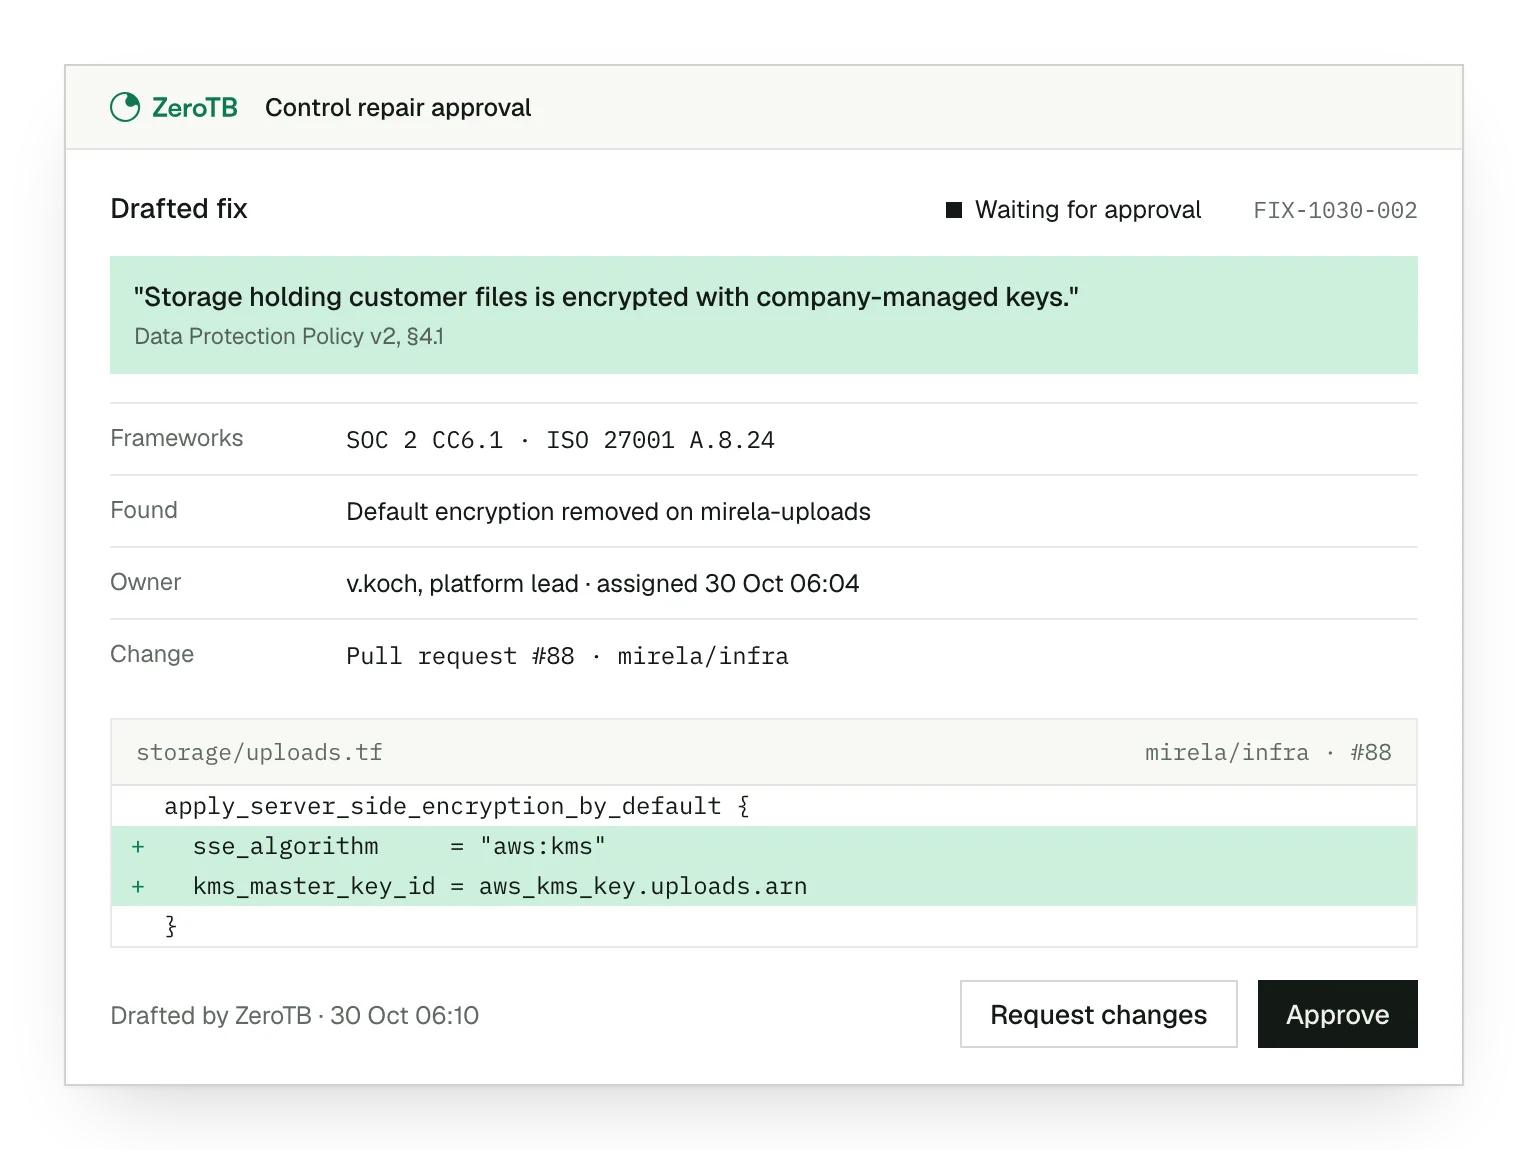
Our team drafts the repair. Your people approve material changes before ZeroTB acts within its granted permissions.
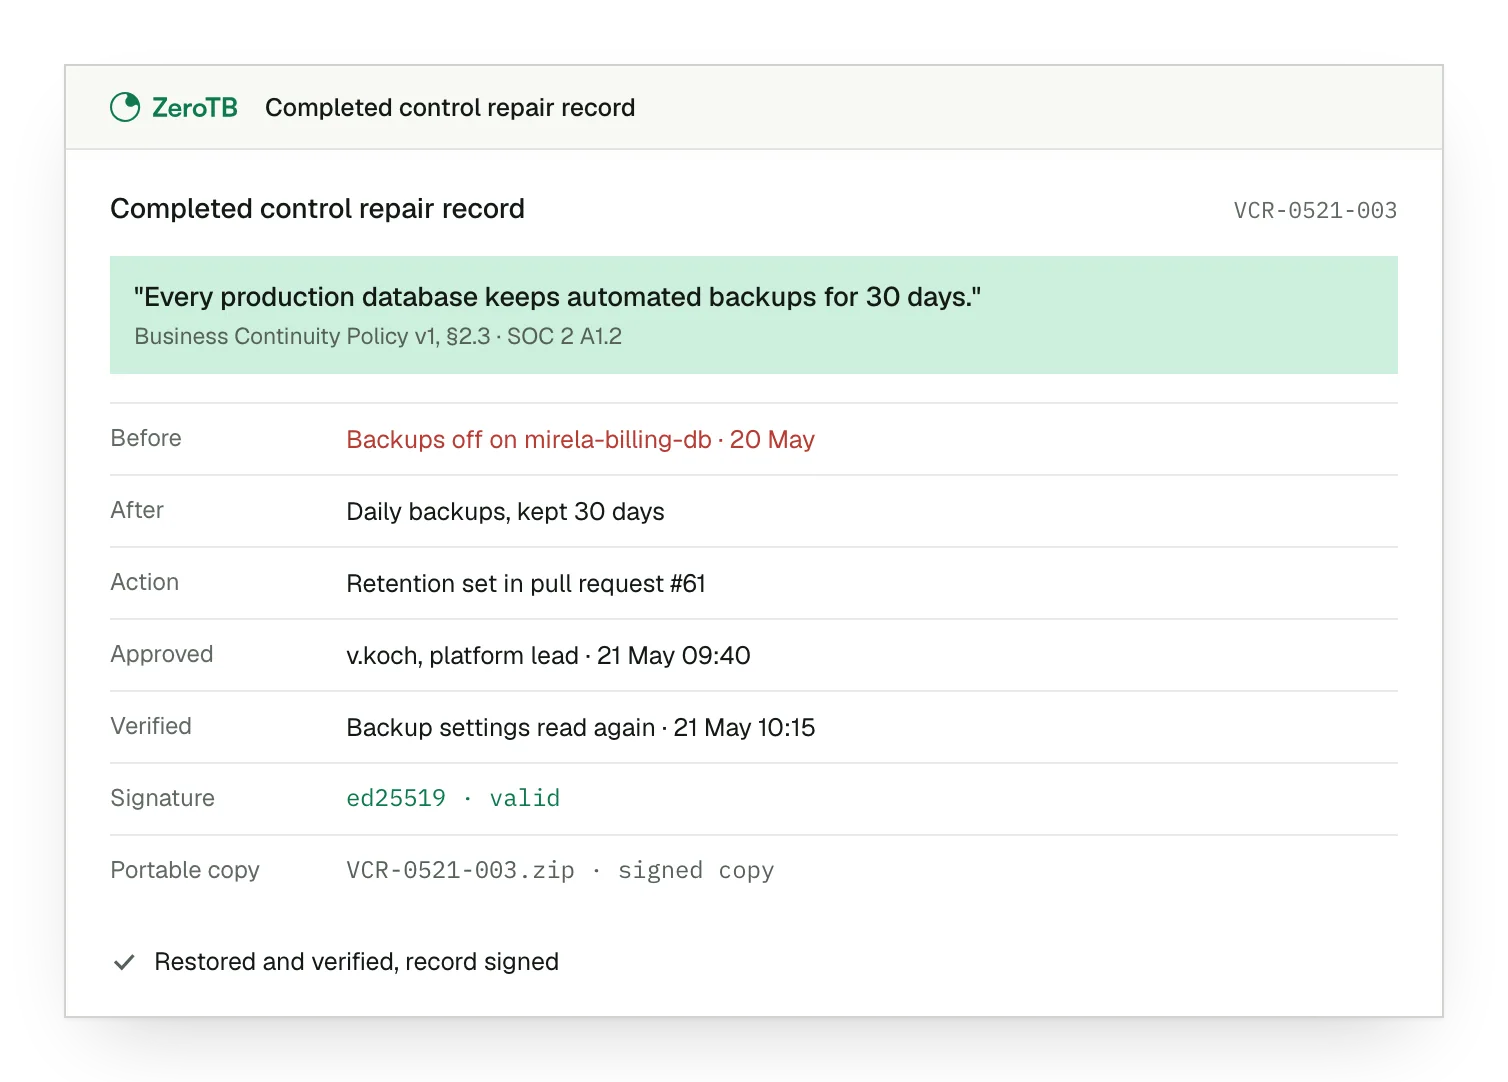
We recheck the affected system before closing the work. The record keeps the result, repair and approval together.
Evidence for compliance reviews
When an auditor asks about completed work, compliance can refer to the signed Verified Control Record. The auditor can read it directly in ZeroTB. Your team can also retain a portable copy for audit review.
Talk to our team
Talk with us about the repairs that keep returning to compliance and where your team needs help with the work.
FAQ
Is this review suitable for a company without a compliance engineering team?
Yes, when your company owns both the requirement and the systems involved. We work with regulated technology companies that need their controls to operate and cannot justify hiring a dedicated compliance engineering team.
Can the review cover controls we have already documented?
Yes. ZeroTB holds the record of commitments for the controls included in the review. ZeroTB works on the controls documented there and returns evidence of completed repairs.
Can the review cover commitments from more than one framework?
Yes. We work with commitments drawn from SOC 2, ISO 27001 and HIPAA. The review follows the controls those commitments depend on, including controls shared by several frameworks.
How much access does an initial review require?
We start with read-only access to observe the systems. Your team can grant and revoke write permissions by action class. Pull requests are the default for material changes; direct API actions need explicit opt-in, a limited scope and a way to reverse them.
Who decides whether an exception is acceptable during the review?
Your team decides. We use AI to help interpret the requirement and investigate what happened. Decisions about the commitment's meaning, legitimate exceptions and material actions remain with the people responsible for your program.
How does the review handle systems with missing observations?
The status shows whether observations are unknown, stale or disconnected. For example, a disconnected system leaves a visible gap in the evidence. ZeroTB needs a check of the system's state to establish health; AI cannot declare it healthy on its own.
What service continues the work after the Pilot?
Control operations continues the checks and repair work between audits. Changes to accounts, devices, code and cloud settings can affect controls during that period. ZeroTB handles the work needed to keep those controls operating.
Start with the Pilot
Start with eight weeks of work on your own controls. In the Pilot, we map up to 25 commitments from your report and take two real gaps through verified restoration. The work leaves functioning controls and portable evidence.