Compliance consultancy services
ZeroTB takes care of recurring control work after your SOC 2 audit. Our team and software check systems, prepare repairs and retain the evidence, reducing the work compliance coordinates across engineering and IT. You can work with your existing adviser while ZeroTB keeps the commitments, checks, repairs and evidence together.
Works with the stack you already run


Control work between engagements
Someone still needs to maintain controls when a consulting project ends. Accounts, devices and code continue to change. If continuing support falls outside the engagement, the internal compliance team has to find someone to investigate each failure and carry the repair through.
The engagement ends
Systems keep changing
Compliance coordinates another repair
Consulting and ongoing control operations
Consultants can assess gaps and implement controls; ZeroTB runs ongoing control work alongside your adviser. A consulting engagement may also include continuing support. The choice depends on who will maintain controls after the audit.
Assessment identifies requirements and current gaps
Implementation puts agreed controls into operation
Continuing support maintains controls as systems change
Control operations
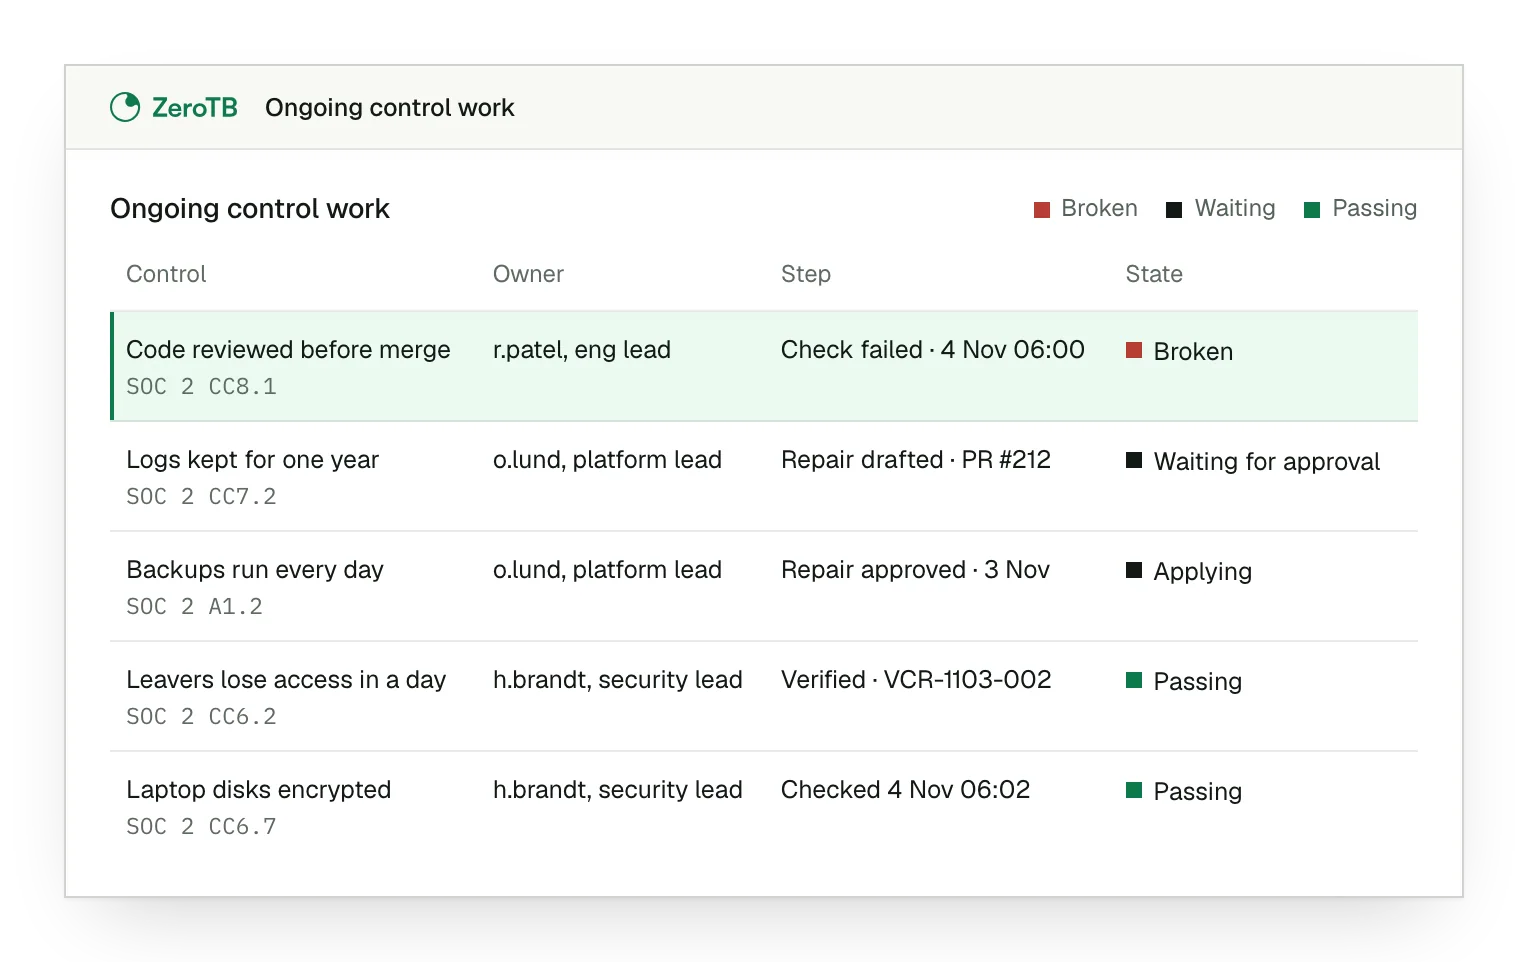
We read reports and policies to identify commitments, then check how systems meet the requirements your team approves.
We investigate a failed control and prepare a repair for approval, assigning an owner to the work.
We check the system after the repair and keep its evidence in a Verified Control Record.
Example of blocking personal account access
The record makes a completed repair available to the people reviewing compliance later. This example concerns access from a personal account on a device with missing protections. It shows the approved restriction and the successful check, with work access preserved.
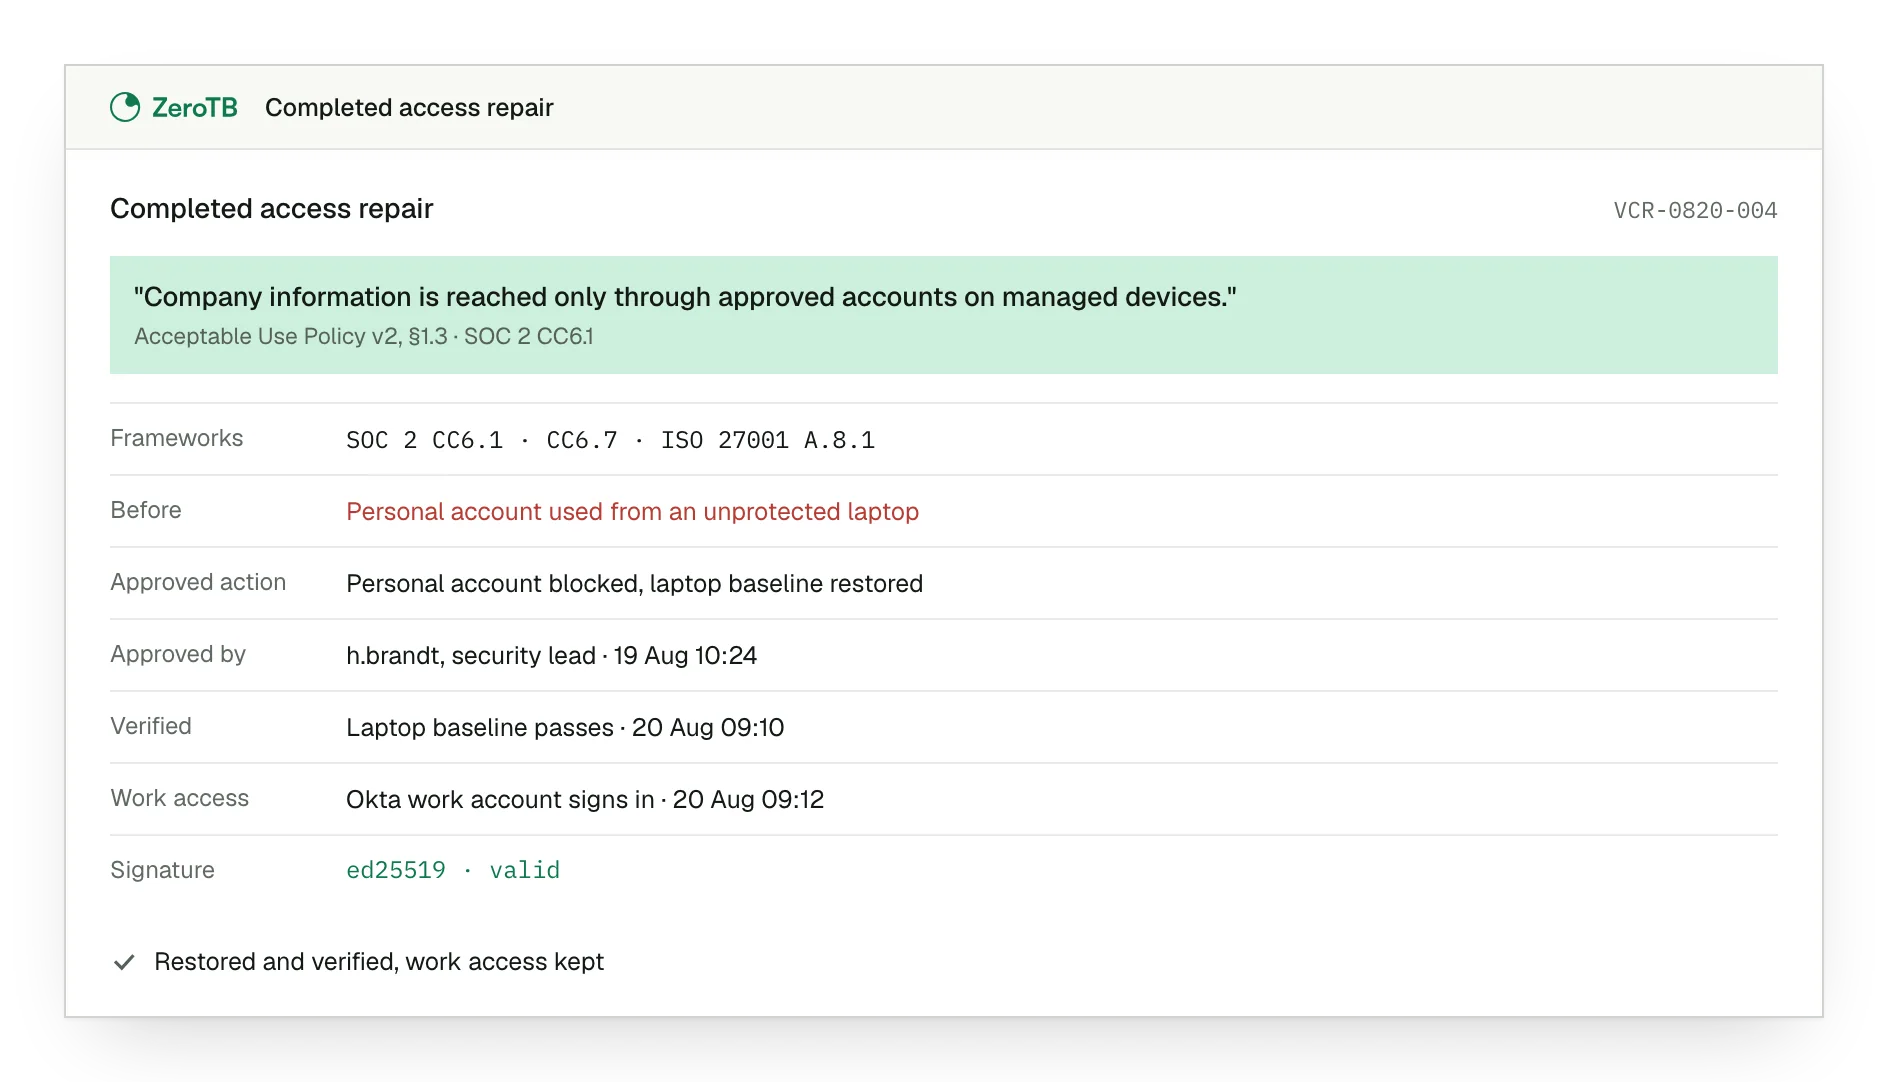
Source requirement. The policy behind this repair requires company information to be accessed through approved accounts on managed devices.
Approved action. The record shows approval for restricting the personal account path and restoring the device protections.
Verified result. The check after the repair confirms the device baseline passes and approved work access still works.
Experience operating compliance programs
Our team has run security and IT in healthtech and taken companies through SOC 2 and ISO 27001. That experience informs ZeroTB's work with regulated technology companies that need controls maintained throughout the year.
Security and IT experience in healthtech
Practical delivery through SOC 2 and ISO 27001
Ongoing control work for regulated technology companies
Talk to our team
Talk with our team about recurring control work, the support you already have and where ZeroTB could help.
FAQ
Can we retain the adviser who helped with our audit?
Yes. Your adviser can continue supporting the programme as ZeroTB takes care of the approved controls. Decisions about what a requirement means, material changes and legitimate exceptions remain with your company.
Where would ZeroTB keep the records of our control work?
Your control records stay in ZeroTB. It keeps commitments and repair evidence together, with portable copies available to retain with other programme material. Auditors can also read completed repair records directly in ZeroTB.
Can the same work support our ISO 27001 or HIPAA commitments?
Yes. A control may serve more than one framework. ZeroTB follows the requirements in your approved SOC 2, ISO 27001 and HIPAA commitments. Where they share a control, the same repair can support each requirement.
What permissions would we grant for the initial review?
Read-only access comes first. Permissions for changes are granted by action class and can be revoked. Direct API actions need explicit opt-in, with a limited scope and a way to reverse the action.
How would engineering review a proposed change?
A pull request gives engineers the change to review and merge. That is the default for material changes. Some repairs instead need a runbook executed by a person; ZeroTB supports that route too.
How would we know if a check stopped receiving data?
The status shows where observations are unknown, stale or disconnected. Those states remain visible until there is evidence of the control’s condition. ZeroTB requires a check of the resulting state before it closes the work.
Is there continuing support after the Pilot?
Yes. The Control operations service maintains controls between audits. That includes the work created by changing accounts, devices, code and infrastructure, with ongoing checks and repairs as the company develops.
Start with the Pilot
In the eight-week Pilot, ZeroTB maps up to 25 commitments from your report and takes two real control gaps through verified restoration. The working controls and portable evidence give you a basis for assessing the continuing service.