Compliance as a service
With ZeroTB, you have a team and software to maintain compliance controls after the audit. We take care of checks and repairs across the systems your commitments cover. You get this work done without building a compliance engineering function, with commitments, checks and repair evidence together in ZeroTB.
Works with the stack you already run


Control work between audits
An audit can finish while the work of maintaining controls continues. Accounts change, devices miss required protections and new repositories need rules. Compliance and engineering still have to establish which requirement applies to a gap and whether a repair has restored the control.
Systems and access change
Required protections stop applying
Control gaps need attention
Keeping your commitments working every day
ZeroTB checks your commitments against your systems each day and carries detected gaps through to verified restoration. The same responsibility continues as the company changes.
Confirm requirements
AI identifies commitments in your report and policies for your team to confirm, including scope and required evidence.
Check daily
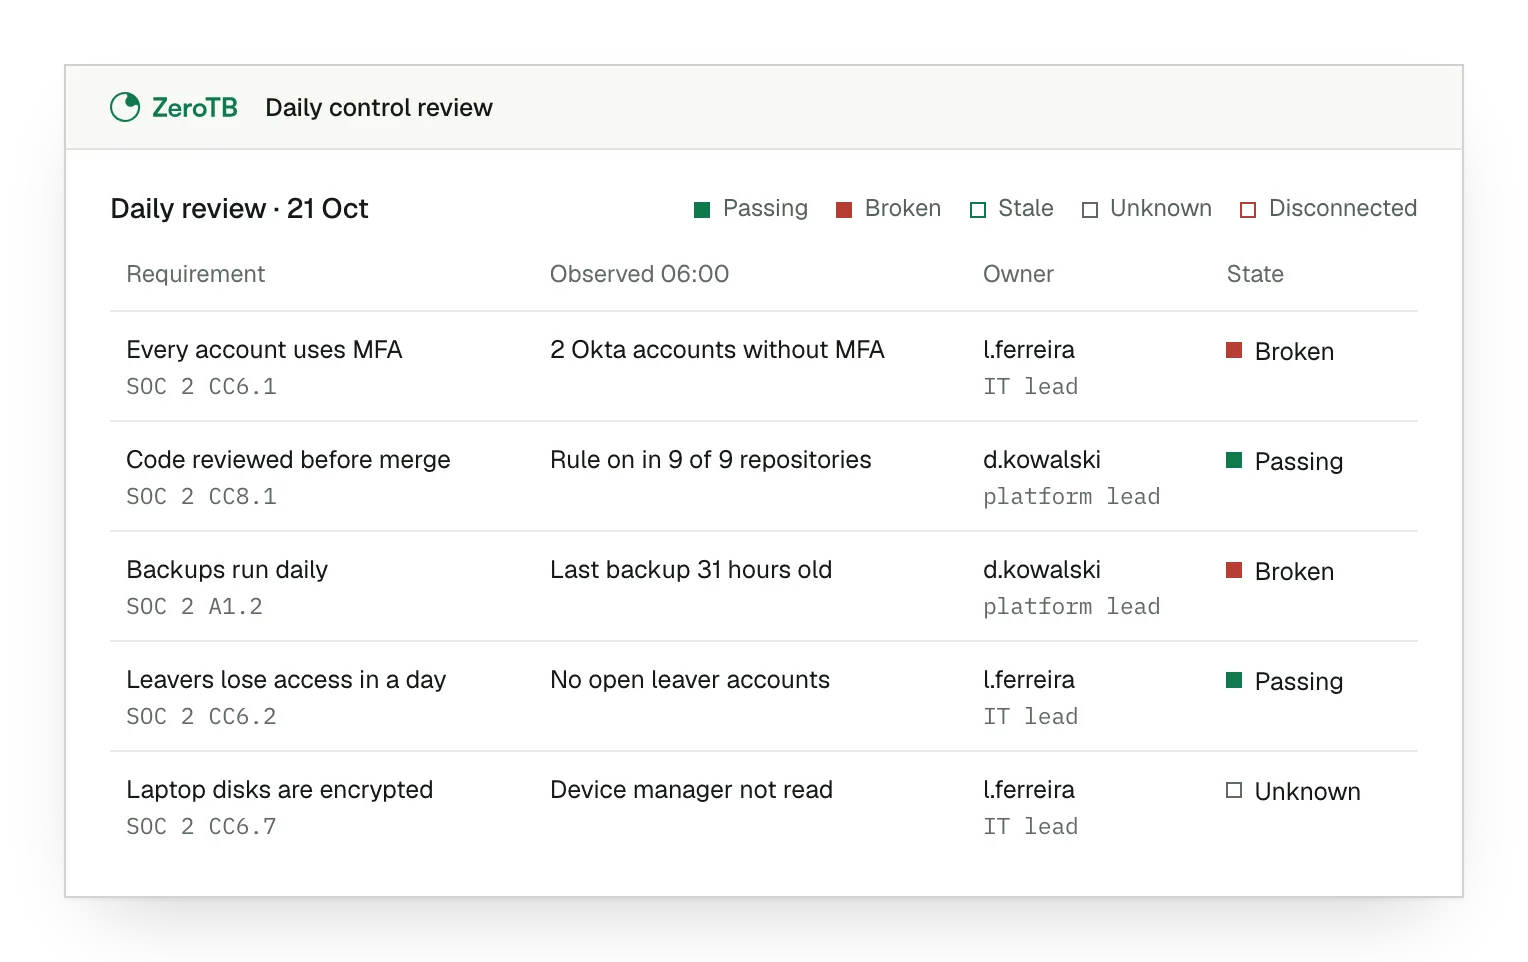
ZeroTB compares requirements with system state daily, showing the source clause, observation and reason for each finding.
Prepare repairs
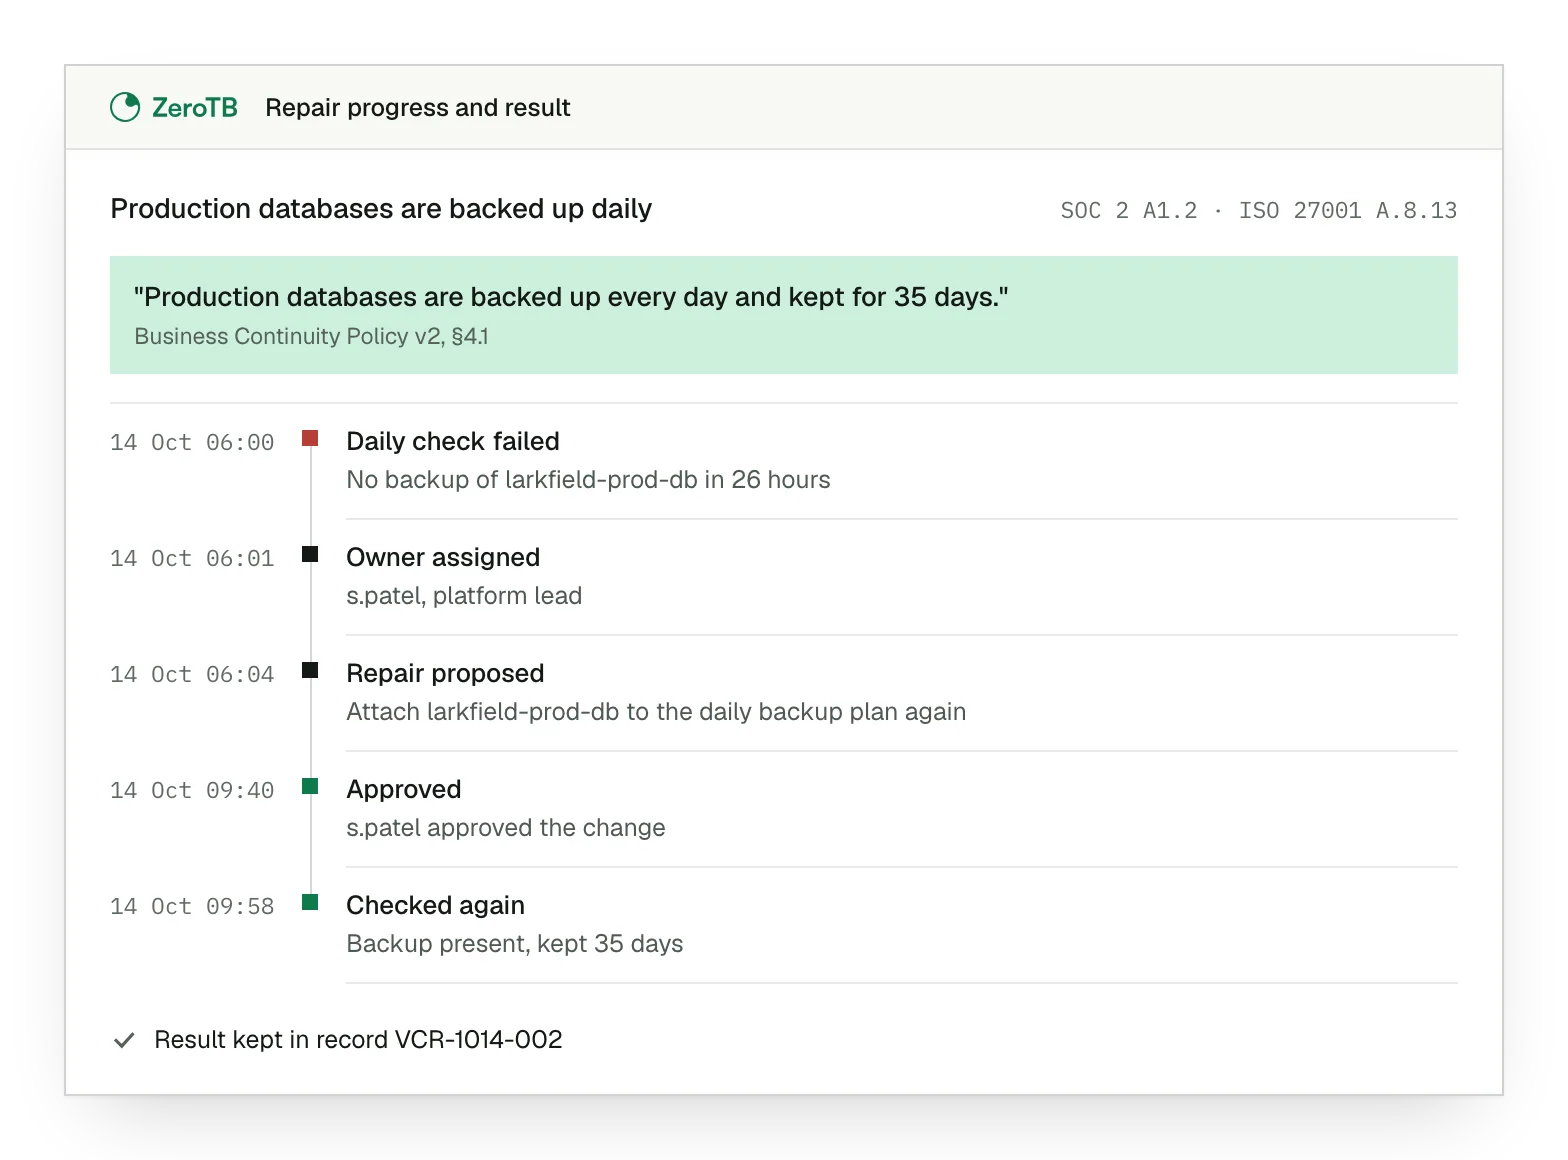
Each gap gets an owner and response window before ZeroTB prepares a runbook, pull request, API action or guardrail.
Authorize changes
Your team authorizes material changes before the responsible person or ZeroTB executes the repair within agreed permissions.
Verify and record
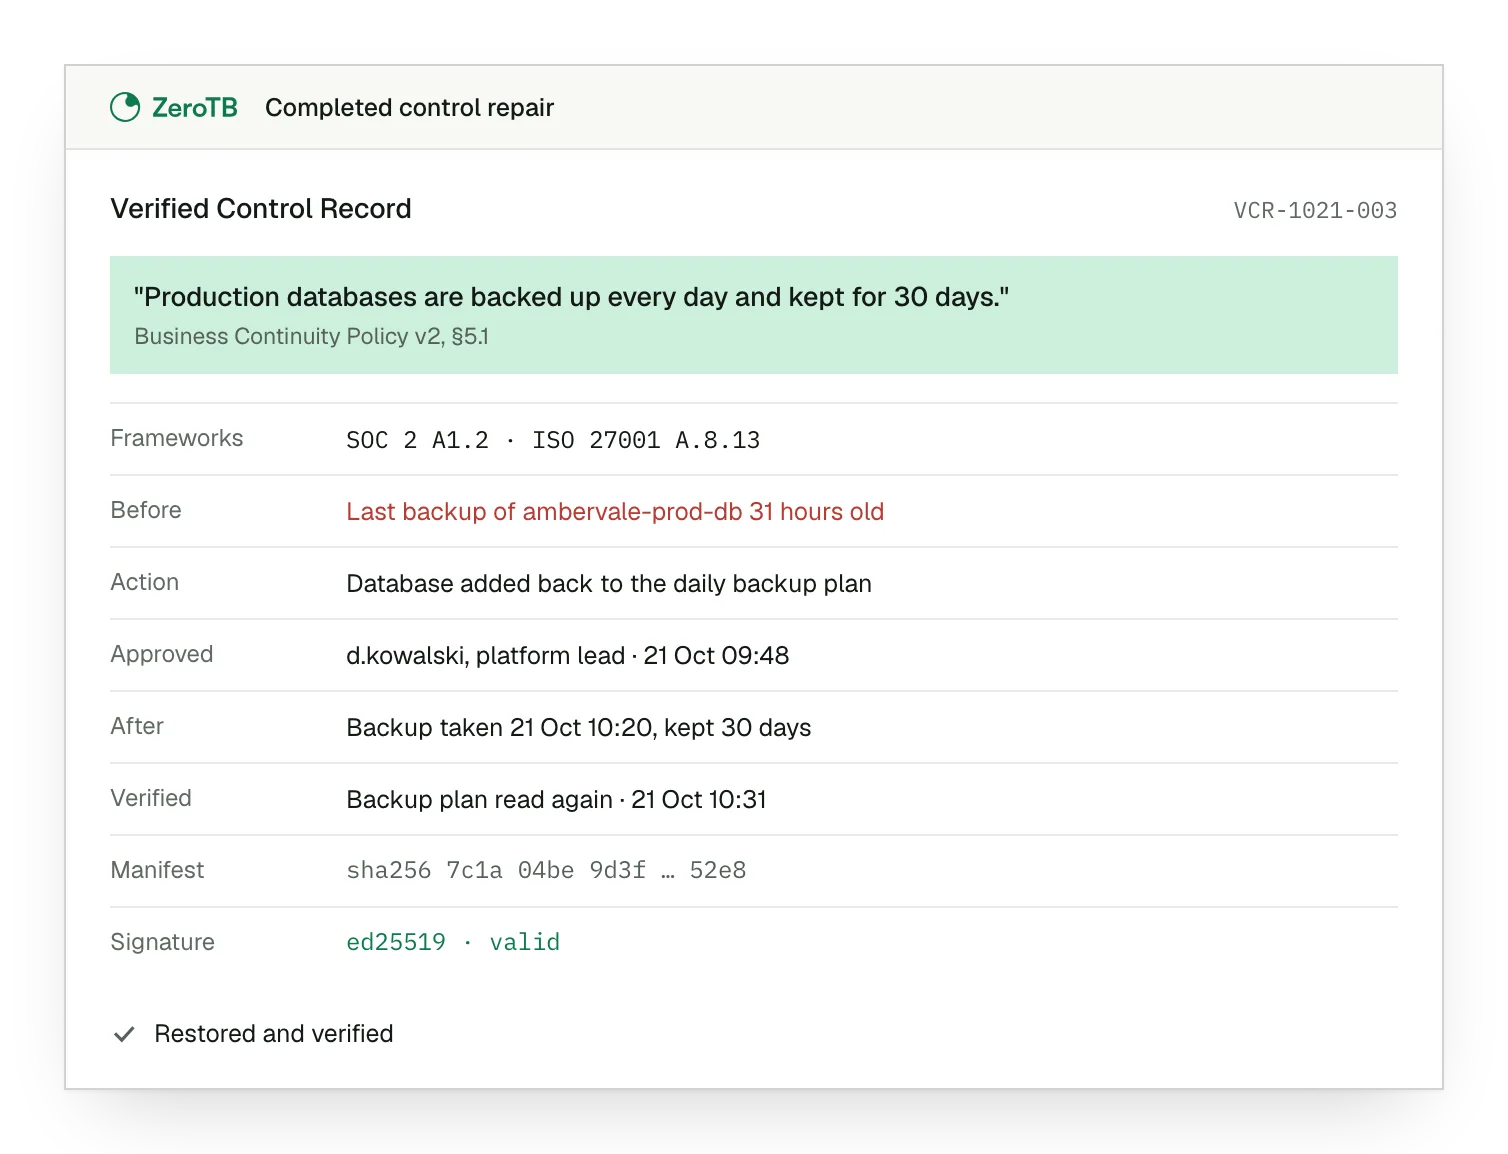
You receive verified restoration and a signed record of the commitment, before-and-after states, action, approval and verification.
Support from compliance practitioners
Our team has operated security and IT in healthtech and helped companies through SOC 2 and ISO 27001. That experience informs Control operations: the continuing work we do with compliance and engineering to maintain the controls in their program.
Experience running security and IT programs
Direct support from our team
Continuing control work after the audit
Work across systems and teams
We check account access and device settings, including whether required protections apply to the laptops people use.
We check required reviews and deployment rules in repositories, alongside cloud settings that must match company policy.
We track required training, vendor reviews and incident exercises through assigned owners, due dates and escalation when late.
Evidence of completed repairs
Completed repairs leave evidence your auditor can read directly in ZeroTB. The signed Verified Control Record contains the commitment, the states before and after the repair, the action, approval and verification. Your team can also keep a portable copy for audit review.
Talk to our team
Talk with us about maintaining controls between audits, the gaps your team encounters and how the service could help.
FAQ
Can the service support us as we add another compliance framework?
Yes. We work from SOC 2, ISO 27001 and HIPAA commitments in your reports and policies. A single control may support several of those requirements. Where the requirements share that control, restoring it can address them together.
Would we need to move our compliance program into ZeroTB?
ZeroTB holds the commitments for the controls we operate. It keeps the commitments, checks, repairs and evidence together as our team operates the controls. You can retain a portable copy of the repair evidence recorded in ZeroTB.
How does the service handle a review that needs a person to complete it?
ZeroTB connects the review to its requirement, assigns a responsible owner and tracks when it is due. If the work is late, ZeroTB escalates it. Completion must be verified before the control counts as restored.
Who decides how a policy applies to our company?
ZeroTB identifies commitments in your reports and policies for your team to review. Your people confirm their meaning and decide which exceptions are legitimate. That decision establishes the requirement against which ZeroTB checks the relevant systems.
Does using the service require broad write access?
We start by observing systems with read-only access. Write permissions come separately: your team grants them for a defined class of action and can revoke them. For material changes, the default is a pull request your team reviews and merges.
Can the service handle repairs outside a pull request?
Yes. For some gaps, a runbook gives a person the steps to perform the repair. A direct API action is another option when your team opts in. Those actions must have a limited scope and be reversible.
How will we know if a connected system stops providing evidence?
ZeroTB shows unknown, stale and disconnected states when observations are missing or out of date. A healthy status requires a supporting check. AI cannot declare the control healthy or close the work by itself.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. You receive working controls and portable evidence to evaluate the service in your own systems.