Coding-agent compliance drift
ZeroTB keeps compliance controls operating as coding agents change your systems. Our team has run security and IT in healthtech and taken companies through SOC 2 and ISO 27001. Your team can keep developing software with support for the control work that follows changes to code, configuration and access.
Works with the stack you already run


More changes between compliance checks
Coding agents increase the number of changes that can affect compliance controls. Code, cloud configuration and access can change between observations, leaving systems outside the requirements your company recorded in its reports and policies.
Agents change system settings
Existing safeguards stop applying
Required controls no longer hold
Keeping your commitments working every day
ZeroTB checks your commitments against your systems each day and carries detected gaps through to verified restoration. The same responsibility continues as the company changes.
Confirm requirements
AI identifies commitments in your report and policies for your team to confirm, including scope and required evidence.
Check daily
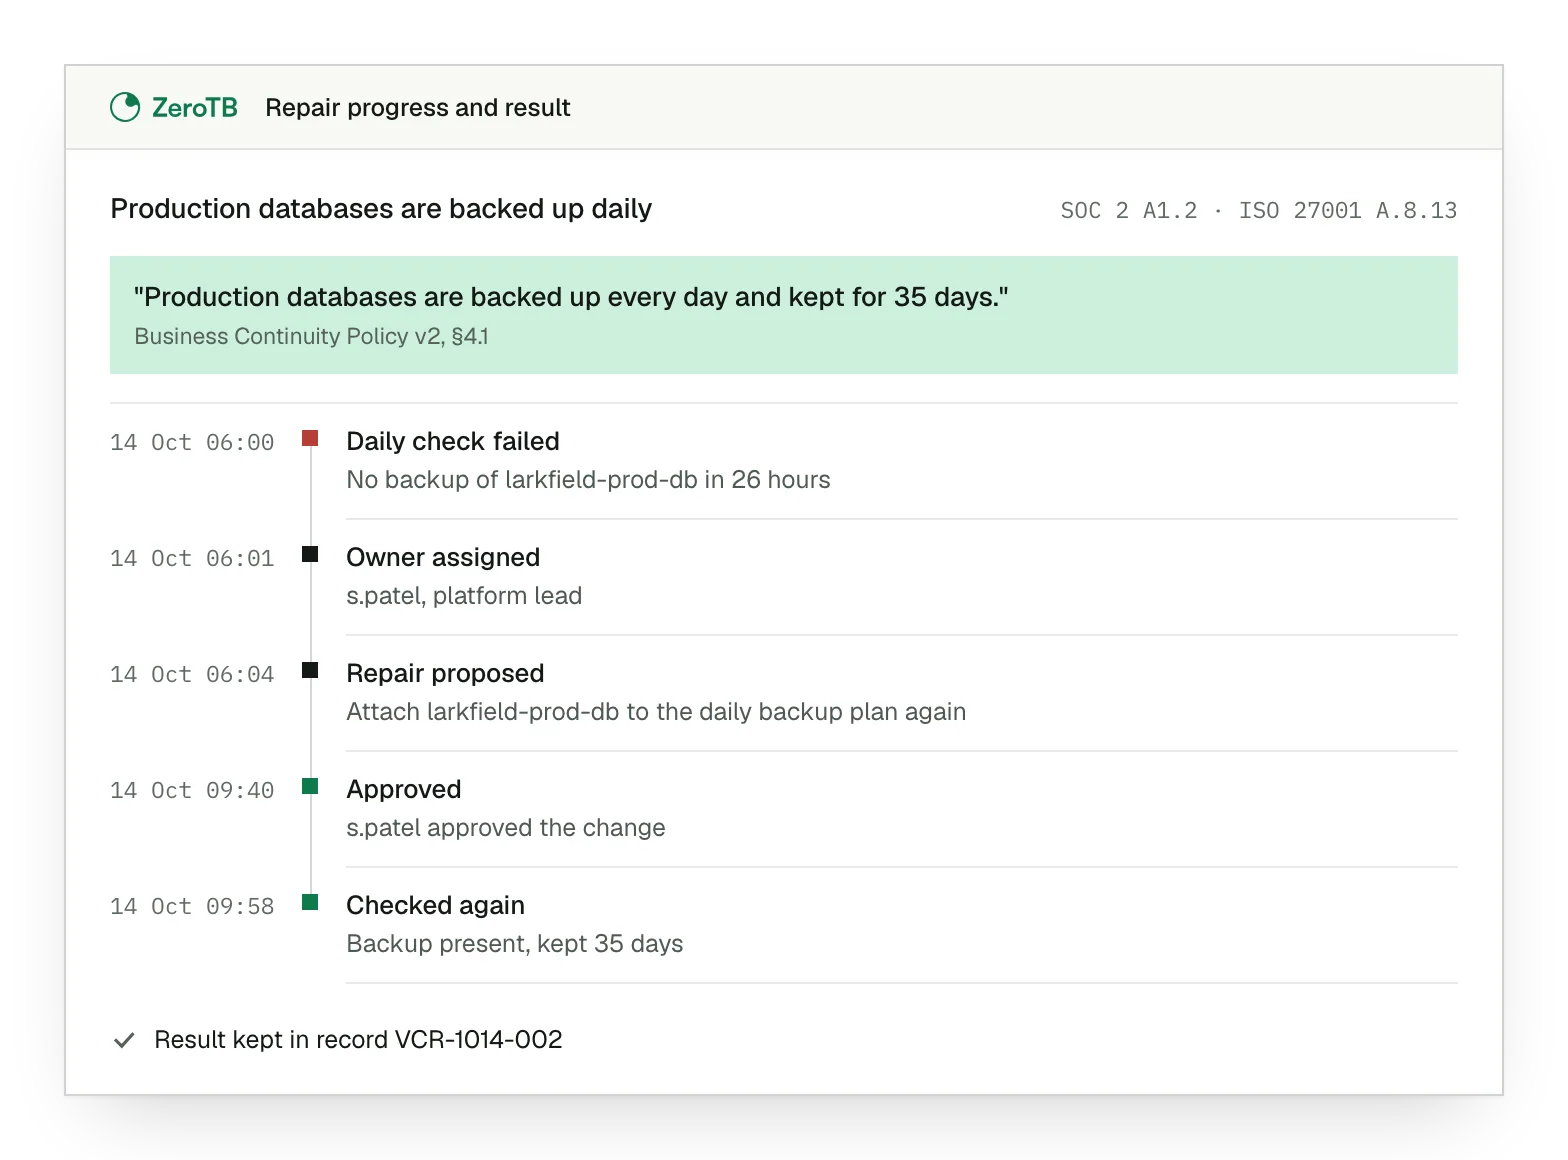
ZeroTB compares requirements with system state daily, showing the source clause, observation and reason for each finding.
Prepare repairs
Each gap gets an owner and response window before ZeroTB prepares a runbook, pull request, API action or guardrail.
Authorize changes
Your team authorizes material changes before the responsible person or ZeroTB executes the repair within agreed permissions.
Verify and record
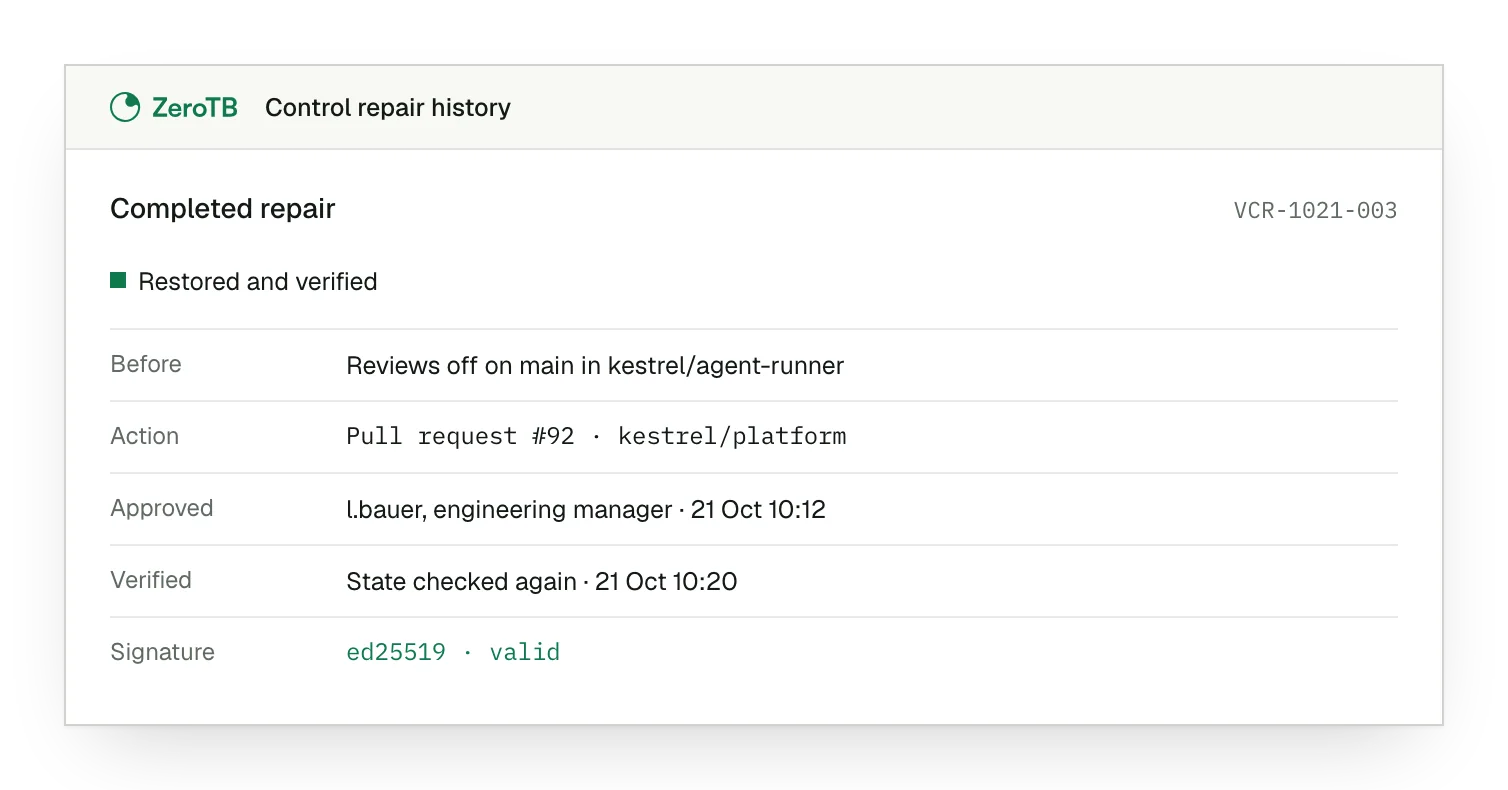
You receive verified restoration and a signed record of the commitment, before-and-after states, action, approval and verification.
Maintaining commitments as development accelerates
ZeroTB helps compliance and engineering maintain commitments without building a dedicated compliance engineering team. Our coding-agent compliance solution covers development, cloud and access changes, so the work reaches across the systems where agents act.
The Pilot starts work on your systems
Control operations covers continuing checks and repairs
ZeroTB keeps commitments, checks and repair evidence together
Repair evidence for the next review
The Verified Control Record lets compliance review a completed repair after development moves on. Your auditor can inspect it in ZeroTB, and your team can retain a portable copy. It records that repair's result; later repository or cloud changes still need their own control checks.
Preventing repeat failures as agents work
ZeroTB can propose preventive guardrails to keep a repaired control operating as agents make further changes. The response fits the requirement and the affected system, so protections remain tied to the development path your company has approved.
Branch rules enforce required code reviews
Delivery gates enforce required tests
Daily observations show whether protections still operate
Talk to our team
Talk with our team about compliance work created by agent changes to repositories, cloud configuration and access.
FAQ
Can compliance need attention even when the delivery pipeline passes?
Yes. A delivery pipeline can still pass while a separate compliance requirement is unmet. Which checks matter depends on the commitments your company made and the systems those commitments cover.
How do we decide whether a policy applies to an agent's change?
Your team confirms the commitment's meaning, scope, owner and expected evidence. That connects the policy clause to the affected system before ZeroTB treats it as an enforced requirement.
Does ZeroTB need write access to inspect development controls?
ZeroTB starts with read-only access. Your team grants write permissions separately by action class and can revoke them. Direct API actions require opt-in, limited scope and a way to reverse them.
Can engineers use a runbook when a pull request is unsuitable?
Yes. A runbook that a person executes is one supported response to a control gap. The response depends on what the requirement needs and how the affected system can be changed.
Who can accept an exception for an agent-driven change?
People retain responsibility for legitimate exceptions. AI can interpret the policy and investigate the gap; your team decides what the commitment means and which material actions to authorize.
What if a repository connection stops supplying observations?
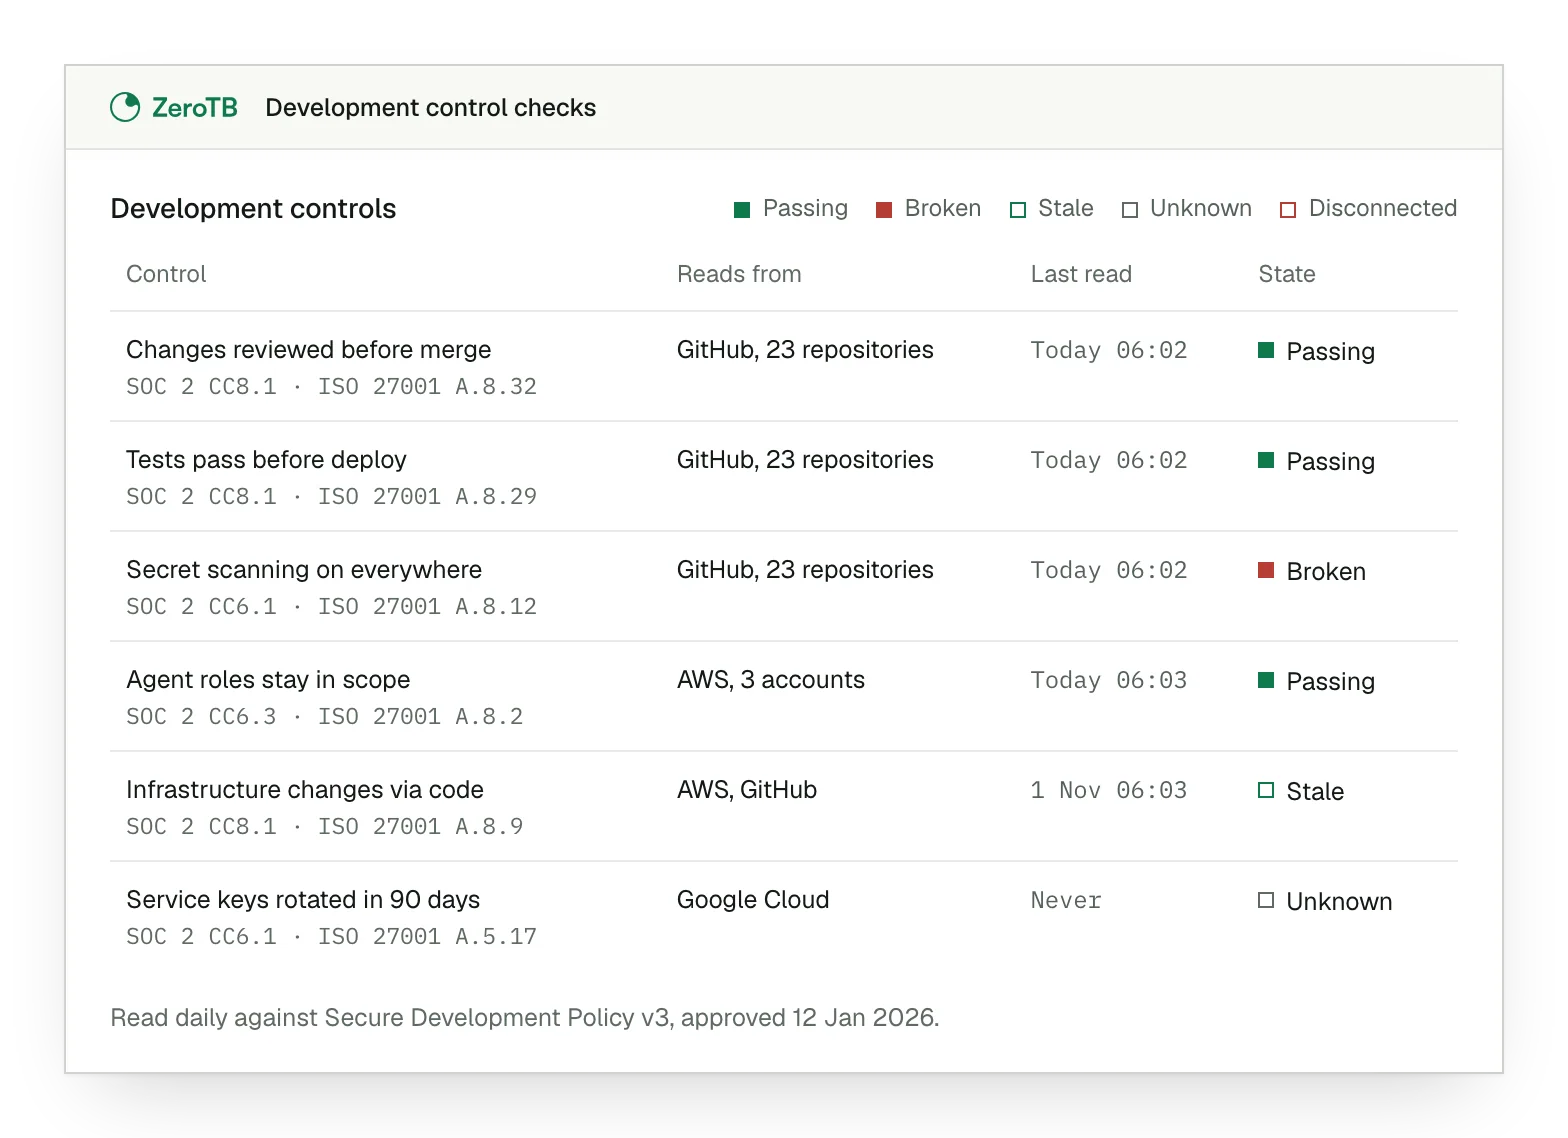
ZeroTB shows unknown, stale and disconnected states. Missing observations remain visible, and a healthy status requires a check that supports it. A lost connection cannot establish that a control works.
Can AI close a development-control finding on its own?
No. AI can propose a conclusion, but it cannot declare the control healthy or close the work on its own. ZeroTB must verify the resulting state.
Can engineers inspect why a development control failed its check?
Yes. ZeroTB shows the source clause, the observed system state and its conclusion. Engineers can inspect the relationship between the written requirement and the condition that needs attention.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. Your team receives working controls and portable evidence to assess ZeroTB's approach in your own systems.