Audit readiness
ZeroTB keeps compliance controls working between audits, so your team can stay ready for the next review. We use your SOC 2, ISO 27001 and HIPAA commitments to check systems and repair gaps with your approval. Compliance gets evidence of those repairs as the work is completed.
Works with the stack you already run


Gaps between audit preparations
Controls can stop meeting a requirement while the last audit's evidence stays unchanged. People leave, permissions change and new repositories appear. When those changes go unchecked, compliance has to investigate the gaps during the next round of audit preparation.
Systems change after the audit
Control gaps go unchecked
Audit preparation reveals unfinished repairs
Keeping controls ready for review
ZeroTB turns approved report and policy commitments into daily checks of the systems they cover.
Our team investigates gaps and proposes repairs, with an owner for each gap and human approval for material changes.
ZeroTB verifies the resulting state before closing a repair and keeps a signed record of the work.
Example of restricting access to approved work accounts
The Verified Control Record gives an auditor the evidence behind a completed repair. In this access example, it shows that the unauthorized account path has closed and approved work access remains available. The auditor can read the record in ZeroTB.
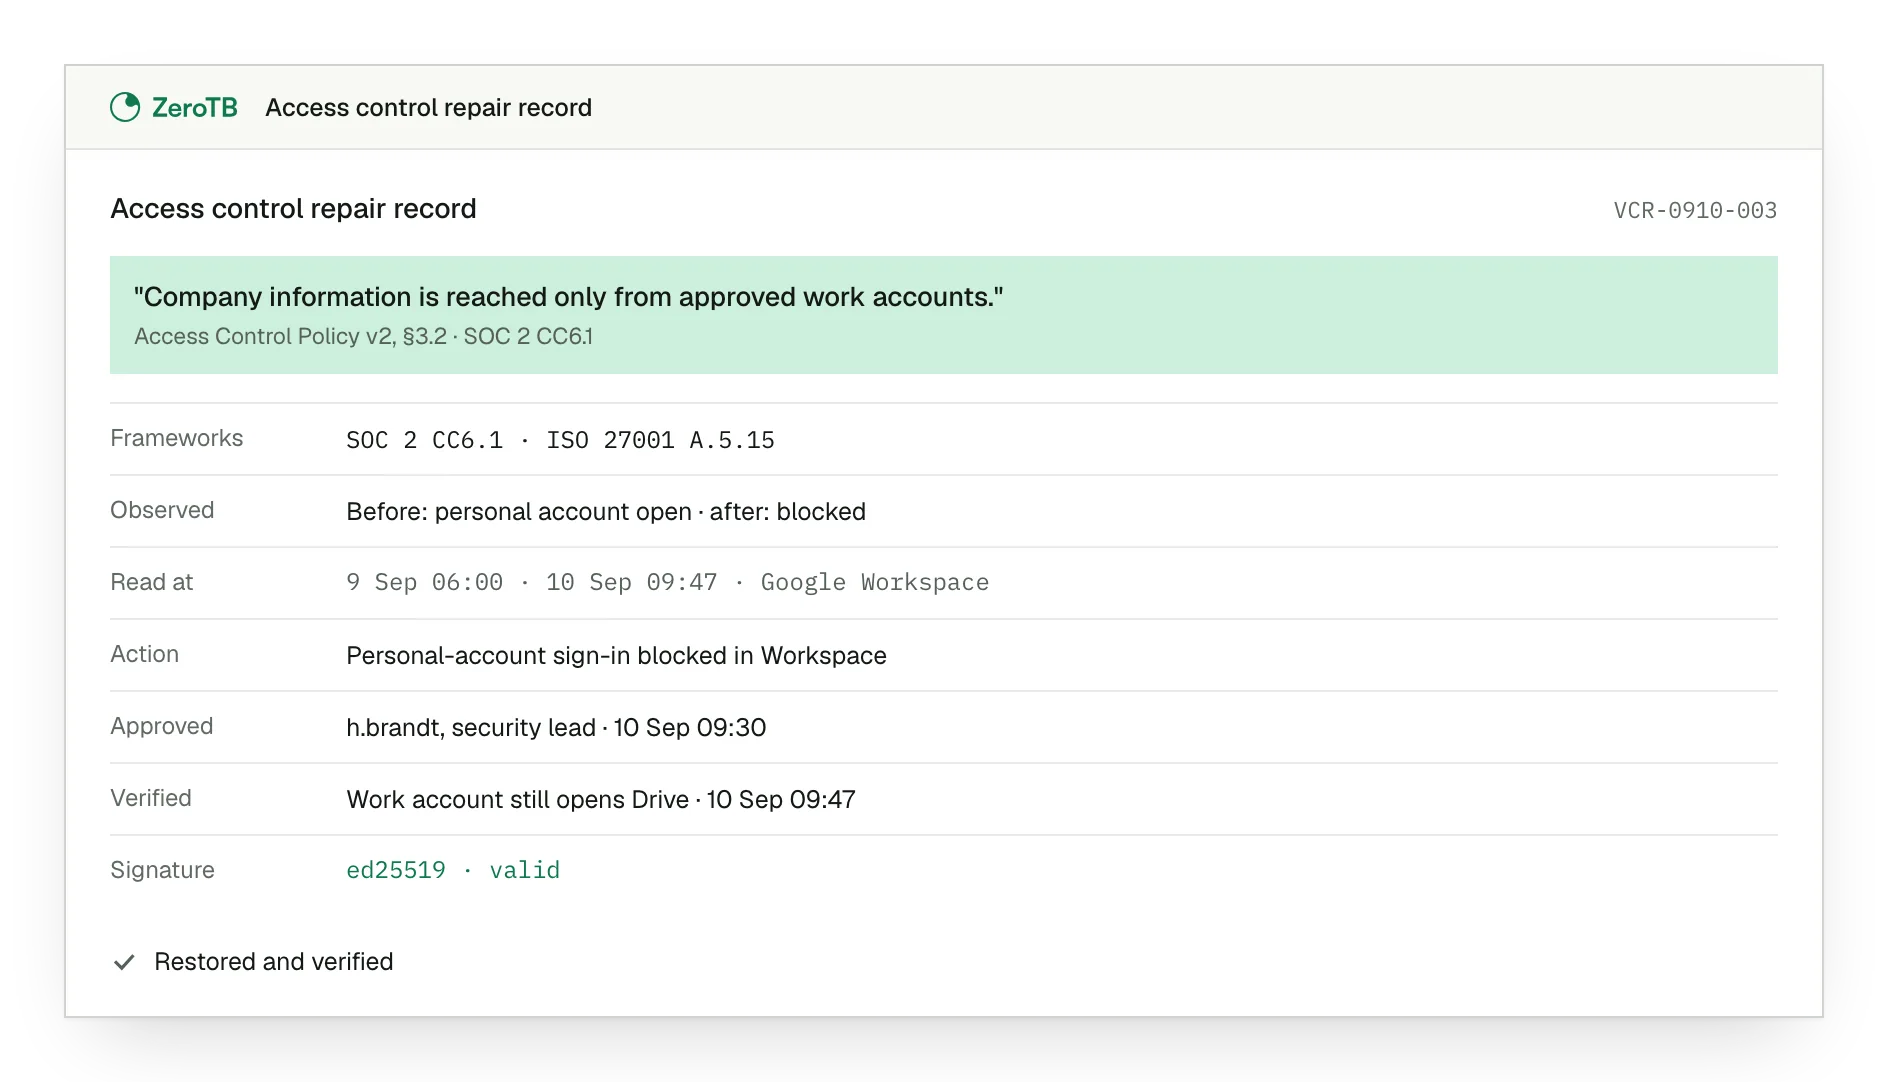
Source requirement. The policy clause establishes which work accounts are allowed to access company information.
Observed change. Observations from before and after the repair show how the access condition changed.
Approved action. The action, its approval and the final check stay together for the reviewer to inspect.
Shared controls across frameworks
Several framework requirements can depend on the same control. ZeroTB connects that control to your SOC 2, ISO 27001 and HIPAA commitments. A repair can then support more than one program, with evidence that shows which requirements it satisfies.
A single control can serve several programs
Each requirement keeps its source clause
Compliance can keep a portable evidence copy
Talk to our team
Talk with our team about staying ready between audits and the repairs that keep returning to your compliance team.
FAQ
Is ZeroTB suitable if we only need help passing an audit?
ZeroTB's work continues after an audit, so it fits companies that need help maintaining their controls throughout the year. Our team works from the commitments already in your reports and policies. Those commitments determine what we check and repair.
Do we need to move our compliance program into ZeroTB?
ZeroTB keeps the commitments, checks, repairs and evidence for the controls we operate. ZeroTB checks and repairs the controls your company has committed to operating. The evidence is portable, so compliance can retain a copy of each completed repair record for audit review.
Can ZeroTB track review tasks as well as technical settings?
Yes. For a vendor review, training requirement or incident exercise, ZeroTB schedules the task, assigns it and escalates it when late. It also checks that the work was completed. Coverage extends to endpoints, identity and access, development and cloud infrastructure.
How can we spot evidence that is too old to rely on?
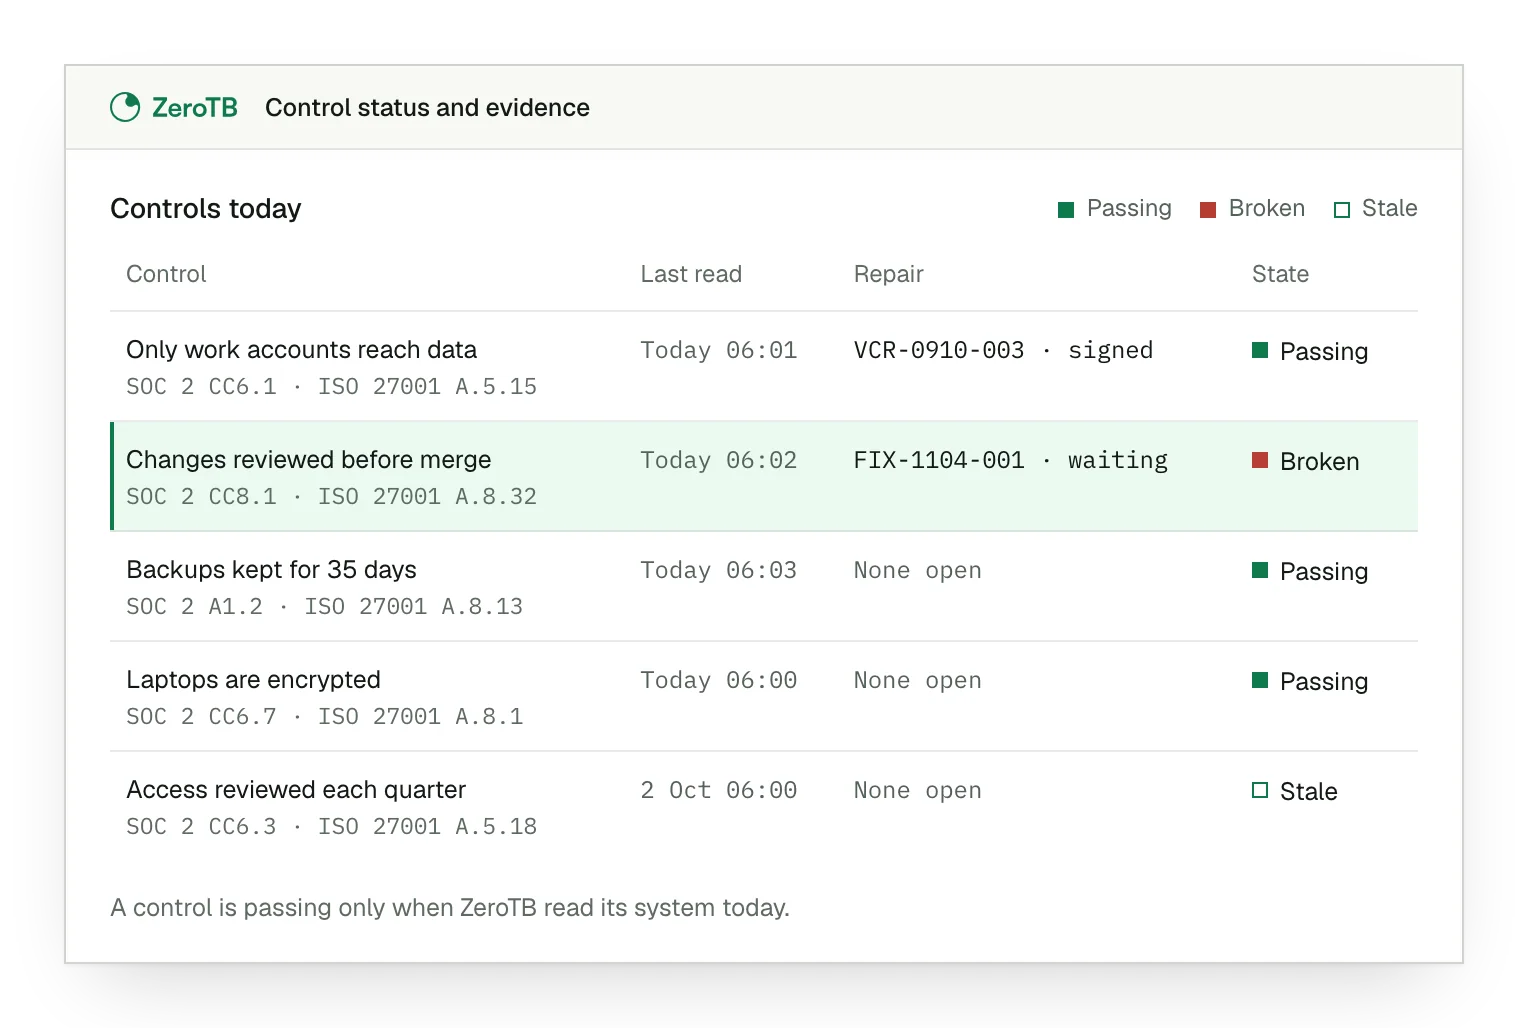
Stale, unknown and disconnected states are visible in ZeroTB. Compliance can see when an observation is missing or no longer current. A conclusion proposed by AI cannot, by itself, close the work or establish a healthy state.
How are proposed repairs reviewed before they affect production?
We normally propose material changes as pull requests for your team to review and merge. If you opt into direct API actions, those actions have limited scope and must be reversible. People decide which material actions and exceptions to approve.
Can the initial review begin without permission to change systems?
Yes. Read-only access lets ZeroTB observe the controls at the start of the work. Any later write permission applies to a particular class of action. Your team decides which of those permissions to grant and can revoke them.
Start with the Pilot
The eight-week Pilot maps up to 25 commitments from your report and takes two real control gaps through verified restoration. The completed repairs give your team operating controls and portable evidence for its compliance program.